Accessibility Service

AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
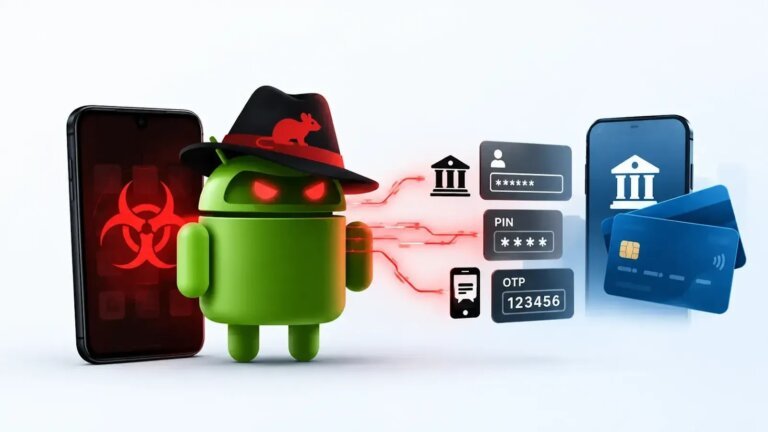
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
AppWizard
June 27, 2026
- Arabic Through Humor is a language learning app that uses humor to help users retain vocabulary and grammar while learning Arabic. - Hidden Touch Button allows users to access various functions of their device from the selfie-camera area through a discreet touch. - An accessibility service app provides real-time transcription and sign language interpretation for deaf and hard-of-hearing users to enhance communication. - An open-source document scanner app enables users to digitize, edit, and organize documents on Android devices, promoting productivity and sustainability.
AppWizard
June 17, 2026
Security researchers at Zimperium have identified a new Android banking trojan named “Rokarolla,” which threatens users of over 200 banking and cryptocurrency applications. It is distributed through spoofed websites, third-party app stores, and social media, but has not been found on the Google Play Store or other official Android repositories. Rokarolla requests extensive permissions, particularly concerning Accessibility services, SMS, calls, and notifications. Its capabilities include accessing WhatsApp contacts, capturing keystrokes, recording the screen, blocking incoming calls, and sending screenshots. Zimperium has not specified which geographical areas may be most vulnerable or the estimated number of potential infections. Users are advised to download applications only from official repositories to reduce the risk of encountering this malware.
AppWizard
May 28, 2026
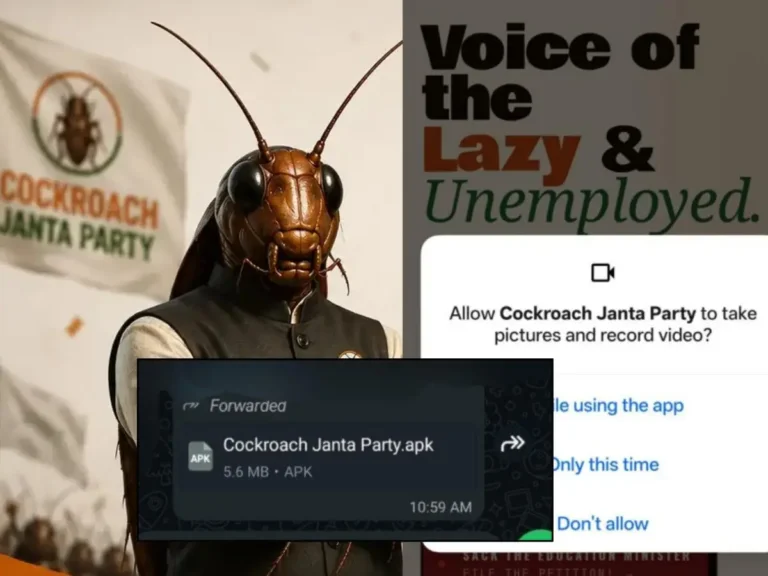
A cybersecurity report released on May 22, 2026, identifies a counterfeit Android application posing as the official app of the Cockroach Janta Party as a significant malware threat. The malicious app, known as Cockroach.Janta.Party, functions as a Remote Access Trojan (RAT) and can infiltrate Android devices, steal sensitive information, intercept communications, and control infected smartphones. The genuine Cockroach Janta Party has no affiliation with this app and is a victim of brand impersonation. The app is distributed through WhatsApp, Telegram, and misleading websites, particularly a rogue domain, cockroachjantaparty[.]org. It targets Android devices running versions 8.0 to 14 and requests elevated permissions, including access to camera, SMS, call logs, and contacts, while misusing the Android Accessibility Service to read on-screen content and grant itself additional permissions. The app contains multiple malicious modules for data exfiltration and uses a Command and Control infrastructure based on the Telegram Bot API. Users are advised to uninstall the app, disable Accessibility permissions, reset banking credentials, enable two-factor authentication, and conduct a full mobile security scan. The legitimate Cockroach Janta Party is encouraged to issue a formal clarification regarding the impersonation.
Search