activity

Tech Optimizer
September 28, 2026
Two newly identified Critical CVEs have expanded Microsoft's September identity infrastructure vulnerabilities to over ten verified weaknesses across more than ten distinct services. The Azure Database for PostgreSQL is vulnerable to CVE-2026-85878, an Improper Authorization flaw (CWE-285) with a CVSS score of 9.9. Azure Billing is impacted by CVE-2026-62874, which presents an Insufficient Data Authenticity Verification issue (CWE-345) with a CVSS score of 10.0. Both vulnerabilities were disclosed on September 18 and validated by Tenable and MITRE. CVE-2026-85878 allows an authorized attacker to elevate privileges over the network with minimal complexity, while CVE-2026-62874 requires no authentication, enabling unauthenticated attackers to jeopardize financial integrity. The vulnerability cluster first emerged during the Patch Tuesday cycles on September 3 and September 8, with initial reports highlighting critical flaws in core services. Other September disclosures include CVE-2026-83711 (Azure AD B2C, CVSS 10.0), CVE-2026-70352 (Azure AI Language, CVSS 10.0), CVE-2026-83941 (Entra ID, CVSS 9.9), CVE-2026-62916 (Entra ID, CVSS 9.1), CVE-2026-69857 (Azure Cosmos DB, CVSS 8.5), and CVE-2026-69854 (Spring Cloud Azure, CVSS 9.0). Activity heightened between September 17 and 18 with the introduction of CVE-2026-77903 (Microsoft Dataverse, CVSS 9.0) and CVE-2026-69843 (Microsoft Fabric, CVSS 10.0). The attack surface has broadened from authentication concerns to encompass trust in AI endpoints, data storage locations, and billing verification processes. Seven out of the ten vulnerabilities are unauthenticated, and all issues were addressed through server-side fixes by Microsoft. The extensive range of affected services suggests these vulnerabilities indicate a shared architectural dependency on authentication logic.
Tech Optimizer
September 26, 2026
Endpoint security is a suite of technologies and processes designed to protect devices connected to a business network from cyber threats. It includes various devices such as laptops, smartphones, tablets, servers, and IoT devices. Endpoint security employs a multi-layered approach, scanning for malware, regulating applications, and monitoring device activity for unusual behavior. It is distinct from antivirus software, encompassing a broader range of protective measures, including firewalls, encryption, application controls, patch management, and Endpoint Detection and Response (EDR). The rise of remote work and the increasing number of devices create a larger attack surface, making endpoint security essential for preventing breaches and safeguarding business operations.
AppWizard
September 25, 2026
Google is rolling out Android 17 QPR2 Beta 6 to Pixel testers to fix various issues, including crashes and unexpected reboots. The update addresses a reboot issue with the Pixel 9 Pro Fold related to third-party apps when opening the camera viewfinder. It follows the release of QPR2 Beta 5 and achieves Platform Stability, with all devices aligned on build numbers. Notable fixes include resolving a system kernel crash during simultaneous access to the camera and microphone, a visual regression affecting content display, a blank screensaver issue while charging, problems with dismissing locked applications, and device crashes during scrolling. Google has also temporarily removed blurred notifications on the lock screen to address certain bugs.
AppWizard
September 25, 2026
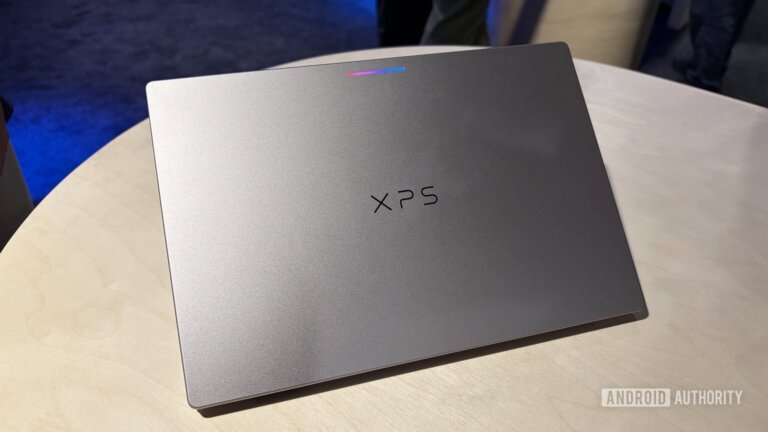
Google has introduced a hidden feature called the Glowbar Disco app in its new line of Googlebook laptops. This app transforms the laptop's lid light strip into a music-synced light show. The Glowbar is a design element across various manufacturers, indicating battery status and Gemini activity. Alexander Kuscher, Google’s Senior Director of Product for Laptops and Tablets, mentioned this feature during an interview, inviting users to explore it. Users had previously experienced the disco mode during demonstrations, but the method to access it was not disclosed until Kuscher's comments. The Glowbar is also functional, displaying essential information and responding to device activity, with plans for developers to create applications utilizing its capabilities.
Winsage
September 24, 2026
Security researchers from Graz University of Technology in Austria have discovered significant vulnerabilities in the file notification systems of major operating systems: Android, Linux, macOS, and Windows. These flaws have existed for decades and can lead to the leakage of sensitive system information. The affected systems include inotify on Linux (since 2005), FileObserver on Android (since 2008), ReadDirectoryChangesW on Windows (since 2000), and FSEvents on macOS (since 2007). The vulnerabilities allow unprivileged users to monitor file events without explicit read permissions, enabling potential attacks such as inter-keystroke timing attacks and website fingerprinting. For example, on Linux, monitoring a readable directory can leak events on files that cannot be read, allowing attackers to achieve a 93.1% to 100% accuracy rate in monitoring keystrokes. Specific vulnerabilities include CVE-2025-68788 on Linux, which received a partial fix in December 2025, and issues on Android where FileObserver can bypass app storage isolation. On macOS, limited information is available due to a lack of bypasses for private directories, while on Windows, monitoring the root directory can reveal the full path of every accessed file, allowing real-time tracking of web activity with a 97.8% accuracy rate. Microsoft has described the issue as "by-design," which has faced criticism. The researchers propose stronger mitigations, such as disallowing monitoring of entire drives on Windows and introducing a permission system for file monitoring on Windows and macOS. Their findings will be presented at the ACM CCS 2026 conference in November in The Hague, Netherlands.
AppWizard
September 24, 2026
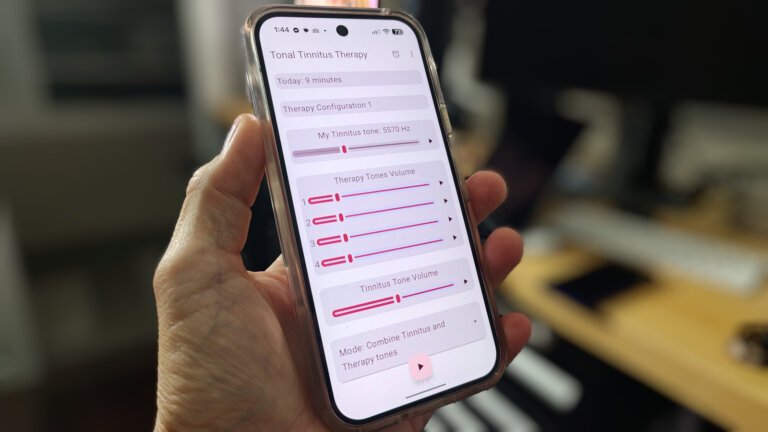
Two Android applications have been identified as helpful for tinnitus relief: one focuses on tonal therapy and the other on ambient sound generation. Both apps are free, with optional premium features. Tonal therapy involves using tailored sound frequencies to disrupt abnormal neural activity associated with tinnitus. Users must identify the pitch of their tinnitus, generate therapy tones, and play them in a staggered sequence. The Tonal Tinnitus Therapy app requires consistent use, with many users reporting significant symptom reduction over time. It offers a free version and a one-time purchase option for unlimited access. Recommended usage includes listening for at least four hours daily, starting with short sessions. The ambient noise generator app, such as Ambience: Sleep Sounds, creates soothing backgrounds to mask tinnitus sounds. It offers a variety of calming sounds and has both free and premium versions. Users can create personalized sound mixes to aid sleep, and reliance on the ambient generator may decrease as tonal therapy takes effect.
Search