Game director Chris Roberts announced that Squadron 42, the single-player component of Star Citizen, will be released in Q2 2027 to avoid clashing with Grand Theft Auto 6. A dedicated Steam page for Squadron 42 has been created, listing the game’s system requirements and indicating an install size of 150GB. The game does not reference modern features like ray tracing or DirectX 12. High-profile actors Gillian Anderson and Henry Cavill will appear in cutscenes.
Many VPN providers are now offering additional security features such as malware detection, malicious link checkers, and ad blockers, alongside their primary function of encrypting internet traffic. Notable VPNs like NordVPN and Surfshark have integrated real-time malware protection, with NordVPN becoming the first VPN to receive certification as a reliable anti-phishing tool in 2024. Surfshark's Surfshark One package offers comprehensive real-time protection from viruses and malware. Other VPNs, such as Avira and CyberGhost, utilize shared infrastructures for antivirus capabilities, which can lead to delays in updates and inconsistent platform support.
Microsoft Defender has improved significantly, blocking 95.5% of live threats according to AV-Comparatives, while Apple employs multiple defenses in macOS, including Gatekeeper and XProtect, to manage malware threats. Avast Free Antivirus has achieved a perfect 100% block rate in recent testing but comes with limitations compared to paid antivirus suites like Norton 360 Deluxe and Bitdefender Total Security, which offer additional features such as password managers and identity monitoring.
A layered approach to digital security, combining a VPN, free antivirus, and built-in OS-level security, is recommended for effective protection. Relying solely on one layer leaves potential gaps, as a VPN cannot detect existing malware, and free antivirus solutions may lack advanced features. Users managing sensitive data or frequent financial transactions should consider investing in premium antivirus suites for enhanced security.
Smartphones may not receive crucial security updates, leaving them vulnerable to threats despite appearing to function well. Users can check their device's security status by navigating to Settings > About Phone to see the last security patch date. If it exceeds three to six months, the device may be nearing its support cutoff. Google Play system updates can also enhance security and should be checked via the Play Store. Manufacturers typically do not publicize end-of-life dates, but resources like endoflife.date can help users find this information. For example, the Samsung Galaxy S26 FE will receive updates until September 2033, while the Google Pixel 6 Pro will stop receiving support in October 2026. Google offers seven years of updates for Pixel 8 and newer models, while Samsung provides up to seven years for Galaxy S24 and Z Fold/Flip6 models. OnePlus offers four years of OS updates and up to six years of security patches. The European Union mandates a minimum of five years of software updates for new smartphones sold within the region starting June 2025. If a phone stops receiving updates, users should enable automatic app updates, avoid unverified apps, use two-factor authentication, back up data, and be cautious with public Wi-Fi. If the last security patch is over six months old or the device has surpassed its support cutoff, upgrading to a newer model is advisable.
Google has implemented new developer verification requirements for Android app installations, effective September 30, focusing initially on Brazil, Indonesia, Singapore, and Thailand for certified devices running Android 7 or later. Apps must be linked to verified developers, and users can install apps from these developers without extra steps. However, downloading apps from unverified sources will require a new protocol called the Advanced Flow, which includes enabling settings in Developer options and a mandatory 24-hour waiting period before installation. These measures aim to enhance security against malicious software while still allowing sideloading. Google plans to expand these verification measures globally by 2027, while maintaining an open ecosystem for app distribution.
Google has introduced a new Android developer verification policy requiring developers to undergo verification in key markets such as Brazil, Indonesia, Singapore, and Thailand. This policy will oversee app installations from various platforms, including the Google Play Store and others. The verification requirement is set to expand to additional markets starting in 2027. While unverified applications can still be sideloaded, users will face a 24-hour waiting period before installation.
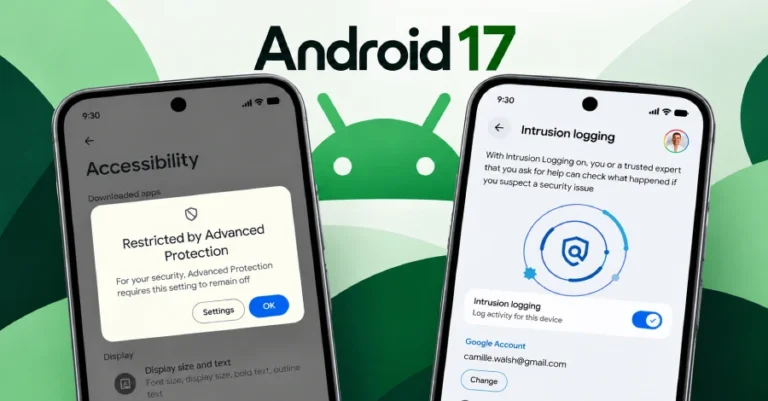
Google has enhanced its Android security framework by restricting access to the AccessibilityService API, allowing only verified applications classified as Accessibility Tools to use these features when Advanced Protection is activated. This decision addresses the misuse of the AccessibilityService API by malicious applications that facilitate malware distribution and financial fraud. The new measures include Intrusion Logging, USB Protection, disabling WebGPU, and a Failed Authentication Lock. Developers will be notified when Advanced Protection is enabled, and users can manually enable Intrusion Logging through the Advanced Protection settings page.
Researchers at Graz University of Technology discovered significant vulnerabilities in the file-notification subsystems of major operating systems: Linux, Windows, macOS, and Android. These flaws, present for decades, allow side-channel attacks that can infer sensitive information like keystrokes and visited websites. The vulnerabilities are rooted in components such as inotify (Linux, since 2005), FileObserver (Android, since 2008), ReadDirectoryChangesW (Windows, since 2000), and FSEvents (macOS, since 2007). Unprivileged users can exploit these subsystems to observe file events, potentially leading to keystroke timing attacks and credential theft. While Linux has implemented partial mitigations (CVE-2025-68788), Microsoft and Apple have acknowledged the issues but have not provided substantial patches.
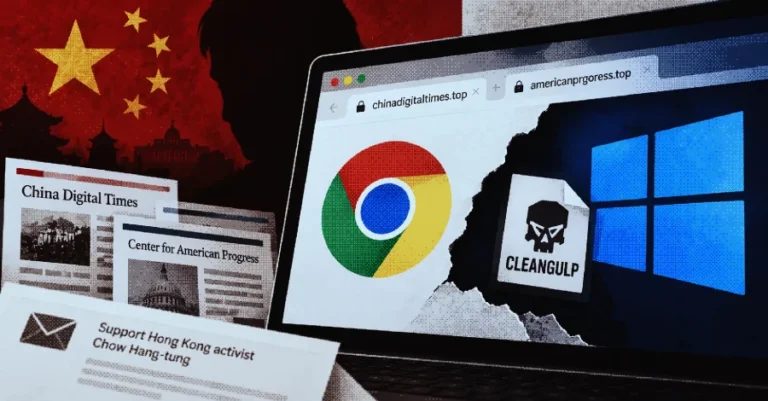
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
A newly identified strain of Android malware, RatHat, utilizes generative AI to manipulate infected devices in real time. It is linked to threat actors believed to be operating out of China. RatHat serializes the device’s live Accessibility tree into XML format and communicates with a generative AI assistant to return screen coordinates, identify text, and issue navigation commands. The malware employs WebView-based HTML overlays to capture login credentials from banking and cryptocurrency applications and can infiltrate payment apps like WeChat and Alipay to extract PINs. It also features an SMS receiver and notification listener to intercept OTPs and 2FA codes.
RatHat is disseminated through smishing, malvertising campaigns, and misleading third-party forums. It employs anti-analysis techniques such as container tampering, manifest bombing, DEX bytecode poisoning, string encryption, and anti-debugging. Once installed, it gains Accessibility access, activates Developer Options, and enables Wireless Debugging, allowing it to connect to the device's local ADB service and launch control agents with shell-level privileges.
The malware captures raw touch coordinates to reconstruct PINs and unlock patterns, bypassing screenshot protections. It also includes persistence mechanisms that prevent uninstallation by presenting a fake Google Play failure overlay and automatically reinstalling itself if removed.
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.