ADB

AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
AppWizard
September 15, 2026
A Google-made wearable device has been listed at the FCC, suggesting it may run on Wear OS and is primarily designed as a fitness tracker due to its lack of Wi-Fi connectivity and use of Bluetooth LE. It features GPS support and a durable metal frame. ADB testing indicates it may include Wear OS software. This device could fill the gap between the Fitbit Air and the Pixel Watch, as there have been no updates to the Fitbit Charge series since 2023. It is also connected to an unannounced fitness tracker shown during the Pixel 11 launch event, indicating Google's intent to expand its fitness tracking offerings.
AppWizard
September 10, 2026
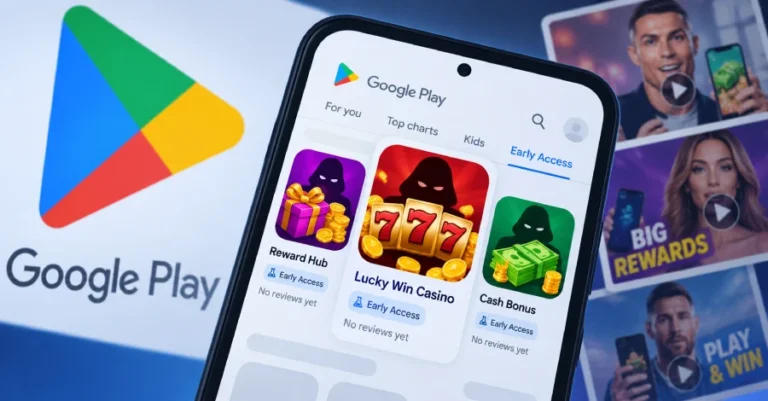
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
AppWizard
September 2, 2026
A developer, Mert Cobanov, optimized his smart TV using Claude Code, resulting in improved performance that surpasses its original state. He connected to his Android TV via ADB, deactivated unnecessary applications, and installed FLauncher without root access. Cobanov has created a website, "Clean up your Android TV," which provides a four-step process for others to achieve similar results. The process allows for reversibility, ensuring nothing is permanently uninstalled, and includes instructions for restoring specific apps if needed.
AppWizard
September 1, 2026
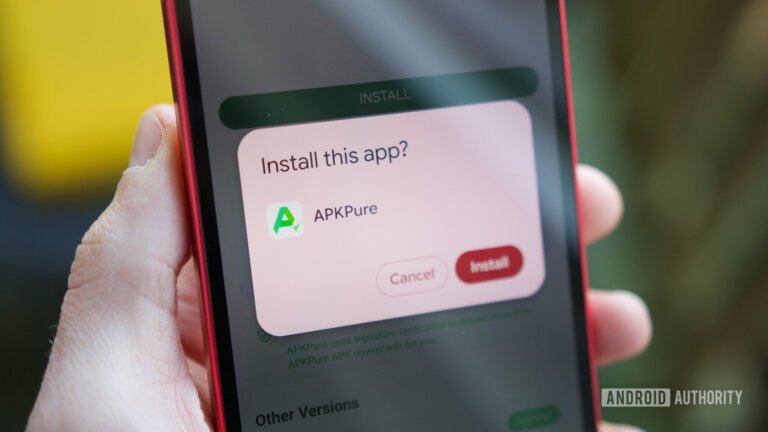
Google has started rolling out a new process for sideloading apps on Android devices, which requires users to restart their devices and wait 24 hours before sideloading applications. Users must confirm if they were prompted by someone to enable sideloading, with warnings about potential scams. After the waiting period, users can allow sideloading for seven days or indefinitely. The new process does not affect sideloading via ADB. Many users have expressed concerns about the future of sideloading, fearing increased restrictions.
AppWizard
August 26, 2026
Multilogin has launched an open-source AI agent for social media management on authentic Android devices in the cloud. This tool enables automation of workflows on platforms like TikTok, Instagram, Facebook, and X. The AI agent connects to a Multilogin Android cloud phone, allowing it to view screens, execute taps, type commands, and save results. It integrates with multiple AI agents capable of running shell commands and interpreting visual inputs. Each cloud phone functions as an independent Android device with unique parameters and persistent app data, connected via ADB. The tool monitors the cloud phone's readiness, activates ADB, interprets screenshots, and executes tasks while logging activities. It is designed for marketers, agencies, creators, and teams, providing setup instructions and compatibility with AI tools like ChatGPT/Codex and Claude Code. The project is available on GitHub, and Multilogin offers a free plan with paid options starting at [openai_gpt model="gpt-4o-mini" prompt="Summarize the content and extract only the fact described in the text bellow. The summary shall NOT include a title, introduction and conclusion. Text: Multilogin has unveiled an innovative open-source AI agent designed to empower social media management on authentic Android devices hosted in the cloud. This groundbreaking tool bridges the gap between AI capabilities and mobile app functionalities, allowing users to automate workflows across popular platforms such as TikTok, Instagram, Facebook, and X. How the Tool Functions The newly developed AI agent connects seamlessly to a Multilogin Android cloud phone, providing it with the ability to view screens, execute taps, type commands, and complete various tasks while saving the results. This integration works harmoniously with multiple AI agents, including Claude Code, Cursor, and OpenClaw, all of which can run shell commands and interpret visual inputs from screenshots. As many social media operations increasingly shift to mobile applications, the limitations of browser-based tools become apparent. While browser profiles serve their purpose for web-based tasks, they fall short when it comes to executing native Android applications. Multilogin's cloud phones offer a distinct advantage by providing an authentic Android environment, facilitating direct interaction with mobile apps. Each cloud phone operates as an independent Android device in the cloud, complete with unique device parameters, installed applications, and persistent app data. The AI agent connects to the cloud phone via ADB (Android Debug Bridge), a standard interface used by developers for device management. Operational Efficiency and Flexibility The process begins with the selection of an Android cloud phone, which the tool monitors until it is fully operational. Once ready, the AI agent activates ADB, allowing it to interpret screenshots, determine subsequent actions, and execute tasks such as tapping or typing. Upon completion of a task or in the event of an error, the tool halts the cloud phone and logs the activity, ensuring that resources are not wasted during the development and testing of AI-assisted mobile workflows. This project is compatible with any AI agent capable of executing shell commands and processing visual inputs, making it versatile for various applications. Gleb K., the UI team lead at Multilogin, emphasizes the importance of this development: “AI agents are becoming useful for real operational work, but many important workflows still happen inside mobile apps. We built this open-source project to give everyone a simple and controlled way to connect AI agents to Android cloud phones.” Target Audience and Accessibility The cloud phone agent is tailored for marketers, agencies, creators, and teams seeking an AI assistant to streamline routine tasks within Android applications. Users need not start from scratch; the project provides clear setup instructions and is compatible with widely-used AI tools such as ChatGPT/Codex, Claude Code, OpenClaw, and Cursor. Once connected, the AI agent can efficiently manage tasks on the cloud phone, with the Multilogin Support team readily available for assistance. As with any automation tool, users are encouraged to adhere to the guidelines set by the applications they utilize. The Multilogin cloud phone agent is accessible on GitHub: GitHub Repository. For further information about Android cloud phones from Multilogin, visit Multilogin's Website. The Need for Android Cloud Phones in Social Media Workflows As marketing teams increasingly adopt AI-driven workflows, the necessity for reliable and scalable environments becomes paramount. Real Android devices provide AI agents with the authentic conditions that mimic human usage, allowing accounts to behave naturally and accumulate history over time—an aspect that emulators and browser profiles simply cannot replicate. About Multilogin Multilogin is a comprehensive platform offering cloud phones and browser profiles tailored for marketers, agencies, creators, and AI workflow builders. It enables teams to manage distinct browser and mobile workflows from a unified dashboard. Multilogin offers a Free plan with no credit card requirement, while paid plans commence at .08 per month when billed annually, inclusive of monthly proxy traffic and mobile minutes based on the selected plan. Established in 2015, Multilogin operates from the UAE and adheres to GDPR compliance. Media Contact: Teona B. Media Specialist Multilogin Email: marketing@multilogin.com For additional visuals accompanying this announcement, please visit the following links: Visual 1 Visual 2" max_tokens="3500" temperature="0.3" top_p="1.0" best_of="1" presence_penalty="0.1" frequency_penalty="frequency_penalty"].08 per month.

AppWizard
August 26, 2026
Samsung has alerted developers using the Galaxy Store about upcoming changes due to Google's new Android Developer Verification (ADV) rules, which will take effect on September 30, 2026. Developers in Brazil, Indonesia, Singapore, and Thailand must complete the verification process to avoid having their unverified apps removed from the Galaxy Store. The ADV process requires developers to authenticate their identities and register package names and signing certificates. Apps that are not verified will be hidden from search results and listings, affecting their visibility. Users may face difficulties reinstalling or updating existing apps until developers complete the verification, although previously installed apps will continue to function. Samsung is indicating the status of app binaries in the Seller Portal and will restrict new registrations and updates lacking ADV approval starting in September. Sideloading will still be possible for certain apps and through an advanced installation flow, while ADB installations will remain unchanged. The initial rollout is limited to specific countries, with a global expansion expected in 2027. Developers are encouraged to act quickly to maintain app visibility.
Search