advertisements

Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
BetaBeacon
September 22, 2026
- Game Developer Releases WWII-Themed Match-3 Combat Game - Loyal Mussy has launched Milk Run: Tiles Over Europe, a WWII-themed match-3 combat game for Android - Players control a B-17 bomber on missions over wartime Europe, blending puzzle-solving and aerial warfare - Features a 25-mission campaign with various enemy aircraft types, anti-aircraft flak corridors, and historically accurate bombing targets - Players can upgrade their bomber, recruit crew members, and customize nose art and aircraft renaming - Immersive experience with visible battle damage, detailed sound design, and no ads or in-app purchases - Available for download on Android devices via Google Play
AppWizard
September 21, 2026
Take-Two Interactive has not confirmed the release date for Grand Theft Auto 6 on PC, but the game is anticipated to launch in November. Rockstar Games has updated its modding guidelines for GTA 6, which include prohibitions on altering storylines, combining elements from different titles, and unauthorized monetization of mods. The guidelines emphasize respect for Rockstar's intellectual property and the creator community, and they state that monetization is only allowed through approved digital storefronts. The game is set to launch on November 19 for PS5 and Xbox Series X|S, with the PC version's release date still unannounced. Additionally, Rockstar will release "Grand Theft Auto 6: The Album," featuring 34 original tracks from contemporary artists.
AppWizard
September 21, 2026
Microsoft is exploring the integration of advertisements into its XBOX gaming ecosystem without increasing prices. The company filed a patent on September 3 for a system that introduces ads during non-disruptive moments in games, such as loading screens or after missions. This system includes the concept of "advertising credits," allowing players periods free from ads. XBOX plans to incorporate ads into services like XBOX Cloud Gaming, which will offer a free tier for users who engage with ads. The company aims to prioritize player experience, avoid interrupting gameplay, maintain high-quality standards for ads, clearly distinguish ads from game content, and align ads with player expectations.
AppWizard
September 20, 2026
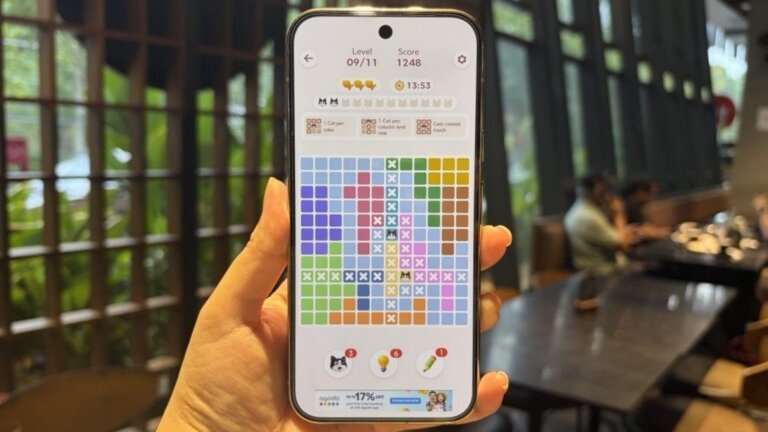
The author enjoys casual Android games that involve sorting and disassembling elements, particularly the game Meowdoku, which is a cat-themed puzzle game inspired by Sudoku. In Meowdoku, players must place ten different cats in a grid while following specific rules: each row and column can only contain one cat, and no two cats of the same color can be adjacent. Incorrect placements result in strikes, and three strikes require a level restart. The game includes hints and daily challenges, but the author finds the frequent ads after nearly every level frustrating, especially since there is no option for an ad-free experience. There is a demand among players for a premium, ad-free version, as discussed on various social media platforms. Despite the ads, the author continues to play Meowdoku and recommends it to others.
AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Search