agent

AppWizard
September 19, 2026
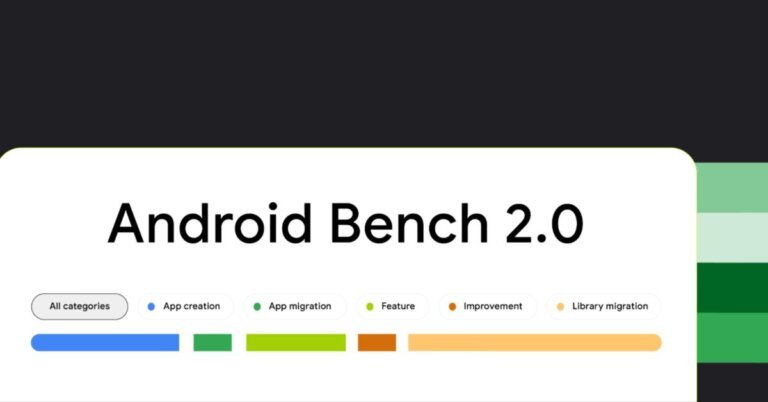
Google has launched Android Bench 2.0, an upgraded benchmark for evaluating AI coding agents, which now includes 30 long-horizon tasks that can take human engineers days or weeks to complete. The best pass rate for these tasks is around 28%, down from approximately 91% in the previous version. The benchmark measures both pass rates and completion rates, acknowledging partial progress rather than just failures. It assesses various challenges, including app creation and feature integration, using a comprehensive scoring methodology that evaluates functionality, regression checks, and visual fidelity. AI models perform better with new code than with modifications to existing systems, facing challenges in runtime validation and cross-platform conversions. The current leaderboard shows OpenAI’s GPT-6 Astra leading with a 28% pass rate, while Gemini 3.8 Flash has an 8% pass rate. Developers using AI agents should be aware that while AI can generate significant portions of applications, further refinements will require human input. The benchmark is available on Google’s Android Bench leaderboard.

AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 18, 2026
Google has released version 2.0 of Android Bench, which focuses on managing complex development tasks rather than minor adjustments. The new version evaluates tasks that may take engineers days or weeks to complete, such as adding features and building applications. A continuous scoring method has replaced the previous pass or fail system, assessing completion rates based on functionality, visual fidelity, and adherence to instructions. Various AI models have been tested, with GPT-6 Astra achieving a 28% pass rate, significantly lower than the previous scores around 90%. No model has achieved a 100% pass rate in porting cross-platform applications, with the best reaching 80%. AI performs better in writing new code than in refactoring existing code, facing challenges with architectural complexity and runtime validation. Android Bench utilized agents from model providers for evaluations and plans to incorporate various model combinations in future updates.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Tech Optimizer
September 16, 2026
Windows is the only desktop platform where antivirus software is essential. Microsoft has patched many vulnerabilities, but the OS still allows installations from unverified sources and connects to potentially untrustworthy networks. As of 2026, the top antivirus solutions for Windows include: - Norton 360: Best overall, with a full scan time of 13 minutes and 22 seconds, robust firewall, and up to 250 GB cloud backup. - Bitdefender: Best for older PCs, maintaining peak CPU usage at 11% and memory at 183 MB during scans. - Avast One: Best free option for Windows 11, achieving a perfect score in AV-TEST. - NordVPN Threat Protection Pro: Best for VPN users, blocking 90% of malware. - McAfee+: Best for households with multiple devices, offering unlimited coverage but is the slowest scanner. - Microsoft Defender: Best free option included with Windows, awarded Top Product by AV-TEST. Norton 360 has a 99.8% detection rate and offers a 60-day refund window. Bitdefender also has a 99.8% detection rate with low resource usage. Avast's free version is effective, while NordVPN provides integrated malware protection for existing VPN users. McAfee is suitable for large households but has slower performance. Microsoft Defender is adequate for single users practicing safe browsing but lacks multi-device support. Kaspersky is unavailable in the U.S. due to supply chain concerns.
Tech Optimizer
September 14, 2026
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
Search