AI assistant

AppWizard
September 22, 2026
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
AppWizard
September 14, 2026
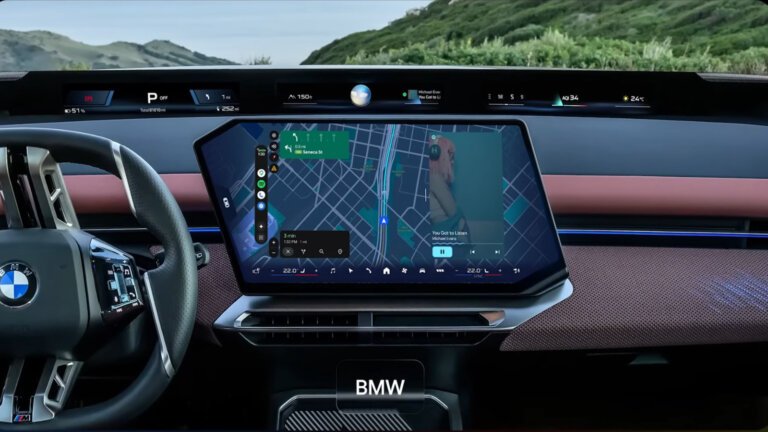
Google has introduced Gemini, an AI-powered assistant in a recent update to Android Auto, but user reception has been mixed, with many expressing dissatisfaction. Users report issues such as incorrect responses to queries, sluggish response times compared to the previous Google Assistant, and feelings of insecurity while driving due to Gemini's inconsistencies. Specific complaints include poor navigation, difficulty locating gas stations, inadequate Spotify integration, and the absence of features like weather updates. While many users have faced challenges, some have shared positive experiences with Gemini. Google is aware of the issues and is working on fixes. Users can revert to the previous Google Assistant if they prefer.
AppWizard
September 11, 2026
On September 1, 2026, Google introduced the “Remembered Items” feature in its Android ecosystem, allowing the AI assistant, Gemini, to track important belongings. This feature is part of the Android “Find Hub” app, version 3.1.732-02, released on September 11, 2026. Users can save items by instructing Gemini with phrases like, “Remember that I put the house key in the mailbox,” and can enhance entries with photos and notes. Items can also be saved manually, but they are not shareable with others. The app may misinterpret playful language, so users are advised to use clear phrases for successful saving.
AppWizard
September 9, 2026
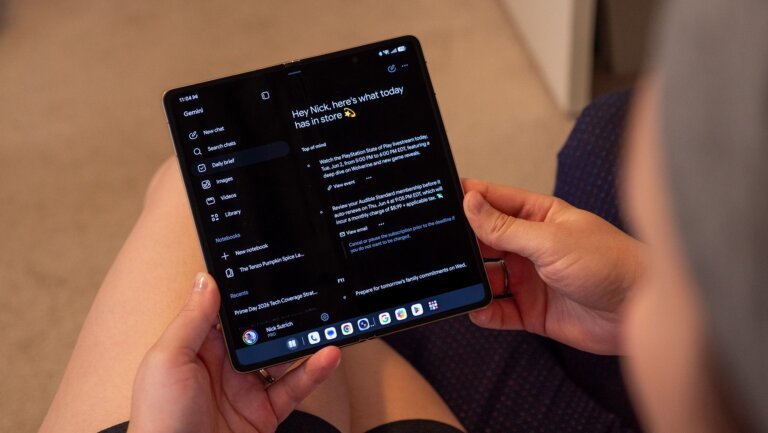
Google's Gemini's Daily Brief feature is now available to free users in the United States, removing the previous paid subscription requirement. The Daily Brief compiles information from Gmail, Google Calendar, and other connected applications, along with insights from past interactions, to create a personalized morning summary. Users need to have Personal Intelligence, Memory, and Google Workspace integration activated to fully utilize the feature. The rollout is gradual, and currently limited to U.S. users. Daily Brief allows users to manage tasks, initiate chats, and receive updates via Gemini Live. Future developments may include audio Daily Briefs and integration into the Android lock screen.
BetaBeacon
September 8, 2026
- Gemini is an AI assistant that has evolved into a multitasking tool. - Users can now complete more complex tasks through text prompts on Google Gemini. - The Gemini app now functions as a dynamic background module for multitasking. - The feature began rolling out on September 4 for Android devices. - The Gemini multitasking shortcut was previously available for specific Android devices. - The feature allows users to multitask while working in other apps. - The author hopes to see similar features for other AI tools on Apple and Android devices.
Search