algorithm

AppWizard
October 11, 2026
A research team from Turkey, led by Erdal Başaran and Ömer Okucu of Ağrı İbrahim Çeçen University, along with Yusuf Alaca from Hitit University, has developed an innovative detection framework for Android malware that utilizes a visual approach. This framework transforms key features of Android applications into images, allowing a Vision Transformer to differentiate between benign software and malware. The researchers created two types of images from static and dynamic analysis features: a conventional 2D grayscale image and a QR code image. Separate Vision Transformer models were trained on each image type, and spatial pooling features were extracted from deeper layers to create a comprehensive representation of application behavior. To refine the fused feature vector, Recursive Feature Elimination (RFE) was employed, enhancing classification clarity and reducing computational load. The final classification utilized a majority-voting ensemble strategy, achieving a detection accuracy of 98.72 percent, surpassing standalone models. The study demonstrates that the multimodal system outperforms individual grayscale or QR code pathways. The dataset used is publicly available, promoting reproducibility. The framework's reliance on static and dynamic analysis features allows it to adapt to new threats, and the novel QR code representation offers distinctive visual signatures of malicious behavior. However, challenges remain regarding feature extraction quality and computational demands.
AppWizard
October 10, 2026
Chrome Unboxed offers support for independent tech journalism and provides an ad-free experience with membership benefits. Android gamers face challenges with popular titles like Call of Duty: Mobile, which are unavailable for installation on Googlebook via the Play Store. Users can sideload apps on Googlebook OS, built on Android 17, without the limitations of the Play Store. The sideloading process involves downloading an APK from a trusted source, allowing unknown apps in Chrome, and installing the app. Google Play Protect monitors installed applications for malicious activity, but users should still exercise caution when sideloading.
Tech Optimizer
October 10, 2026
In gaming, tools such as utilities, beta applications, and modding tools are often distributed as APK, IPA, or desktop files, and it is essential to investigate their origin, version, and any security warnings before installation. Antivirus software flags potential threats based on known malicious signatures, behavior patterns, and reputation data. Tools that modify game clients may receive heightened scrutiny, and classifications like “HackTool” or “Riskware” do not definitively indicate a file's functionality. Identical game utilities can exist on various platforms, and a familiar website does not guarantee authenticity. It is crucial to verify the publisher, update date, version, and installation method of a file. The SHA-256 hash verifies file integrity but does not ensure safety from malware. Calculating a file hash can be done using specific commands in Windows, macOS, or Linux. Multi-engine scanning platforms like VirusTotal provide insights, but a lack of detections does not guarantee safety. Even if a file matches its reference hash and raises no alerts, it may still violate online game terms. A pre-installation checklist includes confirming the publisher, checking file types, comparing SHA-256 hashes, reviewing security findings, keeping antivirus protection enabled, and consulting platform rules. A cautious approach integrates source verification, file integrity checks, security assessments, and compliance with platform regulations.
AppWizard
October 9, 2026
Threads, a social media platform under Meta, is launching a new initiative in the U.S. called "Gems," which will award a distinctive purple badge to public posts and replies that contribute to meaningful discussions. This feature aims to foster engaging discourse among users. Additionally, Threads has introduced "ghost posts," which disappear after 24 hours, allowing users to share temporary thoughts and receive replies in direct messages. Another feature, "Dear Algo," lets users customize their content feed for up to three days and share their preferences with others.
AppWizard
September 30, 2026
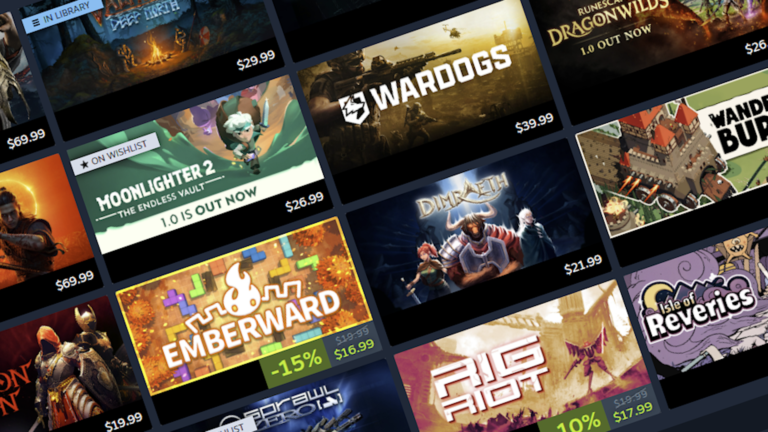
Steam is transitioning from a manual calendar-based promotional strategy to an algorithm-driven showcase of games, starting in early 2027. The Discounts & Events page will implement this new model to offer a wider array of discounted games tailored to user interests. Valve aims to enhance user experience and increase visibility for game developers through this change.
Winsage
September 19, 2026
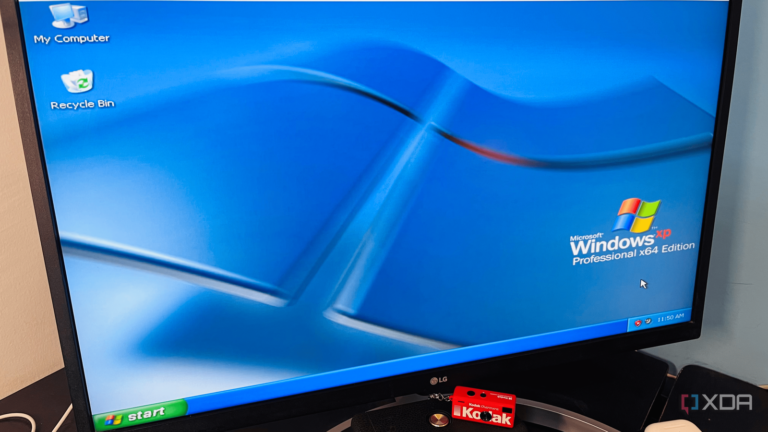
Windows XP was released in two versions: Retail for individual consumers and Volume for Microsoft's partners and OEMs. The product key FCKGW-RHQQ2-YXRKT-8TG6W-2B7Q8 became widely recognized due to a potential leak by an insider at a major OEM, which was then spread by the pirate group Devils0wn. The Volume version's activation system required a unique key, but the FCKGW key was incompatible with the standard installation CD. To verify the legitimacy of Volume discs, the activation system searched for a secret 10MB binary blob exclusive to the Volume media. Microsoft blacklisted the FCKGW key with Service Pack 1 and implemented further security measures with Service Pack 2, restricting access to certain updates. Contrary to prior beliefs, the key's functionality was not due to a simple key generation algorithm but was designed by skilled engineers.
Tech Optimizer
September 1, 2026
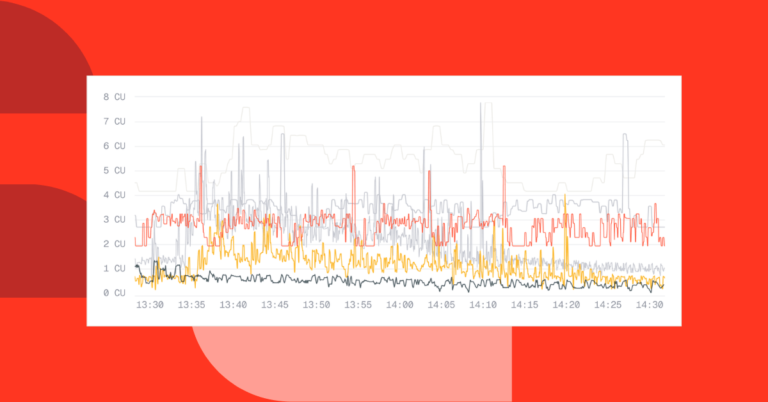
Choosing a database instance size without prior knowledge of the workload can lead to inefficiencies and excessive compute usage. Lakebase Postgres addresses this with an autoscaling feature that eliminates manual sizing, utilizing in-place VM resizing and a monitoring algorithm for CPU, memory, and working set size. Lakebase Postgres separates compute and storage layers, allowing independent resizing of compute nodes without affecting the database. The autoscaling algorithm relies on three signals: CPU load (cpuGoalCU), memory use (memGoalCU), and compute-cache working set size (lfcGoalCU). The CPU load is monitored every five seconds, aiming to maintain it at or below 90% capacity. Memory usage is tracked at two frequencies: overall memory every five seconds and Postgres-specific memory every 100 milliseconds, with a goal to keep usage below 75% of allocated RAM. The compute cache evaluates active data access efficiency, adjusting size based on workload. The working set is estimated using a modified HyperLogLog algorithm that records timestamps for page accesses, allowing for distinct page estimates over various time frames. The algorithm projects future working-set growth to allocate sufficient cache while capping it at 75% of RAM. Resizing the compute involves four components: the autoscaler-agent, vm-monitor, Kubernetes scheduler, and NeonVM. Scaling up occurs when any of the three goals indicate a need for more resources, while scaling down includes verification to ensure sufficient memory remains for operations. Timely adjustments in both directions are prioritized to minimize costs.
AppWizard
August 30, 2026
Security agencies in India have observed a shift in the tactics of terrorist groups, which are now using pornography websites and niche encrypted applications for communication instead of traditional social media. These groups, often collaborating with Pakistan's ISI, utilize platforms with real-time chat tools disguised as dating services to send instructions to recruits in Jammu and Kashmir. Security agencies are monitoring various digital tools, including Tor-based applications like Coatex and Conion, which obscure user identities. Some privacy-focused platforms do not require phone numbers for registration, complicating tracking efforts. Despite bans on certain pornography applications in India, they are still accessed illegally via VPNs, which mask users' IP addresses. The use of the Tor network presents additional tracking challenges, as it obscures data origins and destinations. Security agencies are adapting their surveillance methods in response to these developments, which include the use of virtual SIM cards in terrorist activities, as highlighted during investigations into the 2019 Pulwama attack.
Search