analysis

Winsage
September 24, 2026
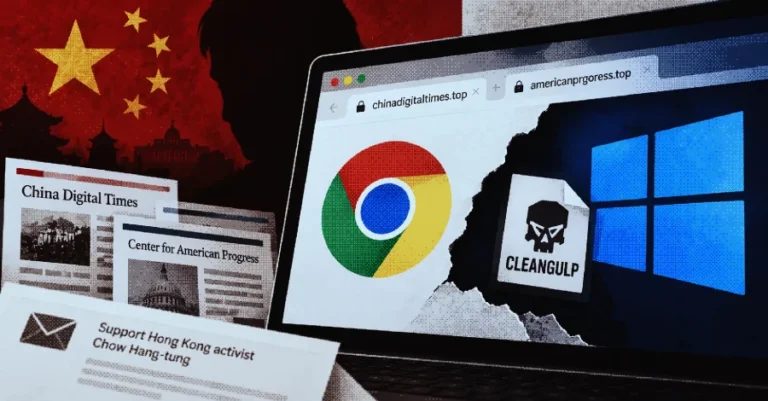
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
AppWizard
September 23, 2026
The Android development community has historically addressed memory optimization reactively, but new performance requirements from Google Play, effective February 2027, emphasize proactive memory management. These requirements include metrics for dynamic memory usage, bitmap memory, and DEX code optimization, with apps needing at least 25% optimization coverage. Memory usage can now hinder releases even without local crash replication, necessitating its integration into the pre-production process alongside other performance metrics. Dynamic memory usage is defined as anonymous RSS plus swap, excluding file-backed data. Google Play will evaluate this across different application states and device performance categories. Bitmap memory is scrutinized for the retention of invisible bitmaps, and DEX optimization aims to reduce memory footprint and improve performance. Investigating memory growth involves using Android Studio’s Memory Profiler to monitor memory changes during specific user flows and conducting heap dumps to identify retained objects. Issues often arise from retained state, where components hold onto callbacks that reference image data, necessitating a focus on lifecycle management rather than merely cache size. Bitmap memory should be carefully managed, as the decoded size can significantly exceed the compressed file size. Downsampling images to match UI dimensions is crucial. Memory checks should occur before production, with a focus on establishing a memory budget based on actual measurements and defining representative memory scenarios for testing. A pre-release memory checklist includes running user flows repeatedly, testing on various devices, inspecting heap dumps, examining image configurations, and reviewing optimization metrics. Monitoring Android vitals and Play Console warnings is essential to detect potential issues before they lead to user-reported crashes.
Search