APKs

AppWizard
October 10, 2026
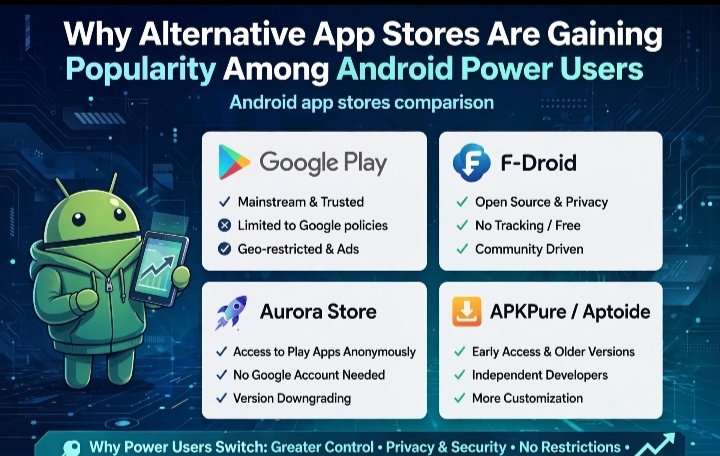
An alternative app store allows users to access apps and games not available on official platforms like the Google Play Store, including older versions, regional apps, and open-source options. Types of alternative app stores include third-party Android stores, open-source platforms, modified APK stores, regional stores, free app stores, and game-focused stores. Users explore these stores for a broader selection of apps, including those restricted by geography. Alternative app stores can provide apps that Google Play does not, such as regional apps and modified applications. When choosing an alternative app store, users should consider the platform’s reputation, app descriptions, update frequency, security measures, and source verification. Alternative app stores differ from Google Play by offering more flexibility and access to unique content, though security and developer support may vary. Modified apps are altered versions that may offer enhanced features. Alternative app stores are important for overcoming regional barriers and providing ad-free experiences. They host a variety of apps, including multiple versions of a single application, and typically feature user-friendly search functionalities. Comprehensive app information is often available, including version data and permissions. Some stores focus on open-source and independent apps. The legality of using alternative app stores depends on licensing and local laws, and they often feature apps not found on Google Play. Many alternative stores provide multiple app versions, and only reliable ones may offer faster updates.
AppWizard
October 10, 2026
Chrome Unboxed offers support for independent tech journalism and provides an ad-free experience with membership benefits. Android gamers face challenges with popular titles like Call of Duty: Mobile, which are unavailable for installation on Googlebook via the Play Store. Users can sideload apps on Googlebook OS, built on Android 17, without the limitations of the Play Store. The sideloading process involves downloading an APK from a trusted source, allowing unknown apps in Chrome, and installing the app. Google Play Protect monitors installed applications for malicious activity, but users should still exercise caution when sideloading.
AppWizard
October 7, 2026
In mid-August, Google implemented sideloading restrictions on Android devices, introducing warnings and a 24-hour wait timer for installing apps from third-party sources. A reader poll with over 1,800 participants revealed that over 63% prefer manually downloading APK files directly from platforms like GitHub. Only 20.7% use alternative app stores, while 16% do not engage in sideloading and only use the Google Play Store. F-Droid is not recognized as a verified third-party app store by Google, but it is noted for its ease of use.
AppWizard
October 1, 2026
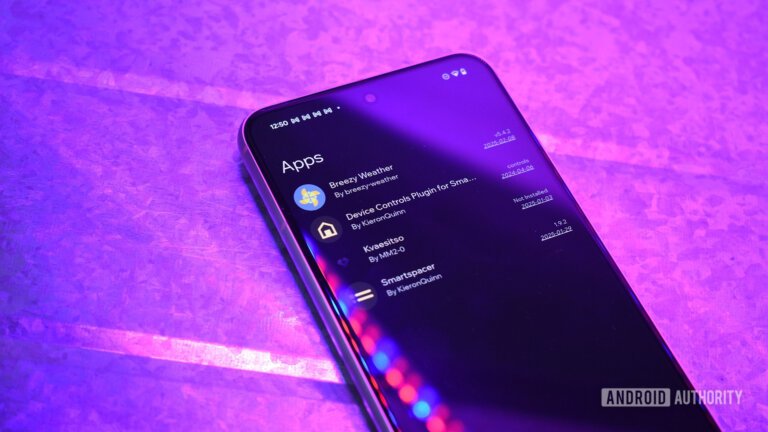
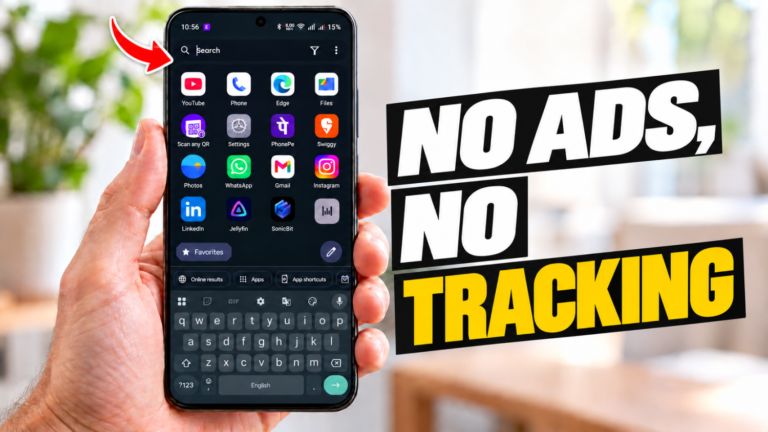
Android manufacturers curate devices, often leading to frustration for users who struggle to find specific settings due to the absence of desired features. The open-source community offers tools to enhance device functionality. MT Manager allows deep app modification directly on devices, providing access to app decompiling and editing without needing a desktop. It requires root permissions for its most powerful features and is not available on Google Play. Install with Options enables users to bypass installation restrictions on Android 7.0 and later, allowing the installation of apps outside the Google Play Store by using shell-level privileges or root access. Canta Debloater helps users safely remove carrier bloatware without root access on devices running Android 9.0 and above, using color-coded safety guidance to assist in the uninstallation process. ColorBlendr offers precise control over Material You color palettes on Android 12 and newer, allowing users to customize colors and themes with a live preview function. It requires elevated access via Root, Shizuku, or Wireless ADB. Kvaesitso Launcher replaces the default home screen with a search-centric interface, streamlining app navigation through a unified search bar that handles queries for apps, contacts, files, and calendar events. It is available on GitHub, F-Droid, and IzzyOnDroid.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Search