authentication

Tech Optimizer
September 14, 2026
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
Tech Optimizer
September 11, 2026
Microsoft BitLocker and Apple FileVault are free, integrated encryption solutions within their respective operating systems. As of 2026, the focus is on investing in management solutions that provide compliance proof, key escrow, recovery options, and policy enforcement across devices. Native encryption solutions lack certain management features, prompting the need for additional management layers from various vendors. Legacy freeware like TrueCrypt is no longer maintained, posing risks for business use, while VeraCrypt is a credible open-source alternative but lacks centralized management. Management options include Microsoft Intune for Windows, Sophos for mixed fleets, and specialized providers like Check Point and WinMagic for advanced needs. Organizations should ensure proper key management before enforcing encryption to avoid data loss and regularly test recovery processes. It is crucial to verify claims regarding compatibility and pre-boot options when selecting encryption solutions. Native engines are free, but management layers typically charge per endpoint annually.
AppWizard
September 10, 2026
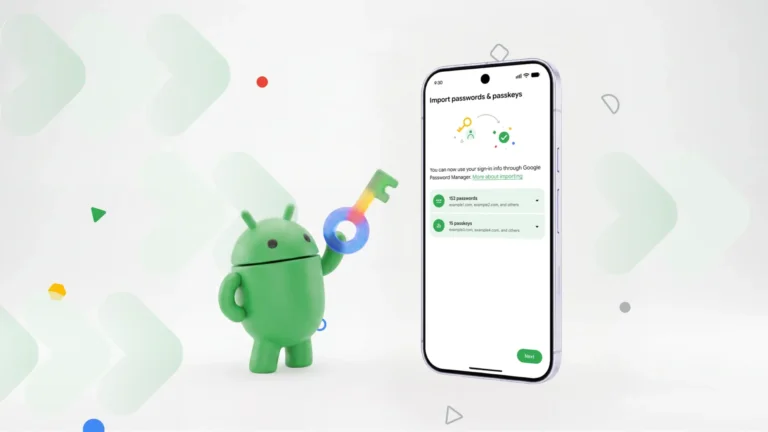
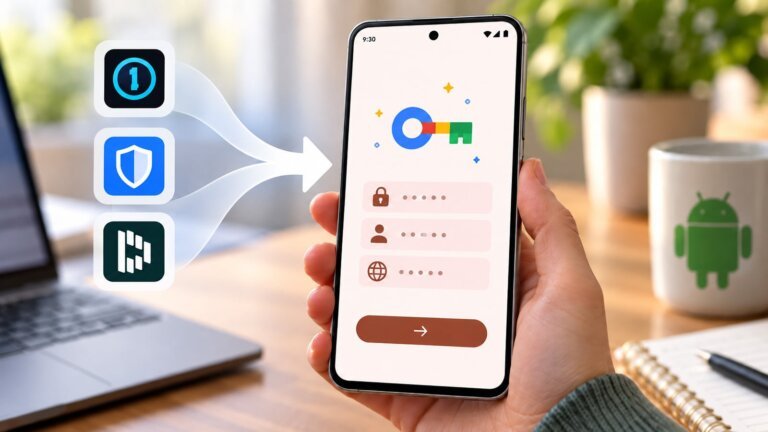
Google has introduced a credential transfer feature for password managers on Android devices, allowing users to seamlessly transfer saved passwords and passkeys between applications using the Credential Exchange Format. This feature enhances security by encrypting the transfer process, ensuring that credentials remain secure and inaccessible to Android during the exchange. Users can initiate the transfer by selecting the import option in their desired password manager app, which automatically detects other installed password managers. Currently, the feature is supported by Google Password Manager, 1Password, Bitwarden, and Dashlane, and is compatible with devices running Android 8 or later.
Winsage
September 9, 2026
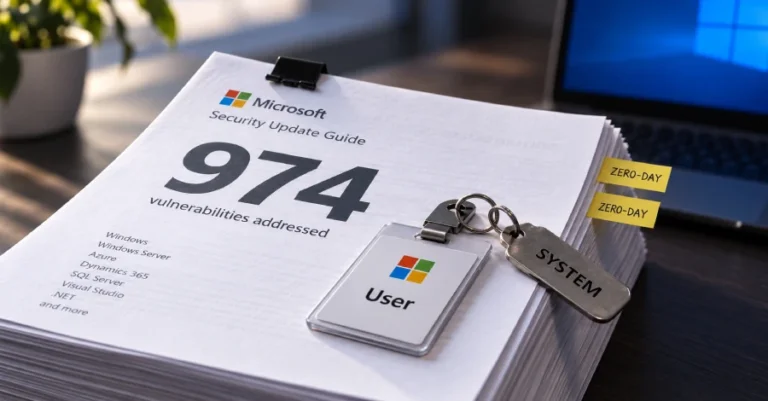
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Winsage
September 9, 2026
The September 2026 security cycle revealed a bifurcated approach to vulnerability management by Microsoft, focusing on cloud-side identity services with silent mitigations and traditional Patch Tuesday updates for on-premises Windows infrastructure. On September 3, Microsoft addressed nine cloud-side vulnerabilities, including two with a CVSS score of 10.0: CVE-2026-83711 (Azure AD B2C elevation of privilege) and CVE-2026-70352 (Azure AI Language Authoring missing authentication). Additionally, CVE-2026-83941 (Entra ID elevation of privilege, rated 9.9) and CVE-2026-80098 (Copilot Studio cryptographic flaw) were noted. On September 8, the Patch Tuesday update addressed 70 CVEs, including critical issues in the on-premises stack, such as CVE-2026-83939 (Windows Secure Kernel Mode elevation of privilege). CVE-2026-69414 (ShieldBreak), an elevation of privilege vulnerability in the Defender Malware Protection Engine, was patched out-of-band on September 3 after being publicly exposed for three weeks. Microsoft is shifting its Self-Service Password Reset (SSPR) enforcement to default to passkeys as of September 7, with plans to phase out SMS and voice-based authentication by February 2027. This aims to enhance security by moving away from legacy credentials.
Winsage
September 9, 2026
At the IFA 2026 event, Microsoft announced that Windows 11 will feature significantly faster boot times and improvements in the responsiveness of Windows Hello, the biometric authentication feature. The company is committed to optimizing Windows 11 for devices with 8GB of RAM, ensuring efficient performance on lower-end PCs.
Search