authorization

AppWizard
October 7, 2026
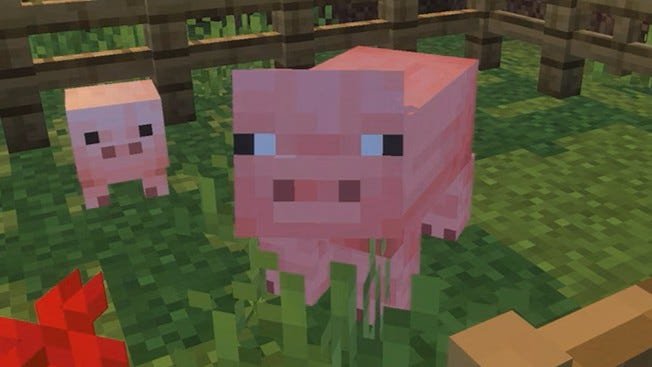
Minecraft is now playable within posts on X (formerly Twitter) through a project called "Tweetcraft," developed by user jaivin using AI technology. Tweetcraft allows users to create a shared Minecraft world and post a link for others to join in real-time multiplayer sessions. Jaivin has also introduced in-game sponsorship opportunities, enabling players to purchase ad placements with cryptocurrency. The project operates without official authorization from Mojang or Microsoft, and jaivin claims it uses none of Minecraft's assets. The launch post has garnered over 7.4 million views, raising potential legal concerns. The community's response includes both enthusiasm and apprehension regarding possible legal challenges. Additionally, October has seen the emergence of browser-based versions of other popular games, highlighting the rapid innovation in AI-generated gaming content.
Tech Optimizer
September 28, 2026
Two newly identified Critical CVEs have expanded Microsoft's September identity infrastructure vulnerabilities to over ten verified weaknesses across more than ten distinct services. The Azure Database for PostgreSQL is vulnerable to CVE-2026-85878, an Improper Authorization flaw (CWE-285) with a CVSS score of 9.9. Azure Billing is impacted by CVE-2026-62874, which presents an Insufficient Data Authenticity Verification issue (CWE-345) with a CVSS score of 10.0. Both vulnerabilities were disclosed on September 18 and validated by Tenable and MITRE. CVE-2026-85878 allows an authorized attacker to elevate privileges over the network with minimal complexity, while CVE-2026-62874 requires no authentication, enabling unauthenticated attackers to jeopardize financial integrity. The vulnerability cluster first emerged during the Patch Tuesday cycles on September 3 and September 8, with initial reports highlighting critical flaws in core services. Other September disclosures include CVE-2026-83711 (Azure AD B2C, CVSS 10.0), CVE-2026-70352 (Azure AI Language, CVSS 10.0), CVE-2026-83941 (Entra ID, CVSS 9.9), CVE-2026-62916 (Entra ID, CVSS 9.1), CVE-2026-69857 (Azure Cosmos DB, CVSS 8.5), and CVE-2026-69854 (Spring Cloud Azure, CVSS 9.0). Activity heightened between September 17 and 18 with the introduction of CVE-2026-77903 (Microsoft Dataverse, CVSS 9.0) and CVE-2026-69843 (Microsoft Fabric, CVSS 10.0). The attack surface has broadened from authentication concerns to encompass trust in AI endpoints, data storage locations, and billing verification processes. Seven out of the ten vulnerabilities are unauthenticated, and all issues were addressed through server-side fixes by Microsoft. The extensive range of affected services suggests these vulnerabilities indicate a shared architectural dependency on authentication logic.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If an organization holds Microsoft 365 E5, it already has access to Microsoft Defender for Endpoint. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly management. CrowdStrike is preferred for those with a mature Security Operations Center (SOC) and sufficient budget. The choice of endpoint protection depends on specific organizational needs. Business endpoint protection integrates various technologies to defend against malware and attacks on devices. Organizations should assess their current situation before selecting a solution. Key recommendations include: - Microsoft Defender for Endpoint for organizations already using Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a funded SOC. - SentinelOne for mid-sized organizations needing automation. - ESET for those with older hardware or virtual desktops. - Avast Business for very small businesses lacking IT staff. - VIPRE for budget-conscious organizations needing straightforward coverage. - Expel for organizations wanting managed detection across diverse environments. Organizations should avoid running multiple real-time agents simultaneously and ensure prevention features are activated. Testing should prioritize line-of-business applications, and rollout procedures should be defined before going live. It’s essential to verify update staging and rollback procedures with vendors and confirm existing licenses to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Search