autonomous

Tech Optimizer
October 10, 2026
DBtune, a startup based in Malmö/Lund, Sweden, was founded in 2020 by Dr. Luigi Nardi as a spin-off from Stanford University and Lund University. The company focuses on enhancing PostgreSQL's capabilities through autonomous database optimization technology and has raised .4 million in a seed round from various investors in July 2023, with support from the Wallenberg Foundation and Vinnova. DBtune's technology utilizes agentic AI for optimizing PostgreSQL databases by tuning server parameters, optimizing indexes, and monitoring autovacuum processes. The release of DBtune version 4.0 incorporates machine learning and AI to dynamically adjust server parameters and suggest optimal indexing strategies. The platform identifies and ranks potential index opportunities based on workload and provides recommendations for new indexes and maintenance of existing ones. A case study with Midwest Tape demonstrated a 10.8x performance improvement in database query runtime after employing DBtune for performance tuning. Benchmarking tests showed a transaction throughput increase of 87% during initial optimization, with a further 17% improvement on an already optimized system. Disk I/O activity was reduced by 43%, and WAL generation decreased by 23%. Dr. Nardi emphasizes the need for AI-driven optimization to manage the complexities of PostgreSQL databases and rising cloud costs, suggesting that significant code adaptations will be necessary for achieving fully autonomous PostgreSQL.
Winsage
September 26, 2026
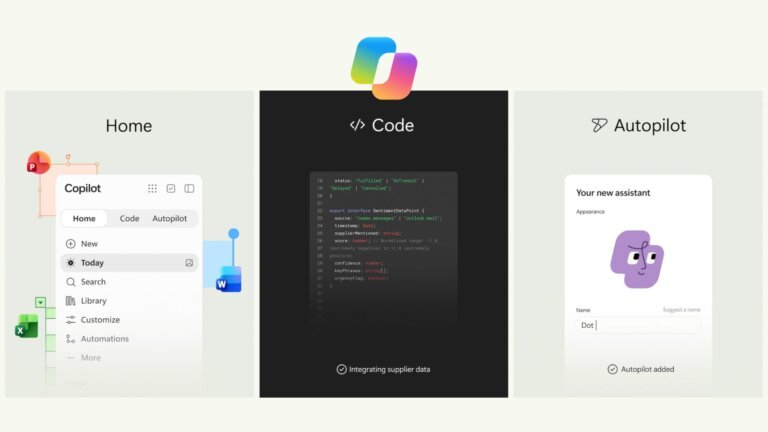
Microsoft CEO Satya Nadella announced a unified Copilot experience that integrates Home, Code, and Autopilot into a single application, transforming the Microsoft 365 suite into a “super app.” Copilot is described as a “new OS for work,” serving as a central hub for productivity across various tasks and devices. The Home section features Chat and Cowork functionalities, while the Office section includes full integration of Word, Excel, and PowerPoint. The Code feature allows users to create applications using natural language, democratizing app development. Autopilot, previously known as Scout, functions as a virtual colleague that manages tasks and projects. Microsoft has revised its pricing model to include a standard per-user subscription for basic functionalities and a usage-based billing model for advanced features. The announcement on September 25 met the timeline set during the Build 2026 conference, although features are still being rolled out incrementally. The new Copilot experience aims to enhance user interaction with AI without introducing a new operating system.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If an organization holds Microsoft 365 E5, it already has access to Microsoft Defender for Endpoint. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly management. CrowdStrike is preferred for those with a mature Security Operations Center (SOC) and sufficient budget. The choice of endpoint protection depends on specific organizational needs. Business endpoint protection integrates various technologies to defend against malware and attacks on devices. Organizations should assess their current situation before selecting a solution. Key recommendations include: - Microsoft Defender for Endpoint for organizations already using Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a funded SOC. - SentinelOne for mid-sized organizations needing automation. - ESET for those with older hardware or virtual desktops. - Avast Business for very small businesses lacking IT staff. - VIPRE for budget-conscious organizations needing straightforward coverage. - Expel for organizations wanting managed detection across diverse environments. Organizations should avoid running multiple real-time agents simultaneously and ensure prevention features are activated. Testing should prioritize line-of-business applications, and rollout procedures should be defined before going live. It’s essential to verify update staging and rollback procedures with vendors and confirm existing licenses to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Search