AVD

Winsage
September 26, 2026
Microsoft has acknowledged that some users may experience desktop loading issues, specifically black screens, after installing the August 2026 preview updates and subsequent releases. This problem mainly affects Azure Virtual Desktop (AVD) hosts using FSLogix. Symptoms include a black screen post-sign-in and crashes related to Windows Explorer, which can be temporarily resolved by manually launching Windows Explorer through Task Manager. For enterprise customers, Microsoft has introduced a mitigation strategy via Known Issue Rollback (KIR), allowing IT administrators to reverse problematic updates by applying specific group policies. Additionally, Microsoft has addressed issues related to the loss of mouse and desktop settings on certain Windows 11 systems caused by the KB5120998 update.
Winsage
September 25, 2026
Microsoft has acknowledged an issue affecting some Windows 11 users utilizing virtual desktops, where a black screen appears after sign-in, requiring manual launch of Explorer to regain access. This glitch is linked to devices operating on the August 2026 non-security preview update or later. It has been predominantly observed on Azure Virtual Desktop (AVD) hosts using FSLogix, with crashes of Windows Explorer noted in the Application event log. A temporary workaround involves using Task Manager to initiate explorer.exe as a new task. Microsoft has implemented a Known Issue Rollback (KIR) via Group Policy to disable the problematic change until a permanent fix is released. Versions 26H1, 25H2, and 24H2 of Windows 11 are affected, while Windows 10 and Windows Server do not appear to be impacted.
BetaBeacon
September 9, 2026
Android Studio Emulator is the official Android SDK tooling maintained by Google for app developers to test code against specific Android API levels, screen densities, and hardware profiles.
Winsage
May 30, 2026
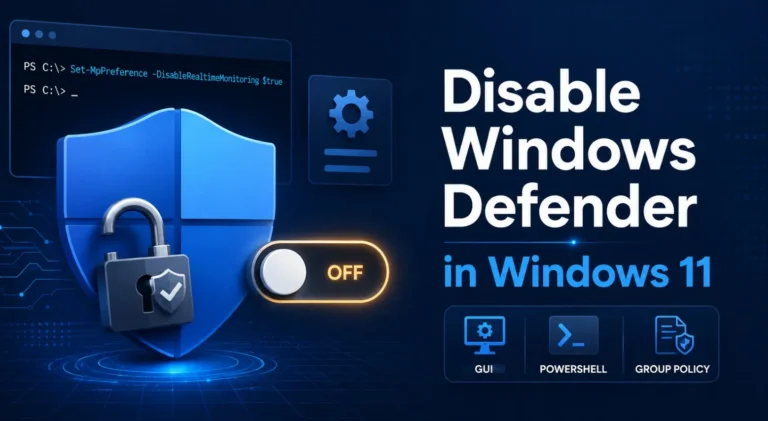
Disabling Windows Defender is common among users setting up virtual machines or optimizing build processes, but it can be frustrating due to Windows 11's resistance to such actions. Many guides suggest using outdated registry keys, which are often reverted by updates, leading to repeated attempts to disable the protections. Users may disable Defender for several reasons, including performance issues with virtual machines, conflicts with Android emulators, hindrances in development environments, troubleshooting disk performance, and security testing in isolated labs. However, disabling antivirus software increases exposure to threats. Microsoft Defender includes components such as Antivirus, Real-Time Protection, Cloud-Delivered Protection, Tamper Protection, and Defender for Endpoint. Tamper Protection is a significant barrier to disabling Defender, as it prevents unauthorized changes to security settings. Key considerations before disabling Defender include the need for administrator rights, the effect of Tamper Protection, potential resets from Windows Updates, temporary toggles for Real-Time Protection, and the option to install third-party antivirus software, which places Defender in passive mode. Methods to disable Defender include using the Windows Security GUI, PowerShell commands, Command Prompt, or Group Policy (available only for certain editions). Disabling Tamper Protection requires accessing the GUI or being managed by an organization. To check if Defender is disabled, users can use PowerShell to review specific fields. Common reasons for Defender reactivating include enabled Tamper Protection, system reboots, Windows Updates, lack of third-party antivirus, and security policy refreshes. Installing a legitimate third-party antivirus is often the best way to maintain a consistent state. Instead of disabling Defender, users can add exclusions for specific folders related to virtual machines or development tools, allowing them to maintain protection while avoiding conflicts. Troubleshooting common problems includes ensuring elevated sessions for PowerShell, checking Tamper Protection status, and understanding the limitations of the Group Policy editor based on the Windows edition. Disabling Defender may be appropriate in specific scenarios, but for regular use, especially on machines handling sensitive tasks, the risks generally outweigh the benefits. Using exclusions is recommended for performance improvements without compromising security.
Winsage
January 30, 2026
Microsoft has enhanced the management of Remote Desktop Protocol (RDP) Shortpath, now available through Group Policy Objects (GPO) and Microsoft Intune, allowing IT teams to implement centralized control over RDP Shortpath behavior across Azure Virtual Desktop (AVD) session hosts and Windows 365 Cloud PCs. RDP Shortpath improves performance and reliability by establishing a direct, UDP-based network connection, reducing latency and enhancing responsiveness for audio and video applications. Prior to this update, managing RDP Shortpath was fragmented, requiring manual adjustments on individual session hosts, which complicated consistent networking behavior. The new centralized configuration allows administrators to enforce Shortpath settings uniformly, reducing administrative overhead and ensuring consistent performance and security controls. Administrators can manage RDP Shortpath settings centrally, control all Shortpath modes, and ensure compatibility with AVD host pool settings. Effective operation of RDP Shortpath requires appropriate network conditions, and policy changes necessitate a restart of session hosts or Cloud PCs.
Winsage
January 18, 2026
Windows 11 KB5074109 has caused several issues for users, particularly those with Nvidia GPUs, including black screens, Outlook freezing with POP accounts, and problems with File Explorer's desktop.ini settings. Users have reported random black screens and desktop freezes after installing the update, with some finding temporary relief by changing their monitor's DisplayPort mode. Outlook Classic has been problematic, remaining active in the background and freezing shortly after opening, prompting users to terminate the process in Task Manager or uninstall the update. Additionally, the update disrupts Azure Virtual Desktop functionality, leading to sign-in failures and connection issues. Microsoft has acknowledged these problems and is investigating solutions, including a Known Issue Rollback for AVD. The update also breaks the LocalizedResourceName directive in File Explorer, preventing folder name customization. Users can uninstall the update through Settings, but this may expose them to security vulnerabilities.
Winsage
July 19, 2025
Microsoft's Windows 11 24H2 update has encountered multiple issues, including a persistent Windows Firewall error (Event 2042) that worsened after the July 2025 update. The company issued an apology for the confusion, clarifying that the error is a logging anomaly with no security risk. Users have also reported problems with the Microsoft Changjie Input Method, Azure Virtual Desktop app failures, camera application unresponsiveness, wallpaper customization issues, blue screen errors related to Easy Anti-Cheat, and audio loss with Dirac Audio. Microsoft is working on resolutions for these problems in future updates.
Winsage
May 6, 2025
Microsoft has released Windows 11 24H2, but users are facing a known issue with Azure Virtual Desktop (AVD) applications, specifically related to the "App attach" feature. This feature allows applications to be dynamically attached to user sessions within AVD, operating within containers rather than being installed locally. Users may encounter an error message stating, "Element not found" when launching App attach applications. Microsoft recommends using VHDX images instead of CimFS images for packaging files, as the issue has not been reported in earlier versions of the operating system. A fix for the current version is expected by June 2025. The update for Windows 11 24H2 will be automatically received by devices running Windows 11 22H2 and 23H2, with users able to select the restart time or postpone the update.
Search