Azure Virtual Desktop

Winsage
October 14, 2026
Microsoft released its October 2026 Patch Tuesday updates for Windows 11, addressing 1,413 vulnerabilities, including a critical fix for an exploited Windows Shell vulnerability (CVE-2026-96951) that bypasses Mark of the Web defenses. This update is the last monthly security update for Windows 11 24H2 Home and Pro users, who must upgrade to a supported version for future security fixes. The update packages KB5127648 and KB5127646 cover versions 24H2, 25H2, and 26H2, and also include fixes for reliability issues such as Explorer.exe startup failures, VPN connection problems, and gaming mouse stuttering. Additionally, the update resolves issues with AC-3 playback, printing failures, and fingerprint sign-in failures after a cold boot. Users are advised to install the updates promptly and restart their systems to complete the process.
Winsage
October 7, 2026
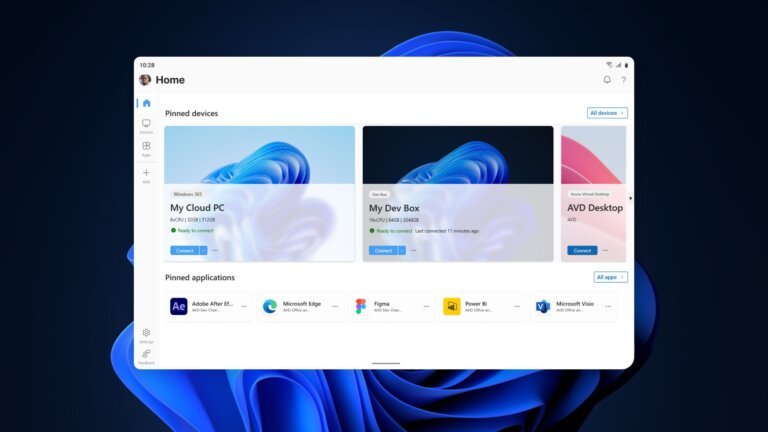
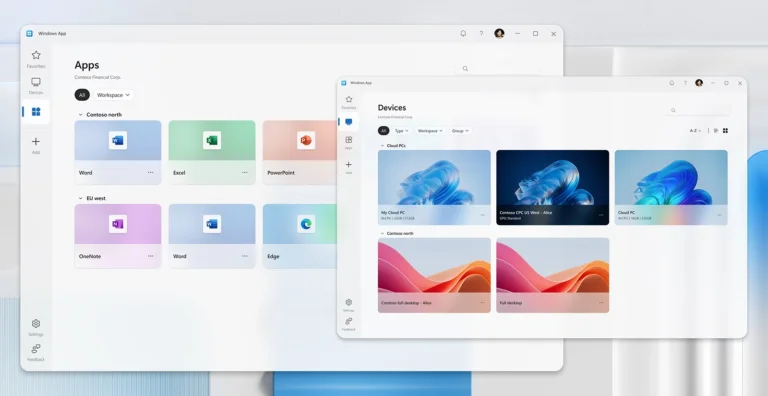
Microsoft has launched a significant enhancement to its Windows App, now allowing general availability for remote PC connections on Windows. Users can access both physical and virtual Windows PCs, integrating resources from Windows 365, Azure Virtual Desktop, and Microsoft Dev Box into a single interface. The Windows App replaces the previous Remote Desktop app from the Microsoft Store and the standalone Remote Desktop client, while the traditional Remote Desktop Connection tool (mstsc.exe) remains supported. Users can connect to remote PCs by entering the computer's name or IP address, with options for display preferences and local resource redirection. All redirections are turned off by default for security, and connections can be saved and pinned to a Favorites list. Marvin Quinzon, Senior Program Manager at Microsoft, highlighted the importance of this update for users and organizations needing flexibility in cloud and traditional remote access scenarios.
Winsage
October 7, 2026
The latest update to the Windows App allows users to connect to a Windows PC remotely, expanding its capabilities beyond previous support for Windows 365, Azure Virtual Desktop, and Microsoft Dev Box. To use this feature, users need to download the app, select "Add a Remote PC," input the remote PC's name or IP address, and then establish the connection. The classic Remote Desktop Connection tool (mstsc.exe) remains available despite the retirement of the Remote Desktop app from the Microsoft Store.
Winsage
September 26, 2026
Microsoft has acknowledged that some users may experience desktop loading issues, specifically black screens, after installing the August 2026 preview updates and subsequent releases. This problem mainly affects Azure Virtual Desktop (AVD) hosts using FSLogix. Symptoms include a black screen post-sign-in and crashes related to Windows Explorer, which can be temporarily resolved by manually launching Windows Explorer through Task Manager. For enterprise customers, Microsoft has introduced a mitigation strategy via Known Issue Rollback (KIR), allowing IT administrators to reverse problematic updates by applying specific group policies. Additionally, Microsoft has addressed issues related to the loss of mouse and desktop settings on certain Windows 11 systems caused by the KB5120998 update.
Winsage
September 25, 2026
Microsoft has acknowledged an issue affecting some Windows 11 users utilizing virtual desktops, where a black screen appears after sign-in, requiring manual launch of Explorer to regain access. This glitch is linked to devices operating on the August 2026 non-security preview update or later. It has been predominantly observed on Azure Virtual Desktop (AVD) hosts using FSLogix, with crashes of Windows Explorer noted in the Application event log. A temporary workaround involves using Task Manager to initiate explorer.exe as a new task. Microsoft has implemented a Known Issue Rollback (KIR) via Group Policy to disable the problematic change until a permanent fix is released. Versions 26H1, 25H2, and 24H2 of Windows 11 are affected, while Windows 10 and Windows Server do not appear to be impacted.
Winsage
June 15, 2026
Microsoft has expanded the rollout of the Secure Boot 2023 certificate update to more Windows 11 and Windows 10 devices with the June 2026 Patch Tuesday update (KB5094126). This update aims to ensure that most supported consumer PCs are classified as high confidence, meaning necessary certificates are either installed or will be applied automatically. Secure Boot is a firmware security feature that verifies the software attempting to load during the startup process, blocking unauthorized software. The certificates supporting Secure Boot, issued in 2011, are expiring in stages starting June 24, 2026, prompting Microsoft to deploy replacement certificates. Most home users do not need to take manual action as the updates will occur automatically via Windows Update. Users can check their Secure Boot certificate status in the Windows Security app. A yellow warning indicates pending compatibility data, while a red alert suggests a firmware incompatibility requiring a BIOS update. Multiple reboots during the update process are normal, and a new SecureBoot folder in Windows is for staging cryptographic files. Older PCs may experience longer update times, and some may not receive updates due to firmware issues. HP users should check for BIOS updates if encountering BitLocker recovery loops. IT administrators should monitor device classifications and manually initiate updates for devices not in the high confidence category. Devices with Secure Boot disabled cannot receive updates, leaving them vulnerable. The expiration of the Microsoft Corporation KEK CA 2011 certificate on June 24 does not immediately affect device functionality, but it limits Microsoft's ability to sign new bootkit blacklist updates.
Winsage
January 30, 2026
Microsoft has enhanced the management of Remote Desktop Protocol (RDP) Shortpath, now available through Group Policy Objects (GPO) and Microsoft Intune, allowing IT teams to implement centralized control over RDP Shortpath behavior across Azure Virtual Desktop (AVD) session hosts and Windows 365 Cloud PCs. RDP Shortpath improves performance and reliability by establishing a direct, UDP-based network connection, reducing latency and enhancing responsiveness for audio and video applications. Prior to this update, managing RDP Shortpath was fragmented, requiring manual adjustments on individual session hosts, which complicated consistent networking behavior. The new centralized configuration allows administrators to enforce Shortpath settings uniformly, reducing administrative overhead and ensuring consistent performance and security controls. Administrators can manage RDP Shortpath settings centrally, control all Shortpath modes, and ensure compatibility with AVD host pool settings. Effective operation of RDP Shortpath requires appropriate network conditions, and policy changes necessitate a restart of session hosts or Cloud PCs.
Search