AppWizard
September 28, 2026
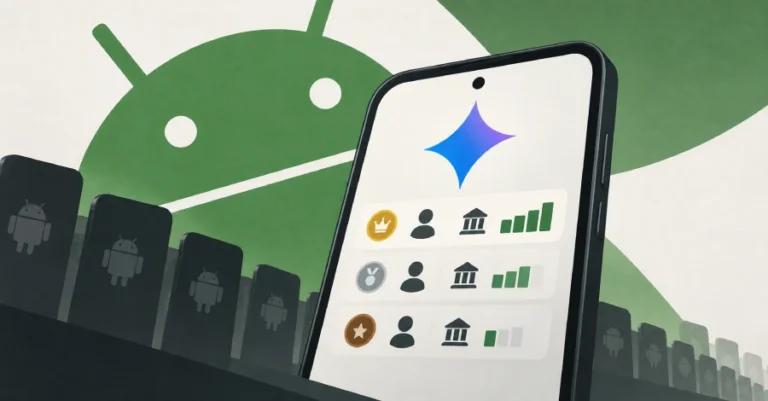
The operators behind RatHat have created an advanced Android banking trojan that allows control of infected devices through a web console. Since April 2026, nearly 100 instances of this console have been identified, indicating a malware-as-a-service model. The console collects sensitive data from compromised phones, including text messages and passwords. It uses Google's Gemini AI to assess victims' bank balances, categorizing them into high-value and mid-value segments, but does not facilitate financial transactions.
The malware has remained largely unchanged since late 2025, but the console has seen significant updates, leading to three new versions: BlackCat Remote Control Management, Panda Workshop V5, and V6. These versions serve as both control interfaces and build tools for creating and distributing malware. The latest version includes templates for deceptive download pages.
RatHat infiltrates devices via text messages and online ads, requesting Accessibility access to read screens and simulate user interactions. This access allows the malware to activate wireless debugging and connect to the Android Debug Bridge (ADB), giving operators elevated privileges to execute commands. A Go program can be deployed to maintain control, even after the app is uninstalled.
Cleafy has tracked console deployments through web code analysis, noting that many IP addresses originate from a Singapore-registered network. The initial console version allowed operators to choose AI providers, but the latest exclusively uses Gemini. RatHat also utilizes Gemini on infected devices to determine tap locations based on screen layouts.
Cleafy has compiled indicators related to the consoles' command-and-control servers, download links, and malware samples, including specific domains, IP addresses, and MD5 hashes. The consoles often use web addresses starting with "admin." and inexpensive top-level domains. Security tools are advised to monitor processes running under the shell user on affected devices.