banking

Tech Optimizer
September 25, 2026
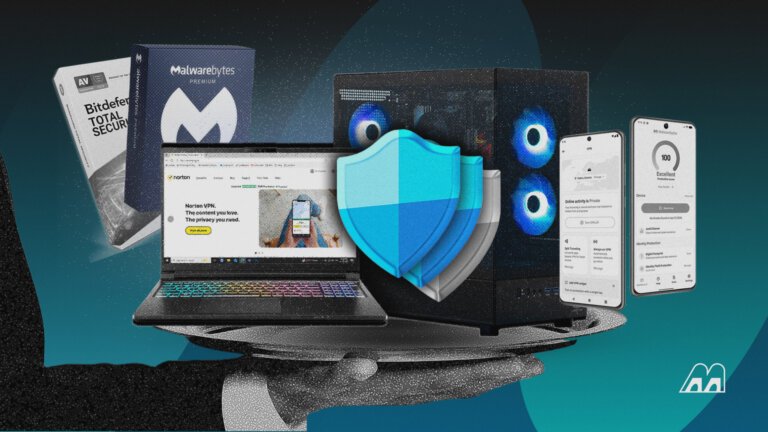
Cybersecurity threats are on the rise, with Verizon’s 2026 Data Breach Investigations Report indicating that 48% of breaches involve ransomware and 31% arise from software vulnerabilities. A review of leading antivirus programs assessed their effectiveness against various threats. Top antivirus software includes: - Bitdefender: Best overall, effective against various threats, perfect score from AV-TEST. - Norton 360: Best all-in-one suite, includes VPN and parental controls, perfect score from AV-TEST. - McAfee+ Premium: Best for families, unlimited device coverage, full marks from AV-TEST. - Malwarebytes: Best for simple protection, user-friendly interface, rated 5.5/6 by AV-TEST. - ESET NOD32: Best for advanced users, lightweight and fast, includes Gamer Mode. - Avast: Best free option, offers various scanning options, straightforward upgrade path. - Microsoft Defender: Built-in for Windows, essential protection, perfect score from AV-TEST. - Intego ONE: Best for Mac users, includes firewall and VPN. - Surfshark Antivirus: Combines antivirus and VPN services, real-time protection. - TotalAV: Best for beginners, combines antivirus with web security tools. The evaluation process included lab data from AV-TEST and AV-Comparatives, hands-on experience, and criteria such as malware protection, false positives, system performance impact, phishing protection, ease of use, platform coverage, additional security features, and pricing. Key metrics from antivirus lab tests include protection scores, false positives, and performance impact. The choice between antivirus software and internet security suites depends on individual needs. Antivirus software remains necessary, especially for Windows PCs, to complement other security measures.
AppWizard
September 19, 2026
Researchers have found that Max, a messaging app mandated by the Russian government, can secretly capture screenshots, access sensitive information, impersonate users, and inject code into other applications. Developed by VK, the app integrates messaging, banking, and government services. Since September 1 of last year, it has been preinstalled on new smartphones, following the blocking of WhatsApp and Telegram. Despite its reach, it is not widely used in political circles, with insiders indicating that compliance with its use is performative.
AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Search