binaries

AppWizard
October 11, 2026
A research team from Turkey, led by Erdal Başaran and Ömer Okucu of Ağrı İbrahim Çeçen University, along with Yusuf Alaca from Hitit University, has developed an innovative detection framework for Android malware that utilizes a visual approach. This framework transforms key features of Android applications into images, allowing a Vision Transformer to differentiate between benign software and malware. The researchers created two types of images from static and dynamic analysis features: a conventional 2D grayscale image and a QR code image. Separate Vision Transformer models were trained on each image type, and spatial pooling features were extracted from deeper layers to create a comprehensive representation of application behavior. To refine the fused feature vector, Recursive Feature Elimination (RFE) was employed, enhancing classification clarity and reducing computational load. The final classification utilized a majority-voting ensemble strategy, achieving a detection accuracy of 98.72 percent, surpassing standalone models. The study demonstrates that the multimodal system outperforms individual grayscale or QR code pathways. The dataset used is publicly available, promoting reproducibility. The framework's reliance on static and dynamic analysis features allows it to adapt to new threats, and the novel QR code representation offers distinctive visual signatures of malicious behavior. However, challenges remain regarding feature extraction quality and computational demands.
AppWizard
October 6, 2026
Scrcpy 5.0 is a lightweight, open-source tool for screen mirroring Android phones to PCs, released by developer Romain Vimont on GitHub. Key features include: - Native hardware-accelerated video decoding, reducing desktop CPU usage by up to 10 times. - Improved input latency due to offloading video decoding to the graphics card. - Enhanced audio capture capabilities, allowing capture of all audio streams. - Official native Windows on ARM64 binaries for Snapdragon-powered laptops. - Bug fixes and refinements, including improved video buffering and resolution of keypress dropping bugs. Hardware decoding is enabled by default, with an option for users to control or disable it. Scrcpy 5.0 follows the previous version's enhancements in flex display handling.
BetaBeacon
October 4, 2026
Winlator is a free, open-source Android application that translates Windows game instructions into ARM instructions on the fly. It uses Wine, Box64, Box86, DXVK, VKD3D, and a graphics translation stack to achieve this. The performance of Winlator depends heavily on the chip doing the translation.
Winsage
October 4, 2026
Tech enthusiast SupraGSX has introduced support for Nvidia's Pascal-era graphics cards (10-series and Quadro P2000-P6000) on the Windows XP 32-bit platform through a custom driver called ForceWare 382.69. This driver combines legacy and modern technology, integrating firmware from Quadro 376.84 and supporting features from GeForce 378.78 designed for Windows 7. Supported graphics cards include GeForce GTX 970, 980, 980 Ti, GTX TITAN X, GTX 1060, 1070, 1070 Ti, 1080, 1080 Ti, GTX 1050 Ti (experimental), Quadro M4000, M5000, M6000, P2000, P2200, P4000, P5000, P6000, and additional OEM variants of GTX 950 and GTX 960. The driver also supports DisplayPort HBR2 and HBR3, ensuring HDMI 2.0 identification and improved HDMI/DVI handling. User feedback has been positive, particularly for ultrawide screens at high refresh rates. The project offers an installer package for download, and modders can access build instructions for modifications. There are inquiries about Windows XP 64-bit support, but a previous fork has been removed, with binaries still available on Mega. Users are advised to proceed with caution due to the unofficial nature of the drivers.
AppWizard
September 19, 2026
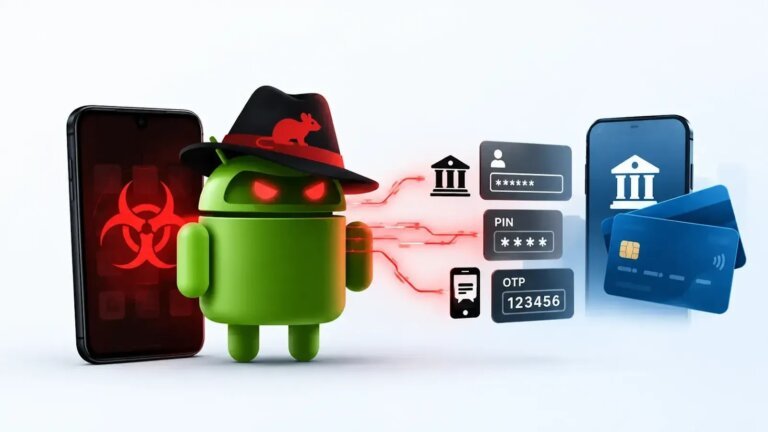
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Winsage
September 16, 2026
David Plummer, a former Microsoft engineer, was the primary author of Windows XP's Product Activation system, which included the infamous product key FCKGW. This key became widely used on pirated copies of the operating system. Plummer created the activation system by compressing and encrypting disc data, ensuring its security. The FCKGW key was specifically tied to certain data configurations, making it ineffective on standard XP CDs. A piracy group, Devils0wn, leaked a complete Windows XP Pro Corporate ISO and the valid FCKGW key just five weeks before the official launch, allowing unauthorized installations. Microsoft responded by blacklisting product IDs associated with the compromised keys in Service Pack 1 and blocking updates for installations using the FCKGW key in Service Pack 2. Valid, un-leaked Volume License Keys (VLKs) remained functional for years after the incident. Plummer noted that the media and the key were leaked before the product reached stores, preventing the intended hardware-binding from functioning.
Search