BitLocker recovery

Winsage
September 25, 2026
The September update for Windows 11 caused significant disruptions, including failures in USB audio functionality and the File History feature. This follows a trend of issues over the past months, with August experiencing printer and PDF problems, July affecting certain Dell PCs, and June reporting startup issues and BitLocker recovery failures. In total, eight out of nine months this year have had at least one major issue. A recurring BitLocker user lockout problem has also been noted. Despite these issues, Windows 11 has improved in overall stability, with fewer system crashes. Windows 10 has maintained stability by focusing solely on security updates since support ended in October 2025, avoiding new feature rollouts. Users satisfied with Windows 10's features may prefer to stay with it for stability. Windows 11 users facing instability can roll back updates or use the Known Issue Rollback feature to revert problematic non-security features.
Winsage
September 7, 2026
Microsoft is facing significant security and reliability issues, particularly related to system startup, BitLocker recovery, and updating Secure Boot certificates. Users have expressed confusion over these complexities, especially regarding Microsoft Defender Antivirus errors. These problems stem from a tumultuous period before the launch of Windows 11, including changes to the TPM requirement and the extension of Windows 10's life. Despite increased security patches, underlying issues remain, leading to user skepticism about the reliability of Windows systems.
Winsage
August 3, 2026
Microsoft is focusing on enhancing Windows 11 by addressing fundamental improvements, as highlighted by CEO Satya Nadella during the fiscal 2026 fourth-quarter earnings call. The company is investing in maintaining high quality and fundamentals for the operating system, with ongoing efforts to fix user concerns. Enhancements include testing a movable taskbar, reducing RAM consumption, fixing memory leaks, improving slow startup times, and updating File Explorer and Windows Search. The introduction of the Low Latency Profile update aims to improve responsiveness in the Start menu and shell. Microsoft has also removed the Copilot branding from certain applications to streamline the user experience. This renewed focus follows a challenging year with problematic updates, including a mandatory update in June that caused boot failures and other issues, prompting an emergency update in July. Financially, Microsoft's More Personal Computing revenue declined by 4%, with Windows OEM and Devices revenue dropping by 7%.
Winsage
July 29, 2026
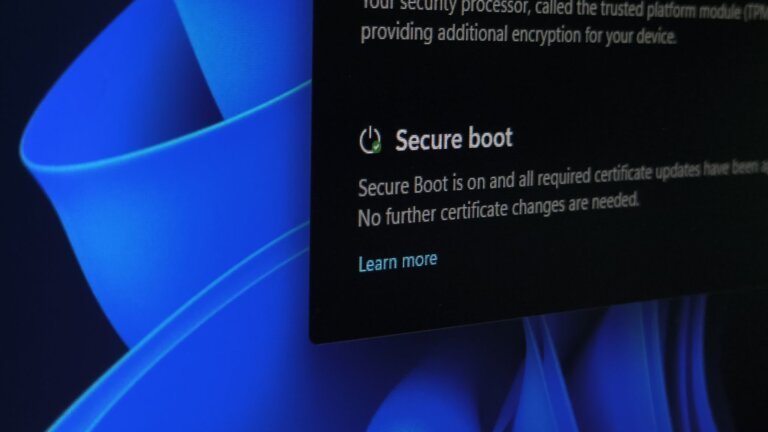
Microsoft reassured Windows 11 and Windows 10 users that their PCs will continue to boot normally and receive updates even if they have not yet received the new Secure Boot 2023 certificates. The rollout of these certificates is expected to continue over the upcoming months. The initial Secure Boot certificate expired on June 24, 2026, and Microsoft has been replacing older 2011 certificates since 2024. The latest update, KB5101650, transitioned Windows 11 to OS builds 26200.8875 and 26100.8875 for versions 25H2 and 24H2, respectively. The 2023 certificates replace older certificates with modern cryptographic standards, allowing Microsoft to deliver DBX revocation updates without interruption. Devices using the 2011 KEK can only receive DBX updates signed with that key, which is no longer valid after June 24. Microsoft has been rolling out the 2023 certificates for the past two years, and many devices remained in a yellow or red status by the June deadline. To check Secure Boot status, users can navigate to Windows Security > Device Security. A green checkmark indicates successful application of the certificates, while yellow and red alerts indicate compatibility issues or firmware incompatibility. PCs that are older or operating in Legacy BIOS mode will not receive the updates. Windows 10 also receives Secure Boot updates, but enrollment in Extended Security Updates (ESU) is required.
Winsage
July 23, 2026
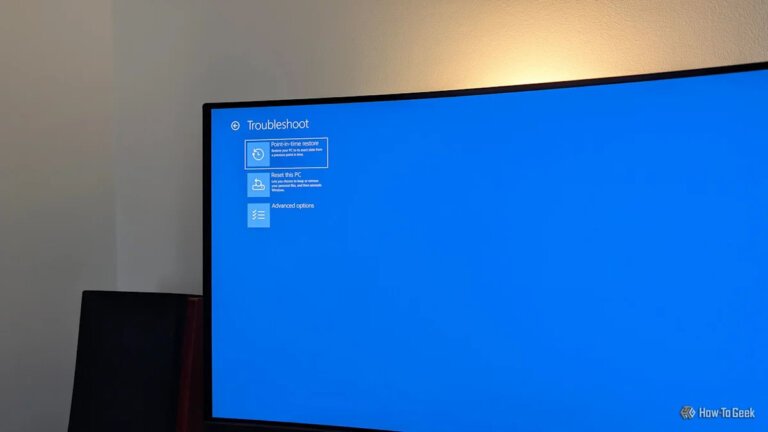
Since June 23, Microsoft has been implementing a point-in-time restore feature on Windows 11, which is enabled by default for Home and Pro editions when the system drive exceeds 200 GB. This feature captures a complete snapshot of the machine approximately every 24 hours using the Volume Shadow Copy service, including system, applications, settings, and local files. Users can revert to a previous state in case of issues, but restoring from a snapshot older than 48 hours will erase all changes made since then, except for OneDrive data. The feature retains snapshots for up to 72 hours and reserves 2% of drive space, capped at 50 GB. If free space drops below 20 GB, older snapshots are deleted. Restoration occurs locally through WinRE, and users need a BitLocker recovery key if the drive is encrypted. After a restore, the feature pauses and requires user consent to resume. Snapshots from upgraded editions are not accessible, and only the Enterprise edition allows adjustments to snapshot settings. The feature can be disabled in system settings. It is not a backup solution, and users are advised to maintain separate backups for important files.
Winsage
July 19, 2026
Microsoft held an OEM Secure Boot Office Hours event with manufacturers like Acer, Asus, Dell, and HP to discuss issues related to the Windows 11 Secure Boot 2023 certificate rollout. Many IT administrators left with unresolved concerns, particularly regarding Secure Boot certificate errors. Participants reported persistent problems, including failures of suggested solutions from official documentation to apply to their hardware configurations. Ed Tittel shared his experience with compliance issues related to CA-2023 certificates, noting that ASUS motherboards sometimes required Secure Boot to be disabled temporarily, while MSI models exhibited erratic behavior. ASRock systems needed manual key resets, and documentation was lacking. Devices from Dell, HP, and Lenovo performed better but still faced staggered rollouts and required multiple reboots for BIOS updates. Specific issues raised included HP's BitLocker recovery loop persisting even with the latest BIOS, challenges with legacy device support from HP, devices showing Secure Boot Status as Unknown, and failures in updating the KEK on HP EliteBooks. Some questions from IT administrators regarding Dell and HP went unanswered during the session. The experiences highlighted a trend of Secure Boot issues across multiple OEMs, not limited to a single vendor. IT administrators are advised to pilot updates on representative hardware, back up BitLocker recovery keys, and consult OEM-specific advisories. The unresolved issues reflect common challenges faced by users, indicating that problems with Secure Boot certificate deployments are widespread across various manufacturers.
Winsage
July 19, 2026
Microsoft has introduced point-in-time restore for Windows 11 users, enhancing the traditional System Restore. This new recovery tool allows users to recover their PCs from software issues, problematic drivers, or faulty updates, even when Windows won’t boot. It uses the Volume Shadow Copy Service (VSS) to automatically generate restore points every 24 hours, which include both system and user files, unlike System Restore. Point-in-time restore manages storage by deleting restore points after 72 hours and integrates seamlessly into Windows Settings, being activated by default for volumes over 200GB. Users with smaller volumes must activate it manually. It also incorporates Reserved Storage to ensure restore points do not consume regular disk space. The feature is available on Windows 11 Home and Pro editions with the installation of the optional Preview Update KB5095093. Users can access point-in-time restore through Windows Settings under System > Recovery, and initiate recovery via the Windows Recovery Environment (Windows RE).
Search