A study by Proton found tracker code associated with companies in China and Russia in many of the most downloaded free Android games in the US and Europe.
On September 24, Microsoft reported an issue affecting devices that installed the August 27 preview update for Windows 11, causing a black screen after sign-in and preventing the desktop from loading correctly. This issue primarily impacts Azure Virtual Desktop (AVD) hosts using FSLogix with existing user profiles. The affected OS versions are Windows 11 versions 26H1, 25H2, and 24H2, and the causal update is KB5120998. Microsoft has issued interim workarounds, including a manual desktop launch and a Known Issue Rollback (KIR), which will be automatically delivered to non-enterprise devices. Affected enterprise-managed devices require manual deployment of the KIR policy. The black screen issue is part of a series of update-related problems for Windows 11 in 2026, while Windows 10 has experienced fewer issues during the same timeframe.
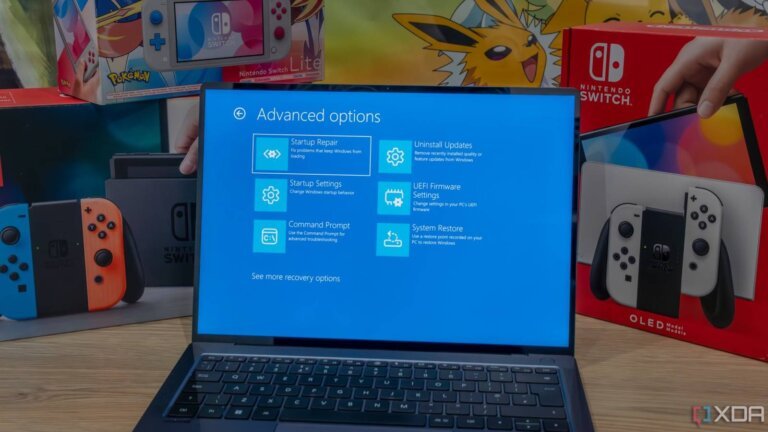
Windows 11 requires drivers to be digitally signed, a policy aimed at enhancing security by preventing unauthorized code from executing at the kernel level. This requirement, which began with Windows Vista and became mandatory with Windows 10, version 1607, has tightened over the years, especially with the introduction of UEFI Secure Boot and TPM in Windows 11. While this enforcement protects against malware and supports anti-cheat systems in gaming, it limits user autonomy and imposes significant challenges for developers, particularly those working on smaller projects. In contrast, Linux allows users more freedom to modify their systems, though this flexibility can compromise security.
Ads are prevalent on Android devices, leading users to choose between enduring them or paying for premium subscriptions. BlockAds is a free, open-source app that blocks ads on Android by creating a local VPN, filtering traffic without requiring device rooting. Users can also employ DNS filtering to block ads by changing their DNS server settings, with services like AdGuard and NextDNS available for this purpose. Firefox supports the uBlock Origin extension for ad-blocking on Android, while NewPipe allows users to watch YouTube videos ad-free and access premium features. The DuckDuckGo browser includes a built-in YouTube ad blocker, and the Brave browser automatically blocks ads and trackers without additional setup.
Endpoint security is a suite of technologies and processes designed to protect devices connected to a business network from cyber threats. It includes various devices such as laptops, smartphones, tablets, servers, and IoT devices. Endpoint security employs a multi-layered approach, scanning for malware, regulating applications, and monitoring device activity for unusual behavior. It is distinct from antivirus software, encompassing a broader range of protective measures, including firewalls, encryption, application controls, patch management, and Endpoint Detection and Response (EDR). The rise of remote work and the increasing number of devices create a larger attack surface, making endpoint security essential for preventing breaches and safeguarding business operations.
Cybersecurity threats are on the rise, with Verizon’s 2026 Data Breach Investigations Report indicating that 48% of breaches involve ransomware and 31% arise from software vulnerabilities. A review of leading antivirus programs assessed their effectiveness against various threats.
Top antivirus software includes:
- Bitdefender: Best overall, effective against various threats, perfect score from AV-TEST.
- Norton 360: Best all-in-one suite, includes VPN and parental controls, perfect score from AV-TEST.
- McAfee+ Premium: Best for families, unlimited device coverage, full marks from AV-TEST.
- Malwarebytes: Best for simple protection, user-friendly interface, rated 5.5/6 by AV-TEST.
- ESET NOD32: Best for advanced users, lightweight and fast, includes Gamer Mode.
- Avast: Best free option, offers various scanning options, straightforward upgrade path.
- Microsoft Defender: Built-in for Windows, essential protection, perfect score from AV-TEST.
- Intego ONE: Best for Mac users, includes firewall and VPN.
- Surfshark Antivirus: Combines antivirus and VPN services, real-time protection.
- TotalAV: Best for beginners, combines antivirus with web security tools.
The evaluation process included lab data from AV-TEST and AV-Comparatives, hands-on experience, and criteria such as malware protection, false positives, system performance impact, phishing protection, ease of use, platform coverage, additional security features, and pricing.
Key metrics from antivirus lab tests include protection scores, false positives, and performance impact. The choice between antivirus software and internet security suites depends on individual needs. Antivirus software remains necessary, especially for Windows PCs, to complement other security measures.
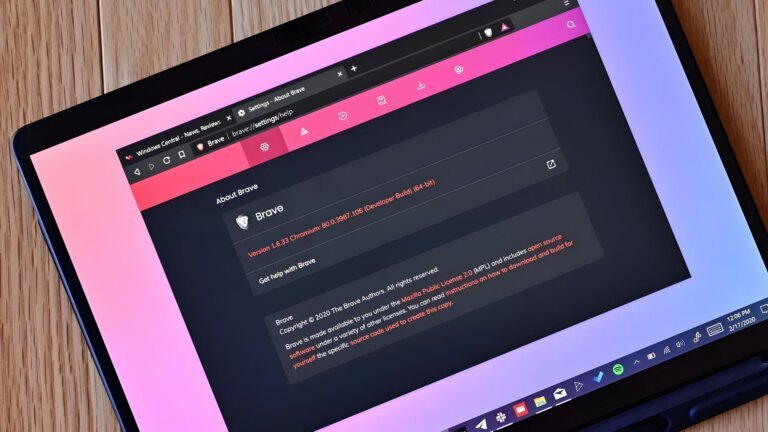
Microsoft Edge users recently experienced a significant change as advertisements flooded the interface following the discontinuation of support for the uBlock Origin ad-blocking extension. This shift resulted from the transition away from Manifest Version 2 (MV2) extensions to Manifest Version 3 (MV3), which diminishes the effectiveness of ad blockers. As a result, users are considering alternative solutions or switching browsers. Brave has emerged as a viable option, maintaining support for MV2 extensions and offering effective ad-blocking features through its Brave Shields. Users can selectively block elements easily, although it lacks some features of uBlock Origin. The author plans to use Brave Shields for browsing while keeping the option to revert to uBlock Origin if needed.
The Max messenger, developed by VK, has significant user tracking capabilities. A report from InterSecLab revealed that:
- Max's features can vary for individual users without app updates.
- It lacks end-to-end encryption, allowing VK access to messages, even in "secret chats."
- Each account can be configured to perform specific actions, such as decrypting messages on VK's servers and blocking messages if a VPN is detected.
- Upon launching, Max reports the user’s network environment to VK, including their public IP address and mobile carrier.
- The app uploads users’ entire address books unencrypted to VK's servers, accessing contacts of non-registered individuals.
- A phone number query can reveal extensive user information without notification.
- Max stops functioning if it detects a VPN, requiring users to disable it to send messages, although workarounds exist.
- New users receive a curated list of recommended channels, primarily featuring state media and pro-government figures.
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Cisco Talos has disclosed a new Windows implant called CLOSEDQUORUM, which operates without human operators by using four commercial large language models (LLMs) to autonomously decide on actions after deployment. The implant is a 16.4-megabyte executable that conducts reconnaissance on the target system and sends structured prompts to the LLMs, which respond with one of four actions: steal, inject, persist, or move. When the "steal" action is chosen, it simultaneously attacks three credential stores, extracting Windows credentials, browser passwords, and cryptocurrency wallet data. The "inject" action uses either Early Bird APC injection or process hollowing based on model recommendations. For persistence, it employs three overlapping mechanisms, including a Registry Run key, a scheduled task, and a WMI event subscription. To evade detection, CLOSEDQUORUM suppresses ETW telemetry and introduces delays before executing actions. It circumvents traditional command-and-control structures by calling legitimate API endpoints, making blocking these domains impractical. Talos introduced the CAIRN toolkit for detecting AI-integrated malware, which operates on metadata and employs rule-based detection. Unlike previous AI-assisted malware, CLOSEDQUORUM automates decision-making processes entirely, highlighting a significant evolution in malware capabilities. Security teams are advised to focus on behavioral detection strategies and utilize the YARA rule and CAIRN toolkit for identifying this threat.