bridge

AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.

AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 19, 2026
ESG reporting standards are becoming increasingly important in mobile technology, affecting various aspects such as data management, material sourcing, energy consumption, privacy, supply chain dynamics, and product accountability. The lifecycle of mobile devices involves raw material sourcing, component manufacturing, device assembly, shipping, marketing, sales, updates, repairs, trade-ins, and disposal. Companies must understand ESG standards to create coherent sustainability narratives and may need to disclose supplier practices, carbon emissions, and governance documentation when partnering with larger firms. Consumers are now asking more questions about the longevity of software updates, repairability, data collection, packaging design, and the accountability of product creators. The rise of connected devices complicates ESG reporting due to extended product lifecycles and the need for ongoing software support. Companies should track product lifespan estimates, warranty data, repair trends, and update schedules to improve product quality and ESG reporting credibility. Emerging tech companies can start their ESG journey by cataloging product claims, consolidating evidence, designating ownership of records, and reviewing product lifecycle information. Global sustainability frameworks exist but may not align with consumer needs for straightforward product information. Successful mobile tech companies will need to bridge formal reporting requirements with accessible product-level communication. Trust and transparency in practices will increasingly influence consumer choices in mobile technology.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Winsage
September 15, 2026
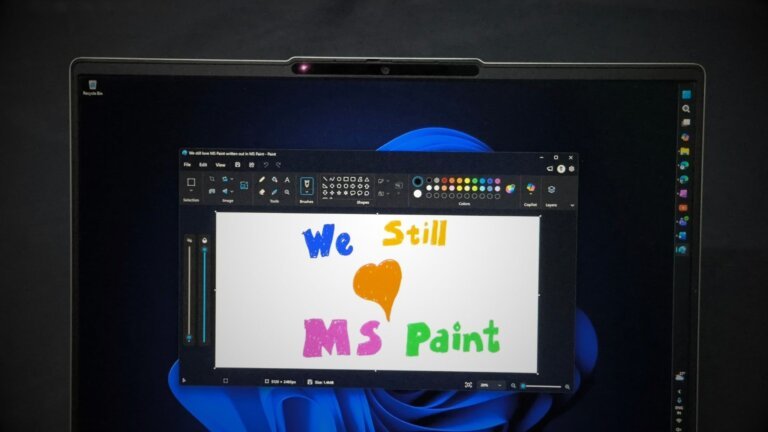
Microsoft's Paint has been a popular tool since its launch in Windows 1.0 in 1985, with over 100 million monthly users reported in 2017. Paint 3D was introduced as part of Microsoft's vision for "3D for everyone," featuring tools like 3D Doodle, Brushes for 3D surfaces, Magic Select, and Mixed Reality Viewer. However, it struggled to resonate with users due to a cumbersome interface and a lack of necessity for 3D capabilities, leading to its deprecation in 2024. By 2021, Paint 3D was no longer preinstalled on new Windows 10 devices, and Microsoft shifted focus back to the original Paint, enhancing it with features like background removal and AI-driven tools. Despite its potential, Paint 3D failed to bridge the gap between casual users and professional 3D software, and an open-source approach could be a way to revitalize it.
Tech Optimizer
September 14, 2026
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
AppWizard
September 14, 2026
Native App AI simplifies the process of converting websites or AI-generated web apps into Android applications ready for the Play Store without needing to rebuild from scratch. It allows users to input a website URL, customize the app's features, and generate APK and AAB files for testing and publishing. The platform supports various features such as push notifications, AdMob monetization, deep linking, and custom branding. It also assists in preparing necessary information for Google Play, ensuring compliance with policies and technical requirements. This service is beneficial for SaaS companies, startups, e-commerce ventures, and creators who have existing web products.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
Search