campaigns

AppWizard
October 16, 2026
The author attended a three-day review event in Los Angeles for Modern Warfare 4, spending nearly 24 hours on the campaign, multiplayer, and DMZ modes. They have been engaged with Call of Duty for over two decades, initially drawn in by the campaigns. The campaign of Modern Warfare 4 features relatable characters, primarily a group of young South Korean marines during a North Korean invasion, and aims to recapture the essence of earlier installments. Key missions include "Mayhem," "Losing Ground," and "Stranded," the latter showcasing a sandbox level with non-linear objectives. Concerns about integrating Warzone mechanics into single-player gameplay were alleviated by the assurance that the map was designed specifically for the campaign. The narrative includes Captain Price but feels disjointed, with his character fading from the story. Overall, Modern Warfare 4 is noted for its robust campaign, extravagant set pieces, and solid gunplay, marking a return to form for the series.
AppWizard
October 16, 2026
A report from Bitdefender reveals a malware campaign named "Midnight Mimosa" affecting budget and midrange Android smartphones, particularly those using low-energy MediaTek chipsets. This malware, embedded in devices marketed under various labels like Cubot and Doogee, operates through an application called "System" (package name com.android.system.lite) that displays hidden ads and can allow hackers to control the devices. Thousands of devices have been tracked with this malware, with 13% of affected devices located in Mexico, 8% in the United States, and less than 3% in Canada. The malware's source traces back to Android ODM Shenzhen Zediel. Additionally, Bitdefender identified 13 other ad fraud-related apps signed by the same entity that were previously available on the Google Play Store. Major manufacturers like Google, Motorola, and Samsung have security protocols to protect their firmware, unlike the affected budget brands.
AppWizard
October 15, 2026
Cybersecurity experts from Bitdefender have found that budget Android smartphones, such as the Doogee S200 X, Doogee Fire 3 Max, and Cubot KINGKONG X, may come pre-loaded with malware embedded in their firmware, posing significant security risks. This malware is introduced during the manufacturing process, particularly affecting devices with MediaTek chipsets. Thousands of users in around 150 countries, including Mexico, France, Italy, the United States, Germany, Brazil, and Spain, have been impacted. Bitdefender identified a network of 32 malicious applications disguised as legitimate utilities that generate fraudulent ad impressions. Some infected phones can function as residential proxies for criminal activities, including spam campaigns and DDoS attacks. Uninstalling the malicious app may not eliminate the infection if it is integrated into the system software, potentially requiring firmware-level remediation. Buyers of budget phones should research manufacturers' supply chain control and commitment to security updates.
Winsage
October 14, 2026
Microsoft's October 2026 security updates address 1,411 vulnerabilities, marking the largest Patch Tuesday release to date. The update includes 70 vulnerabilities classified as Critical, with 57 related to remote code execution, 11 to elevation of privilege, and two to spoofing. Key vulnerabilities include CVE-2026-96951, a Windows Shell security bypass being actively exploited, CVE-2026-108398, which affects .NET Framework and allows bypassing Windows Defender Application Control, and CVE-2026-92707, a denial-of-service vulnerability in MessagePack-CSharp. The release coincides with critical Windows support deadlines, with the final regular update for Windows 11 24H2 Home and Pro and Windows 10 Enterprise LTSB 2016 occurring on October 13. Organizations are advised to prioritize the exploited vulnerabilities, ensure relevant updates are applied, and validate application-control behavior.
Tech Optimizer
October 10, 2026
Every year, billions of dollars flow through online crowdfunding platforms, leading to donor concerns about the allocation of funds. Traditional crowdfunding applications lack transparency, often leaving funds in unverified balances without real-time auditability or guarantees against double-allocations. GoodCause, a social impact platform, aims to address this issue by creating a system that ensures financial integrity and atomic fund distribution. Its architecture is based on mobile-first delivery, atomic auditability, and strict data isolation, utilizing technologies such as React Native, FastAPI, and PostgreSQL. The platform incorporates a mobile client for cross-platform navigation, a backend API for domain-driven routing, a database with Row-Level Security, and a payment gateway for secure transactions. A significant engineering challenge is preventing race conditions and double-spending in concurrent donation scenarios.
AppWizard
October 6, 2026
Frosthaven Digital will release its full 1.0 version on October 15. The game has been enhanced with new features, classes, and missions to align closely with the original board game. Team Wargamer awarded it a 10/10 rating. The digital format allows players to complete scenarios in about 30 to 40 minutes, compared to two to three scenarios in five hours for the physical version. A "custom save" feature will enable players to edit saves and import campaigns from physical to digital formats. The 1.0 version is 99% mechanically accurate to the board game, with some minor visual adjustments. Players can unlock a new hero, the Shattersong, late in the game, which plays a supportive role. There are 137 missions in total, with 64 as the main story and many side quests available. The onboarding process will include a three-mission tutorial and a four-mission prequel.
Winsage
September 24, 2026
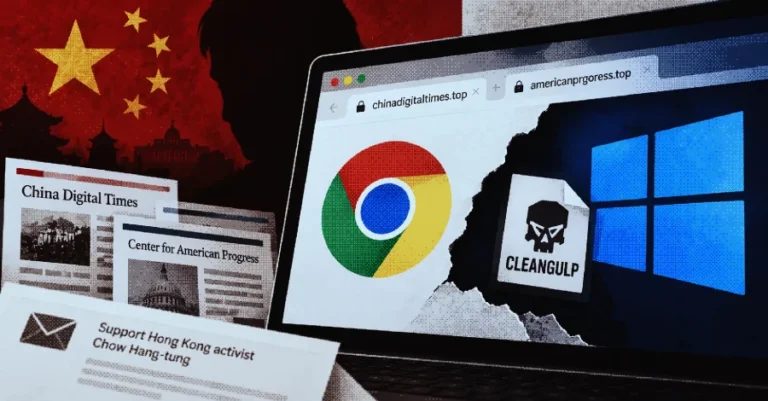
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Search