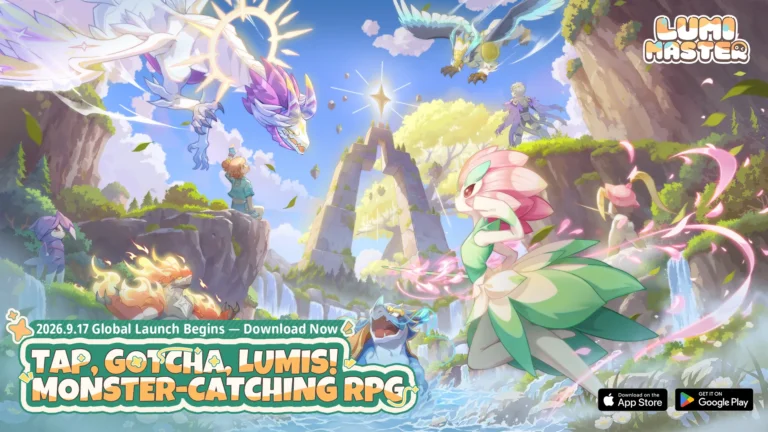
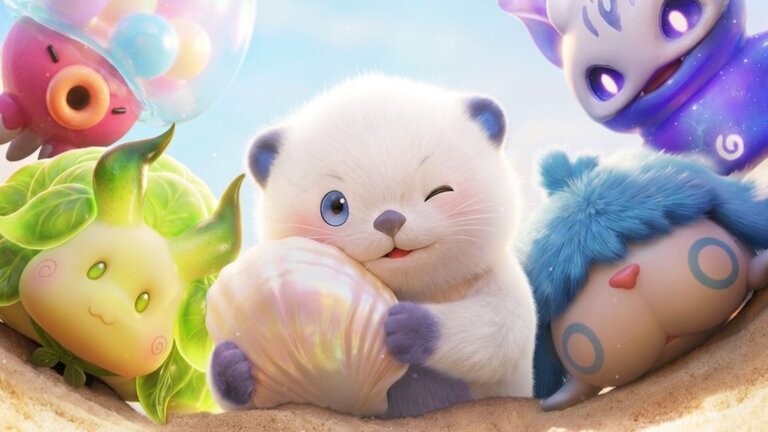
Lumi Master is a portrait-mode RPG where players catch, collect, and train Lumis in the fantastical realm of Lumia. Lumis are unique creatures that evolve based on how they are raised. Players can freely roam, explore, and capture Lumis using cards, adding them to their team. The game features charming 2D fantasy art and an Auto-play Feature for relaxed gameplay. Players can also interact with other adventurers, trade items, socialize, and team up for ranking battles.
Researchers have found that Max, a messaging app mandated by the Russian government, can secretly capture screenshots, access sensitive information, impersonate users, and inject code into other applications. Developed by VK, the app integrates messaging, banking, and government services. Since September 1 of last year, it has been preinstalled on new smartphones, following the blocking of WhatsApp and Telegram. Despite its reach, it is not widely used in political circles, with insiders indicating that compliance with its use is performative.
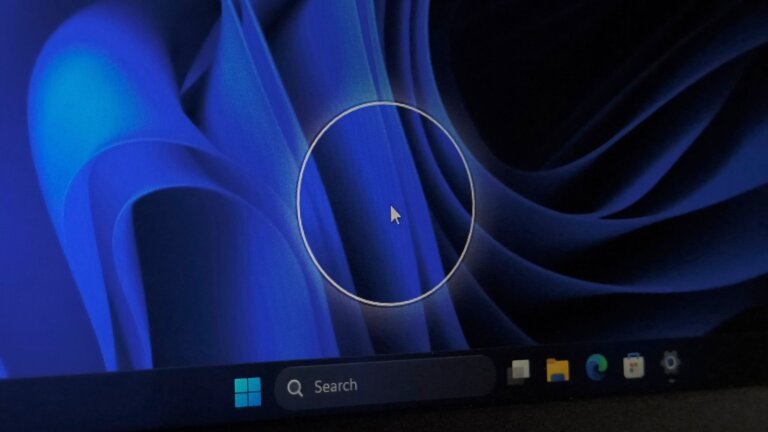
Microsoft has released a modernized version of the Mouse Indicator in Windows 11 Insider Preview Build 26340.9502 on September 18, 2026. This update features a new animation that can be activated through Accessibility settings, allowing users to keep the indicator on until they press the Esc key. Users can choose to activate the Mouse Indicator with a single or double Ctrl press. The previous version displayed a simplistic circle around the pointer briefly, while the new version offers a smoother, more dynamic animation. The feature is currently available only in the Insider build for the Experimental channel, and users can enable it by navigating to Settings > Accessibility > Mouse pointer and touch > Mouse indicator.
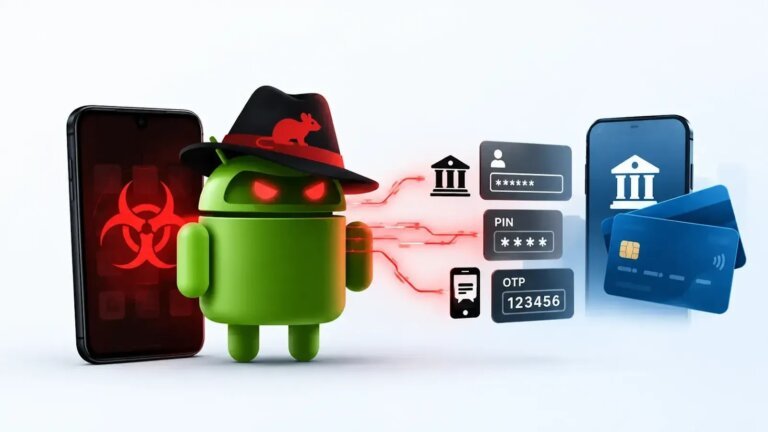
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
The Russian government is pressuring citizens to download a mobile app called "Max," which has raised privacy and surveillance concerns. Max is a popular messaging platform in Russia and integrates messaging, government services, and payment functionalities. Research by a University of Michigan team found that Max can capture users' screens without consent, access sensitive information, impersonate users, and potentially enable cyberattacks via code injection. Despite these concerns, many Russians still use alternative messaging platforms like Telegram and Signal. Some government officials are using separate devices for Max, indicating unease about its surveillance capabilities. The app is linked to a social media company connected to the Russian government, and President Putin may have an indirect financial stake in it.
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox.
The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception.
Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client.
The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures.
RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands.
The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
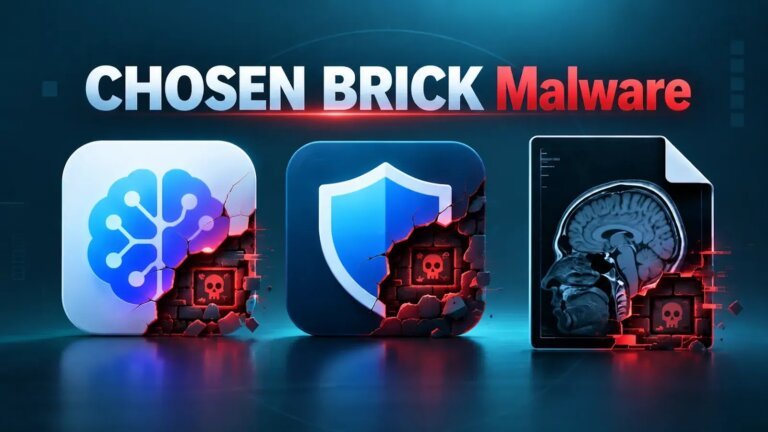
Iranian state-affiliated cyber actors are targeting dissidents, activists, and journalists using fake AI applications, counterfeit antivirus tools, and fabricated MRI scan results, primarily through a spyware family known as CHOSEN BRICK, which is designed for Windows systems. This campaign has been active since at least 2025 and affects individuals globally, including in the UK, US, and Netherlands. The malware establishes persistence via the Windows Registry Run key and communicates through Telegram, utilizing unique Bot IDs for each victim. CHOSEN BRICK is capable of extensive data collection, including capturing screenshots, recording audio, and stealing email content. Personal information from victims has been found on pro-Iranian leak sites, increasing harassment risks. Security measures should include monitoring for suspicious Registry entries and unusual communications, while users are advised to avoid unsolicited software installations and keep their systems updated. The FBI refers to this malware family as HEAVYGRAM.
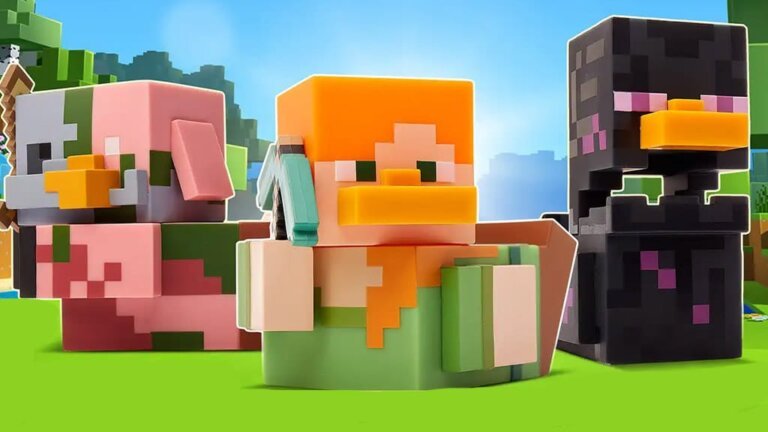
Tubbz is expanding its Minecraft lineup with three new collectible rubber ducks: Alex, an Enderman, and a Zombified Piglin. The Enderman features a slack-jawed expression and purple eyes, the Zombified Piglin has a half-decayed look and a golden sword, and Alex is equipped with a diamond pickaxe. Each comes in a themed bathtub display with a sticker and an exclusive print. They are available for purchase at select retailers and on tubbzus.com, with a suggested retail price of .99 - .99.
Aniimo is not a gacha game, as it lacks traditional banner systems. It monetizes through a cosmetics shop where players can buy Lumin Crystals with real money for outfits and accessories. Some cosmetics are available for free, but premium items are often behind a paywall. The game also features shop bundles and a battle pass called the "Companion Handbook," which includes free and premium tiers. Players can acquire Aniimo by using Aniipods to capture creatures, hatching eggs, completing events, or progressing through the battle pass. Legendary Aniimo can be captured by collecting unique tokens and using a special Aniipod.