certificate expiration

Winsage
October 12, 2026
Microsoft has reminded IT administrators about the expiration of certificates that enable trusted connections between Windows devices and Windows Update servers, set to expire in May and June of 2027. Devices without replacement certificates by these deadlines may lose access to Windows Update services. Most supported Windows devices will receive new certificates automatically through security updates, but older or infrequently updated systems may require manual intervention. Organizations that do not update their devices risk losing access to critical updates, particularly unsupported Windows versions that will not receive necessary certificate updates. IT teams should audit device inventories and ensure compliance with updates, as systems on supported versions will obtain replacement certificates seamlessly. Upgrading unsupported systems is essential, and organizations are encouraged to conduct audits and expedite upgrade projects to avoid losing access to Windows Update.
Winsage
October 11, 2026
Windows machines that are not current with updates will face changes in access to Windows Update due to two critical certificate expirations on May 17, 2027, and June 19, 2027. Supported versions must install specific security updates before these dates to maintain access. - Windows 11, version 25H2 and later: No action required. - Windows 11, version 24H2 and Windows Server 2025: Must install the September 2025 Windows security update or later, before June 19, 2027. - Other in-support Windows 11 versions and Windows Server 2022: Must install the July 2026 Windows security update or later, before June 19, 2027. - In-support Windows 10 versions: Must install the July 2026 Windows security update or later, before June 19, 2027. - Windows 10 Enterprise 2019 LTSC, Windows Server 2019, and Windows Server 2016: Must install the July 2026 Windows security update or later, before May 17, 2027. - Any other Windows version: Upgrade to a supported release to maintain access. Devices that are up to date will continue receiving updates without interruption, while those that are behind will lose access to Windows Update services after the expiration dates. Out-of-support versions will lose access entirely. The notice regarding the certificate expiration was posted on October 8, 2026, and reiterated on October 10, 2026.
Winsage
October 9, 2026
Microsoft will stop providing security updates for devices running unsupported versions of Windows after the Windows Update certificate rotation in May and June 2027, specifically on May 17, 2027, and June 19, 2027. Users and administrators are advised to upgrade to a supported version of Windows before these dates to maintain system integrity. Replacement certificates have already been issued for supported versions, requiring no action for those systems. Specific upgrade guidance includes: - Windows 11, version 25H2 and later: No action required. - Windows 11, version 24H2 and Windows Server 2025: Install the September 2025 security update or later before June 19, 2027. - Other supported versions of Windows 11, Windows Server 2022, and Windows 10: Install the July 2026 security update or later before June 19, 2027. - Windows 10 Enterprise 2019 LTSC, Windows Server 2019, and Windows Server 2016: Install the July 2026 security update or later before May 17, 2027. - Other Windows versions: Upgrade to a supported version of Windows client or Windows Server. IT administrators should evaluate their networks for unsupported Windows versions and ensure monthly updates are applied to supported devices. The directive does not apply to devices receiving updates through Windows Server Update Services (WSUS). Microsoft also announced the rollout of Windows 11, version 26H2, as an enablement package for eligible systems.
Winsage
July 20, 2026
On July 14, 2026, Microsoft released cumulative update KB5101650 for Windows 11 versions 25H2 and 24H2, addressing OS Builds 26200.8875 and 26100.8875. This update includes essential security fixes, updates to Secure Boot certificates, and enhanced Remote Desktop Protocol (RDP) defenses against phishing attacks. It consolidates July 2026's security content, addressing known vulnerabilities and introducing functional improvements. The update is critical for minimizing exposure to identified threats and is prioritized for systems managing remote access or nearing certificate expiration. The update enhances Remote Desktop security by supporting SHA-2 certificate thumbprints while retaining SHA-1 for legacy compatibility. It includes new Group Policy options to mitigate phishing risks associated with malicious .rdp files. The curl upgrade to version 8.21.0 incorporates security patches for command-line tools in Windows environments. Secure Boot certificates are automatically updated through Windows updates, ensuring boot security across various hardware. KB5101650 installs primarily through the Windows Update interface, requiring a restart to activate changes. Enterprise environments can use the Microsoft Update Catalog for manual distribution. A temporary restriction affects certain Dell devices with Intel Innovation Platform Framework drivers, which Microsoft plans to address in a future update. The cumulative update resolves a total of 622 Microsoft CVEs, including 416 affecting Windows components. Users are advised to verify and install the update promptly to secure the full suite of improvements.
Winsage
July 14, 2026
Microsoft has acknowledged that several older Secure Boot certificates have expired, necessitating updates for Windows 10 and 11 users. A temporary halt in the issuance of new Secure Boot certificates affects specific PCs, particularly various HP models. Most PCs will receive updates automatically through Windows Update, but some may require a firmware update from the manufacturer. Users may see messages indicating that Secure Boot certificate updates are paused or blocked due to known issues or hardware/firmware limitations. Until manufacturers like HP release necessary firmware updates, users cannot update their Secure Boot certificates. Although the immediate risk from expired certificates is low, it is expected to increase over time. Devices with un-updated Secure Boot certificates will continue to function normally, but they will not receive new security updates, making them vulnerable to emerging threats. Essential features that rely on updated security measures may cease to function correctly as new security challenges arise.
Winsage
June 29, 2026
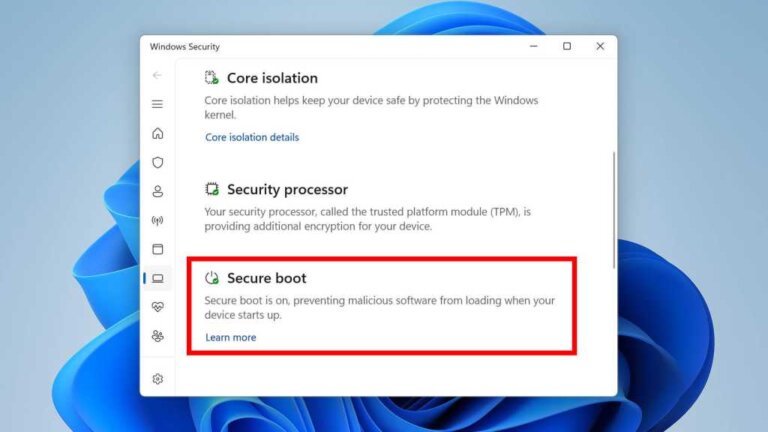
Major PC manufacturers, including HP, Dell, ASUS, Lenovo, MSI, Acer, Samsung, LG, and Microsoft’s Surface division, have provided guidance on transitioning to new Secure Boot certificates as the expiration of Microsoft’s 2011 certificates approaches. The expiration will occur in three phases: Microsoft Corporation KEK CA 2011 expired on June 24, 2026; Microsoft UEFI CA 2011 expired on June 27, 2026; and Microsoft Windows Production PCA 2011 is set to expire on October 19, 2026. Microsoft has begun rolling out replacement certificates through Windows Update, contingent on OEMs providing compatible BIOS updates. ASUS offers detailed documentation for both consumer and commercial devices, confirming that most users will receive updates automatically. Lenovo provides direct download links for BIOS updates organized by product family and specifies which products will not receive updates. Dell's support article covers its entire product lineup, noting that devices with an End of Service Life before January 1, 2026, will not receive updates. HP outlines a dual-track approach for updates, with specific timelines for commercial PCs. Microsoft's Surface devices receive updates directly from Microsoft, while MSI categorizes guidance based on processor generation for its laptops. Acer emphasizes backing up the BitLocker recovery key and provides a model table for confirmed BIOS release dates. Samsung confirms that all PCs running Windows 10 or 11 will function normally post-expiration, but security updates will cease. LG has released a guide for checking BIOS updates for its PCs. To verify if a PC has the 2023 certificates, users can check the Secure Boot section in Windows Security. A green checkmark indicates successful application, while yellow or red icons indicate pending updates or incompatibility. Microsoft has pushed the certificates to all eligible devices as of June 2026.
Winsage
May 26, 2026
Microsoft will begin the expiration of Secure Boot certificates on most PCs in June, marking the end of a 15-year period of stability. This affects all PCs manufactured before 2023. Users will likely need to perform multiple restarts during the update process, which includes pushing data into firmware and loading a new bootloader. Ignoring the Secure Boot deadline in June 2026 may lead to significant security risks, as Microsoft will stop providing essential boot updates and malware blacklists. The Windows Security App has been updated to help users monitor these changes, and users should check for warnings indicating the status of Secure Boot. It is important for Windows 10 users to ensure they are enrolled in the Extended Security Updates (ESU) program to avoid vulnerabilities.
Winsage
March 6, 2026
Every Secure Boot-enabled Windows PC relies on cryptographic certificates issued by Microsoft in 2011 for boot process integrity. The first of these certificates will expire on June 24, 2026, impacting the ability to receive future security updates. Microsoft is rolling out replacement certificates through Windows Update, requiring collaboration between Microsoft, PC manufacturers, and users. Three critical certificates will expire: the Microsoft Corporation KEK CA 2011 and Microsoft UEFI CA 2011 in June 2026, and the Microsoft Windows Production PCA 2011 in October 2026. The new certificates introduced in 2023 have a restructured functionality to enhance security. Not all PCs are affected; newer devices manufactured since 2024 come with the new certificates. Windows 10 users face challenges as support ends in October 2025, and unsupported devices will not receive updates. Home users should ensure automatic Windows updates and check for firmware updates, while enterprise environments must verify firmware updates before applying certificate updates. The first certificate expiration is on June 27, 2026.
Winsage
February 23, 2026
Windows Server administrators should update Secure Boot certificates before the June 2026 expiration date. Microsoft has held Secure Boot Ask Microsoft Anything (AMA) sessions in December 2025 and February 2026, with recordings available for those who missed them. Upcoming AMAs are scheduled for March and April. Administrators are encouraged to follow Windows Events on the Microsoft Tech Community and bookmark the Windows Secure Boot certificate updates page for centralized guidance and resources.
Search