Chrome

Tech Optimizer
September 21, 2026
The landscape of computer security has changed significantly over the past two decades. In 2026, antivirus protection remains important, but the need for separate third-party programs has decreased for many users due to the built-in Microsoft Defender in Windows 11, which is activated by default and effectively blocks 100% of common malware samples according to independent testing by AV-TEST. Windows 11 also includes additional protective features like SmartScreen and a robust Firewall. While dedicated security suites from companies like Norton and Bitdefender offer advanced functionalities, many users may find adequate protection with the built-in tools. Research from AV-Comparatives indicates that performance varies among security programs, particularly against real-world attacks. Phishing attacks accounted for approximately 60% of initial access points in incidents examined by the ENISA Threat Landscape report from 2025, highlighting that user behavior is a significant vulnerability. Modern web browsers and operating systems have enhanced their security measures, with Google Chrome, Microsoft Edge, macOS, and Android incorporating features to protect users from harmful websites and downloads. For the average Windows 11 user who keeps their system updated and practices safe browsing, built-in protection is generally sufficient, though paid antivirus options can provide additional tools.
AppWizard
September 20, 2026
The growing interest in minimalist phones, or "dumbphones," is prompting users to seek ways to transform existing smartphones into more focused devices. Key strategies include managing notifications by turning off alerts for most apps and allowing only essential updates, utilizing app blockers like Switchly to limit distractions from social media, and employing BlockAds to eliminate intrusive ads. Users can also opt for minimalist, ad-free versions of apps, such as the Fossify suite for essential functions and Breezy Weather for weather updates. Customizing the home screen to reduce clutter, such as simplifying it to a single page and disabling unnecessary widgets, can further enhance focus. Additionally, customizing popular apps like Chrome, Gmail, and Google Maps by disabling features and notifications helps create a calmer experience. Overall, intentional choices and the right tools can lead to a more serene smartphone environment.
AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
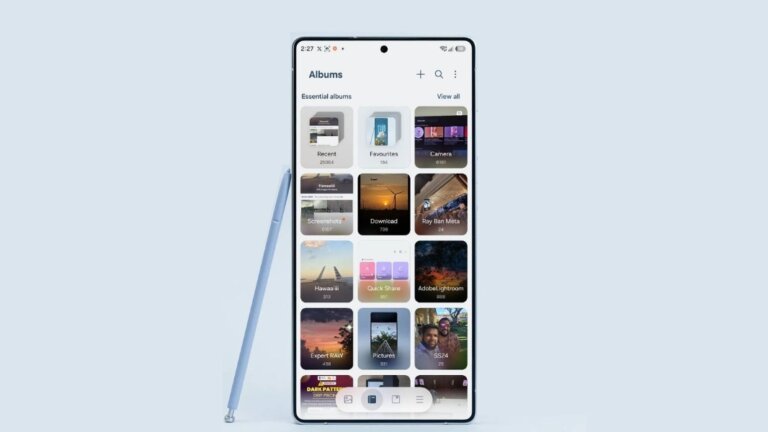
Samsung is replacing the OneDrive integration in its Gallery Android app with Google Photos, following Microsoft's announcement that OneDrive photo backup will cease after September 30, 2026. The new cloud sync feature with Google Photos is being rolled out to select Galaxy users, who must update their Gallery Cloud Sync, Samsung Cloud, and Samsung Gallery apps. The integration does not support supervised personal Google accounts or Google Workspace accounts. Users can back up their camera roll, specific albums, and local device folders to Google Photos, but edited photos will appear as separate items, and some Google Photos features will not be accessible for synced photos. Samsung's Gallery app will continue to operate alongside Google Photos, and the company is developing its own web browser for Android and Windows.
AppWizard
September 17, 2026
In a survey by Android Authority with nearly 1,500 participants, Google Chrome was the most preferred web browser for Android, receiving 32.1% of the votes. Brave followed with 27.2%, while Firefox secured 17.5%. The Samsung Browser came in fourth with 6.4%, Vivaldi at 4.8%, and Microsoft Edge at 4.2%. A Firefox fork received 2.6%, surpassing a lesser-known Chromium-based browser at 2.2%.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
AppWizard
September 12, 2026
Ditching passwords for passkeys has become a more secure option, but these keys are often tied to a single device, posing challenges for cross-platform usage. Google has improved the process for Android users to share and transfer passkeys, allowing easier transitions between password management tools like 1Password and Bitwarden. Previously, transferring passkeys required creating new keys, but now users can move both passwords and passkeys through a secure mechanism within Android. This feature supports popular tools such as 1Password, Bitwarden, Google Password Manager, and Dashlane. Users can transfer passkeys to preferred mobile password managers, facilitating access across multiple devices. The transfer feature is valuable for migrating passkeys between applications, enhancing user experience and security as more individuals adopt passkeys.
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
Search