ClickFix

Tech Optimizer
September 25, 2026
Cybercriminals have developed an infostealer called MacSync, targeting Mac devices by using iCloud calendar events and cloud storage. This malware disguises itself as fake cryptocurrency wallets and pirated software. It begins with a loader that retrieves instructions from calendar entries and deploys malware to exfiltrate sensitive information, including credentials and cryptocurrency wallets. Recent versions have introduced an Objective-C backdoor that mimics Finder. Victims are often tricked into downloading these malicious applications, and effective antivirus solutions can prevent damage. Cybercriminals use tactics like SEO poisoning and phishing to direct victims to fraudulent websites or social media promoting pirated software. In one case, the loader was marketed as a cryptocurrency wallet, and victims encountered a misleading ClickFix error message that prompted them to execute a command in the Terminal.
Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
Winsage
September 4, 2026
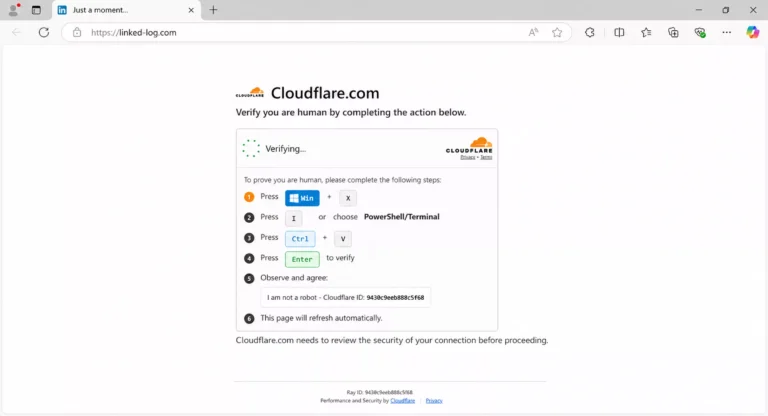
Microsoft has identified a new malware campaign called TerminalFix that uses fake CAPTCHA prompts to trick Windows users into executing malicious commands. This campaign is a variation of ClickFix attacks and employs deceptive pages that impersonate reputable services like Cloudflare. Instead of traditional CAPTCHA challenges, users are instructed to open PowerShell or Command Prompt and paste in commands, allowing attackers to execute complex scripts more easily. TerminalFix initiates a multi-stage intrusion, granting attackers persistent proxy access to the infected machine, which can lead to further exploitation of the company's network. The campaign relies on social engineering tactics, requiring user compliance with counterfeit verification instructions. Microsoft has released mitigation guidance, recommending restrictions on PowerShell access, monitoring for DLL sideloading, blocking outdated Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The campaign poses significant risks to enterprise networks, but individual users should also be cautious about executing commands requested by websites.
Winsage
September 1, 2026
Microsoft Threat Intelligence has identified a new variant of the ClickFix malware campaign called "TerminalFix." This variant uses deceptive CAPTCHAs that mimic trusted services like Cloudflare and directs users to PowerShell or a command prompt, allowing for the execution of complex scripts. TerminalFix aims to orchestrate a multi-stage attack that provides attackers with persistent, network-level proxy access through the compromised host, potentially leading to significant data theft and malware propagation within unsecured enterprise networks. Recommendations for defense against TerminalFix include restricting access to PowerShell and Windows Run dialogs, monitoring for DLL sideloading indicators, blocking Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The attacks primarily target enterprise environments rather than individual consumers.
Winsage
September 1, 2026
Security researchers at Microsoft have identified a campaign named "TerminalFix" that exploits compromised websites to trick users into installing a backdoor. Users visiting these sites encounter a deceptive overlay prompting them to complete a fake Cloudflare CAPTCHA, which requires executing a malicious PowerShell command. This leads victims to inadvertently sideload dynamic link libraries (DLLs) and deploy a Python implant that creates encrypted reverse tunnels, allowing attackers to access internal networks.
Winsage
August 27, 2026
Windows holds a 71 percent share of the desktop market, with over 1.6 billion active Windows PCs globally. In contrast, macOS accounts for just over seven percent of the market, rising to nearly 20 percent when combined with OS X. Windows users face a variety of threats, including trojans and riskware, and in 2025, Windows users encountered seven times more malware than macOS users. Surfshark's data indicates that macOS users are increasingly targeted by phishing attacks, which pose significant financial and personal risks.
Winsage
August 17, 2026
A suspected advanced persistent threat (APT) group linked to China exploited a newly patched vulnerability in VMware vCenter (CVE-2026-59310), which has a critical CVSS score of 9.8, allowing for arbitrary code execution and the deployment of Babuk-derived ransomware. A recently patched vulnerability in Apple macOS (CVE-2026-65400) has been exploited to deploy a cryptocurrency miner, granting unauthorized root access. The Lazarus Group from North Korea exploited a zero-day vulnerability in Microsoft Windows, targeting defense and aerospace sectors. GeoServer patched a critical SQL injection vulnerability that was actively exploited. A new macOS malware, Amnesia Stealer, targets users through ClickFix attacks, stealing data and allowing real-time access to authenticated sessions. A novel attack technique named GhostSplice can manipulate AI coding assistants. Research revealed a method exploiting Chromium's DevTools Protocol for data theft. Noteworthy CVEs this week include CVE-2026-68820, CVE-2026-58231, and multiple others across various platforms. A high-severity command injection flaw in FileRun allows remote code execution. An advanced ClickFix attack has been reported, deploying sophisticated malware. A heap overflow vulnerability in Citrix NetScaler was patched after indications of exploitation. A new malware loader targeting Portuguese-speaking users has been identified. A significant reduction in exposed Automatic Tank Gauge systems has been observed. A phishing campaign targeting Brazil has been detected, and an F.B.I. agent faces charges for unauthorized crypto withdrawals. Authorities in Ukraine dismantled fraudulent call centers, and a North Carolina man was sentenced for cyber extortion. Unauthorized access to sensitive data by the ExfilSquad group has been confirmed. LightSpy activity linked to China has been detected in over 13 countries. A supply chain attack exposed over 2,500 companies, and an Azure exfiltration campaign has exposed millions of enterprise records.
Winsage
August 7, 2026
Microsoft has identified a sophisticated malware campaign that uses the infrastructure of BNB Chain to spread harmful code through compromised websites. The attackers deceive visitors into executing malicious commands disguised as standard security checks, exploiting vulnerabilities in conventional website security measures. This campaign affects both businesses and individual users, utilizing ClickFix lures and EtherHiding techniques. An injected Base64-encoded JavaScript communicates with a BNB Smart Chain RPC gateway to facilitate these malicious operations.
Search