A study by Proton found tracker code associated with companies in China and Russia in many of the most downloaded free Android games in the US and Europe.
The GTA V Android port project has been shut down by parent company Take-Two Interactive with a cease-and-desist letter, ending hopes of a native and optimized version of the game on Android phones. The project aimed to run the game natively on ARM hardware, but relied on leaked source code and violated strict modding policies, leading to its closure on October 3, 2026. The project's source code will not be released publicly to avoid further legal issues. This leaves emulation and cloud streaming as the only options for mobile gamers to play GTA V on their Android phones.
Paralympics Productions attempted to adapt GTA V to run directly on ARM-based hardware for better performance and controls on Android devices. The project ended due to reports that the port used leaked GTA V source code, leading to a cease-and-desist letter from Take-Two. The shutdown does not rule out an official Android version of GTA V in the future.
Traditional antivirus software relies on a signature-based model that compares files against a database of known malware, which limits its effectiveness against modern threats. Cybercriminals have adapted by using polymorphic malware and fileless techniques that evade detection. Endpoint Detection and Response (EDR) continuously monitors device activities, tracking process activity, network connections, and file changes to detect behavioral patterns indicative of attacks. EDR also enables rapid response actions, such as isolating affected devices and terminating malicious processes. Small and medium businesses are increasingly targeted by attackers who exploit the limitations of traditional antivirus solutions. Relying solely on antivirus software creates vulnerabilities, making it essential for organizations to incorporate EDR for enhanced security.
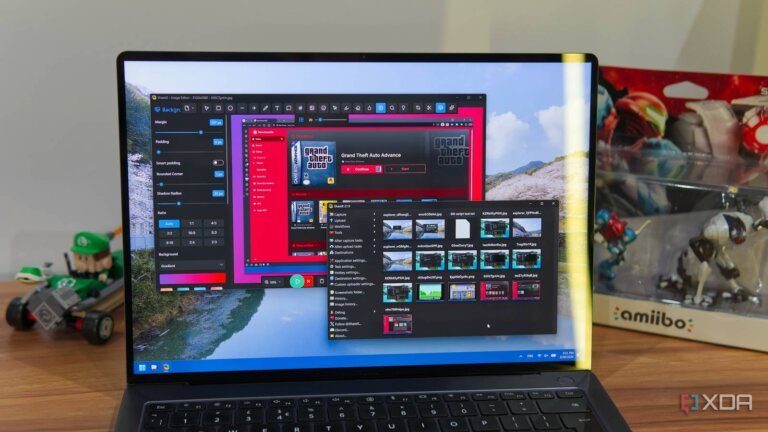
The Snipping Tool in Windows has been modernized in Windows 11 but still has bugs that can disrupt user workflow. ShareX is a free and open-source alternative that excels in screenshot capabilities and offers advanced features, including precise selection tools, real-time editing, video recording, and GIF creation. ShareX supports multiple upload targets, including Imgur and cloud services like OneDrive and Google Drive, and allows users to upload various file types, including text documents to Pastebin. It includes bonus features such as a video converter, image comparison tools, and customization options for hotkeys. However, ShareX may be overwhelming for newcomers seeking basic screenshot functions, for whom the Snipping Tool remains a valid choice.
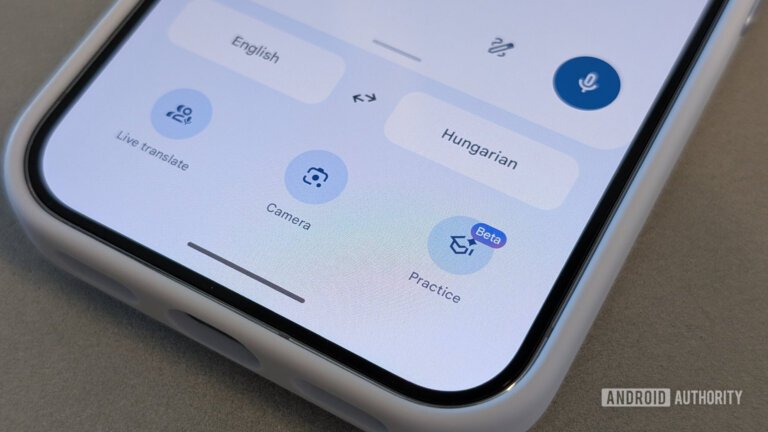
Google Translate is enhancing its Live Translate functionality with a new “Auto-save transcript” feature for mobile users, which will automatically save translation transcripts at the end of each session. However, when using Live Translate through connected smart glasses, transcript saving will be disabled to protect user privacy. The app's code specifies that transcript saving is disabled during glasses use to prevent unauthorized recording. Additionally, users will be able to initiate Live Translate sessions hands-free with voice commands and conclude them with a swipe on the touchpad. Google is also working on simplifying access to Live Translate settings. No timeline for the rollout of these features has been announced.
Organizations that rely on technology face evolving cyber threats that traditional antivirus software struggles to address. Traditional antivirus detects known malware through signature matching but is limited in its ability to catch new or modified threats. Modern cyberattacks utilize techniques like polymorphic malware and fileless attacks to evade detection.
Endpoint Detection and Response (EDR) tools have emerged as a solution, focusing on analyzing behavior rather than matching known threats. EDR continuously monitors endpoints, collects data on system activities, and uses behavioral analysis to identify suspicious actions. This allows for real-time responses to threats, such as isolating affected devices or rolling back changes made by ransomware.
EDR is essential for all organizations, including small businesses, which are often targeted by attackers. It should be part of a broader security strategy that includes traditional antivirus, regular updates, employee training, access controls, and backups. When considering EDR options, businesses should prioritize response speed, visibility, reporting capabilities, and integration with existing IT support.
The GitHub Security Lab has introduced the Taskflow Agent, an open-source tool that uses artificial intelligence to automate the identification of vulnerabilities in Android applications. This tool allows security researchers to create custom taskflow prompts, leading to the discovery of over 20 vulnerabilities. To use the taskflows, a GitHub Copilot license is required, and users can run scripts to audit their projects, with results displayed in an SQLite viewer. Two specific vulnerabilities identified include:
1. OsmAnd app allows malicious applications to track user locations due to improper handling of intent extras in its exported activity.
2. The Wikipedia app has a logic flaw that enables attackers to redirect users to malicious sites via a deeplink mechanism, potentially leading to account takeovers.
The GitHub Security Lab has reported a total of 24 vulnerabilities in Android applications, highlighting the effectiveness of AI in security research.
The author has never played Minecraft and has mixed feelings about dungeon crawlers, finding titles like Diablo IV overly complex. They discovered Minecraft Dungeons 2, which offers a simpler dungeon-crawling experience without the usual complexities of the genre. The game's narrative involves the Illagers opening a portal to a realm called the Sift, where players must reclaim the Overworld. Minecraft Dungeons 2 lacks traditional class systems and deep character customization, instead allowing players to create characters from presets and use a straightforward equipment system. The game features fast travel, clear objectives, and a polished visual style, with responsive combat and a variety of weapons and armor. While it may feel shallow to some veteran players, it is designed for cooperative play and prioritizes accessibility. Minecraft Dungeons 2 is set to release for PS5 on September 29, 2026.
The operators behind RatHat have created an advanced Android banking trojan that allows control of infected devices through a web console. Since April 2026, nearly 100 instances of this console have been identified, indicating a malware-as-a-service model. The console collects sensitive data from compromised phones, including text messages and passwords. It uses Google's Gemini AI to assess victims' bank balances, categorizing them into high-value and mid-value segments, but does not facilitate financial transactions.
The malware has remained largely unchanged since late 2025, but the console has seen significant updates, leading to three new versions: BlackCat Remote Control Management, Panda Workshop V5, and V6. These versions serve as both control interfaces and build tools for creating and distributing malware. The latest version includes templates for deceptive download pages.
RatHat infiltrates devices via text messages and online ads, requesting Accessibility access to read screens and simulate user interactions. This access allows the malware to activate wireless debugging and connect to the Android Debug Bridge (ADB), giving operators elevated privileges to execute commands. A Go program can be deployed to maintain control, even after the app is uninstalled.
Cleafy has tracked console deployments through web code analysis, noting that many IP addresses originate from a Singapore-registered network. The initial console version allowed operators to choose AI providers, but the latest exclusively uses Gemini. RatHat also utilizes Gemini on infected devices to determine tap locations based on screen layouts.
Cleafy has compiled indicators related to the consoles' command-and-control servers, download links, and malware samples, including specific domains, IP addresses, and MD5 hashes. The consoles often use web addresses starting with "admin." and inexpensive top-level domains. Security tools are advised to monitor processes running under the shell user on affected devices.