Command Prompt

Tech Optimizer
September 21, 2026
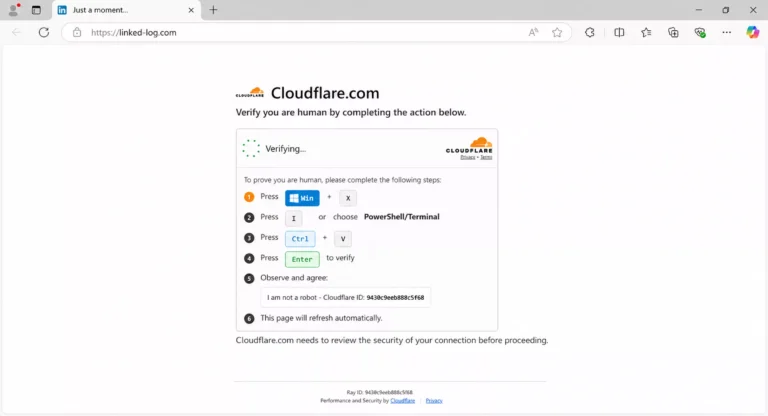
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
Winsage
September 19, 2026
Users are experiencing freezing issues with web applications on PCs due to a bug in Microsoft Edge version 153, which causes windows to become unresponsive to mouse and keyboard inputs. Microsoft has acknowledged the problem and suggested reverting to version 152 as a temporary solution. To downgrade Microsoft Edge, users must disable updates through the Group Policy Editor, download the MSI file for version 152, and execute a rollback command in the Windows command prompt. After completing these steps, users can verify the version of Microsoft Edge to confirm the rollback.
Winsage
September 18, 2026
The Fast Startup feature in Windows, enabled by default, allows the kernel session to remain hibernated during shutdown, which results in quicker boot times by restoring a saved state. In contrast, selecting Restart clears the kernel session entirely, performing a complete boot of Windows. The process of shutting down with Fast Startup involves closing applications, logging off, keeping the kernel loaded in memory, saving the kernel and drivers to hiberfil.sys, and powering off, while Restart closes applications, logs off, ends the kernel session, and reboots immediately without saving a kernel snapshot. Fast Startup can lead to persistent issues from previous sessions, making Restart a better option for troubleshooting. To perform a full shutdown bypassing Fast Startup, users can execute the command "shutdown /s /t 0." Microsoft advises against permanently disabling Fast Startup, as it enhances shutdown-to-boot transitions.
Winsage
September 4, 2026
Microsoft has identified a new malware campaign called TerminalFix that uses fake CAPTCHA prompts to trick Windows users into executing malicious commands. This campaign is a variation of ClickFix attacks and employs deceptive pages that impersonate reputable services like Cloudflare. Instead of traditional CAPTCHA challenges, users are instructed to open PowerShell or Command Prompt and paste in commands, allowing attackers to execute complex scripts more easily. TerminalFix initiates a multi-stage intrusion, granting attackers persistent proxy access to the infected machine, which can lead to further exploitation of the company's network. The campaign relies on social engineering tactics, requiring user compliance with counterfeit verification instructions. Microsoft has released mitigation guidance, recommending restrictions on PowerShell access, monitoring for DLL sideloading, blocking outdated Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The campaign poses significant risks to enterprise networks, but individual users should also be cautious about executing commands requested by websites.
Winsage
September 1, 2026
Microsoft Threat Intelligence has identified a new variant of the ClickFix malware campaign called "TerminalFix." This variant uses deceptive CAPTCHAs that mimic trusted services like Cloudflare and directs users to PowerShell or a command prompt, allowing for the execution of complex scripts. TerminalFix aims to orchestrate a multi-stage attack that provides attackers with persistent, network-level proxy access through the compromised host, potentially leading to significant data theft and malware propagation within unsecured enterprise networks. Recommendations for defense against TerminalFix include restricting access to PowerShell and Windows Run dialogs, monitoring for DLL sideloading indicators, blocking Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The attacks primarily target enterprise environments rather than individual consumers.
Search