command

Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
AppWizard
September 20, 2026
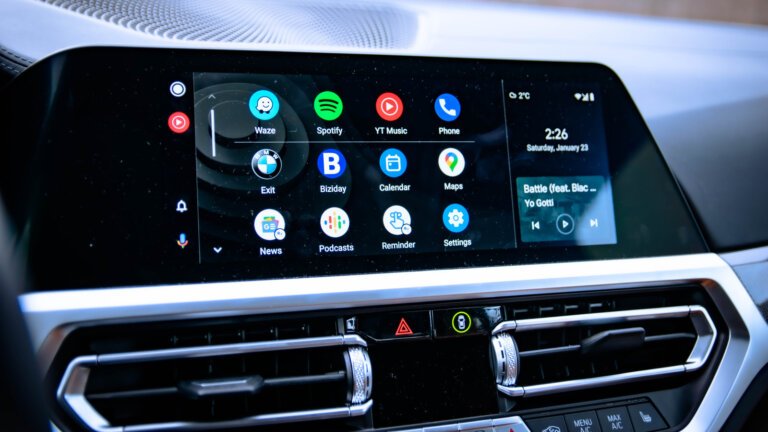
Gemini integration in Android Auto enhances hands-free functionality, allowing drivers to use natural voice commands for navigation, music, and phone features without touching their devices. Users can activate voice commands by saying "Hey Google" or using a dedicated steering wheel button, depending on the vehicle model. Navigation can be managed entirely through voice, enabling users to request routes, add stops, and report issues without screen interaction. Android Auto also supports hands-free control for calls and messages, allowing users to answer and respond without taking their hands off the wheel. Automations can be set up to start Android Auto and media playback automatically when the phone connects to the vehicle, streamlining the driving experience.
Tech Optimizer
September 19, 2026
For nearly two months, Windows 11 users received persistent notifications from the Windows Security app falsely indicating that Microsoft Defender was disabled, despite it functioning properly. This issue, which began in early August, has been addressed with a security update from Microsoft. The false alerts affected all versions of Windows 11, Windows Server, and Windows 10, and were linked to a bug introduced with a recent Defender security update. Microsoft confirmed that no manual action is required from users to resolve the issue, as the fix will be automatically deployed to all PCs with mandatory security updates enabled. The problem was resolved in the Microsoft Defender Antivirus update (version 4.18.26080.4), released on September 17, 2026. Users can verify the status of Defender by checking Windows Security or using a PowerShell command.
Winsage
September 19, 2026
Users are experiencing freezing issues with web applications on PCs due to a bug in Microsoft Edge version 153, which causes windows to become unresponsive to mouse and keyboard inputs. Microsoft has acknowledged the problem and suggested reverting to version 152 as a temporary solution. To downgrade Microsoft Edge, users must disable updates through the Group Policy Editor, download the MSI file for version 152, and execute a rollback command in the Windows command prompt. After completing these steps, users can verify the version of Microsoft Edge to confirm the rollback.
Winsage
September 18, 2026
The initial storage cost of the search index on a fresh installation of Windows 11 is minimal, only a few megabytes. When a sizable work folder is added, the index expands, but it does not revert to its original size after the folder is removed. The search index is stored in Windows.db for Windows 11 and Windows.edb for Windows 10. Windows 11 has two indexing modes: Classic (default) and Enhanced, with Classic indexing Documents, Pictures, Music folders, and the Desktop, while Enhanced scans the entire PC. The index includes file names and content, allowing keyword searches. Users can measure their index items through Settings without special permissions, while file size requires administrative access via PowerShell. An index under 30,000 items is acceptable for average users, while performance issues may arise beyond 400,000 items, with a technical ceiling of one million items. In an experiment, the index grew from 462 items and 6.71 MB to 3,466 items and 18.66 MB after adding 3,000 text files, but remained at 16.81 MB after deleting those files. To reclaim disk space, users can exclude specific folders from indexing and rebuild the index, which can significantly reduce its size while retaining the same number of items.
Winsage
September 18, 2026
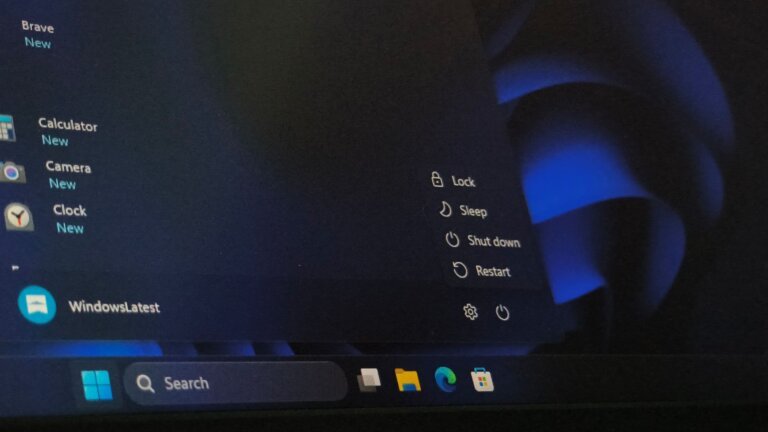
The Fast Startup feature in Windows, enabled by default, allows the kernel session to remain hibernated during shutdown, which results in quicker boot times by restoring a saved state. In contrast, selecting Restart clears the kernel session entirely, performing a complete boot of Windows. The process of shutting down with Fast Startup involves closing applications, logging off, keeping the kernel loaded in memory, saving the kernel and drivers to hiberfil.sys, and powering off, while Restart closes applications, logs off, ends the kernel session, and reboots immediately without saving a kernel snapshot. Fast Startup can lead to persistent issues from previous sessions, making Restart a better option for troubleshooting. To perform a full shutdown bypassing Fast Startup, users can execute the command "shutdown /s /t 0." Microsoft advises against permanently disabling Fast Startup, as it enhances shutdown-to-boot transitions.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Search