commerce

AppWizard
October 15, 2026
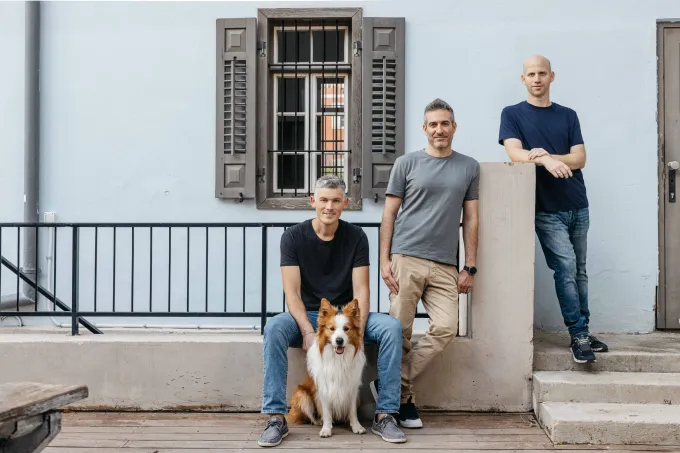
Businesses are increasingly using consumer-facing chat applications for staff communication and document sharing. Zenzap is a new private messaging platform led by Guy Weiss, designed for organizational context and compliance, featuring AI capabilities. The startup has secured funding from investors such as Bessemer, Lightspeed, and individual backers, marking Weiss's first fundraising effort after previously bootstrapping an e-commerce platform. Zenzap, founded in 2022, aims to serve various industries, offering features such as group chats, task management, calendar integration, and AI-powered tools on both free and paid plans. It currently counts clients like FedEx, Taco Bell, and Starbucks, and has a team of 50 employees across multiple locations. Zenzap's versatility is emphasized, as it targets a broader audience beyond developers, focusing on the majority of employees using personal messaging applications.
AppWizard
September 16, 2026
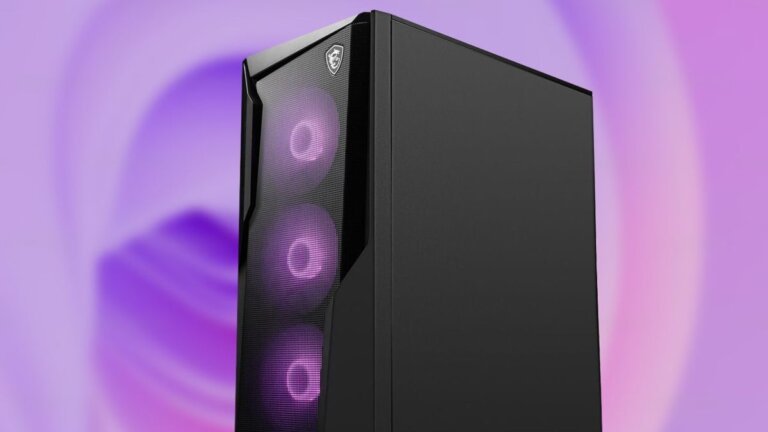
B&H Photo is offering a limited-time deal on the MSI Codex Z2C RTX 5070 gaming PC for ,399 with free shipping. Buyers will receive a download voucher for the game Control: Resonant, releasing on September 22. The PC features an AMD Ryzen 7 8700F CPU, GeForce RTX 5070 12GB GPU, 16GB of DDR5 RAM, and a 1TB M.2 SSD. The Ryzen 7 8700F has an 8-core, 16-thread architecture with a boost clock speed of 5.1GHz. The GeForce RTX 5070 is designed for 1080p and 1440p gaming, typically retailing around 0. It can run most titles at 4K, but upgrading to a 5070 Ti may provide better performance at that resolution.
AppWizard
September 16, 2026
The Humble Isometric Immersion CRPG Pack includes 11 games, featuring titles like Disco Elysium: The Final Cut and Warhammer 40,000: Rogue Trader. The retail value of the games is significantly higher than the sale price. Disco Elysium: The Final Cut received a perfect score of 10/10, while Warhammer 40,000: Rogue Trader and Pathfinder: Wrath of the Righteous scored 8, and Torment: Tides of Numenera scored 8.8. The bundle expires in 7 days.
Tech Optimizer
September 14, 2026
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
AppWizard
September 14, 2026
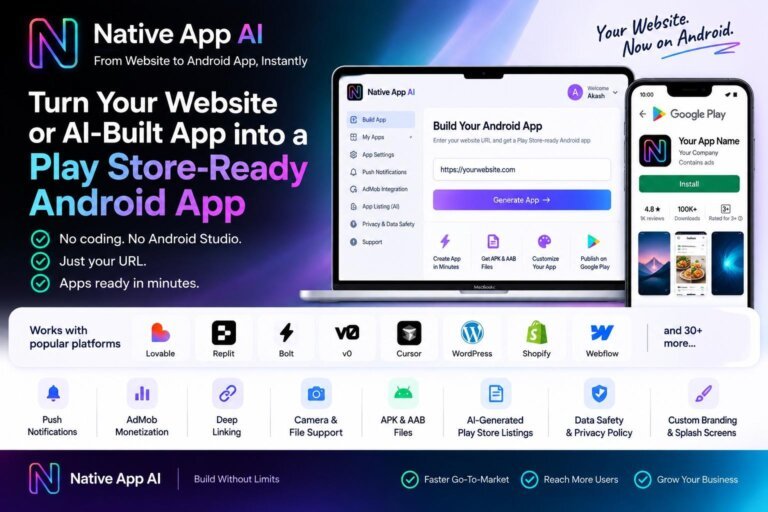
Native App AI simplifies the process of converting websites or AI-generated web apps into Android applications ready for the Play Store without needing to rebuild from scratch. It allows users to input a website URL, customize the app's features, and generate APK and AAB files for testing and publishing. The platform supports various features such as push notifications, AdMob monetization, deep linking, and custom branding. It also assists in preparing necessary information for Google Play, ensuring compliance with policies and technical requirements. This service is beneficial for SaaS companies, startups, e-commerce ventures, and creators who have existing web products.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
Winsage
September 10, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has expanded its Known Exploited Vulnerabilities (KEV) catalog, adding critical vulnerabilities that need immediate attention. 1. CVE-2026-75650: A vulnerability in Adobe Commerce and Magento with a CVSS score of 10.0, allowing unauthenticated remote code execution. Affected versions include Magento Open Source releases 2.4.7, 2.4.8, and 2.4.9. It has been actively exploited since September 4. 2. CVE-2026-81963: A Microsoft Windows vulnerability with a CVSS score of 7.8, related to a link-following issue within the Update Stack, allowing local attackers to escalate privileges. It is currently being exploited. 3. CVE-2026-85880: Another Microsoft Windows vulnerability rated at 7.8, involving a heap-based buffer overflow in the ALPC component, permitting local privilege escalation. This flaw is also actively exploited. 4. CVE-2026-86218: A N-able N-central vulnerability with a CVSS score of 10.0, allowing pre-authenticated remote code execution. N-able has released an emergency hotfix for this issue. Federal agencies must address these vulnerabilities by specified deadlines: Windows flaws by September 22 and other vulnerabilities by September 11, 2026, in accordance with Binding Operational Directive (BOD) 22-01. Private organizations are advised to review the KEV catalog and take necessary actions to strengthen their infrastructure against these vulnerabilities.
Search