Researchers have found that Max, a messaging app mandated by the Russian government, can secretly capture screenshots, access sensitive information, impersonate users, and inject code into other applications. Developed by VK, the app integrates messaging, banking, and government services. Since September 1 of last year, it has been preinstalled on new smartphones, following the blocking of WhatsApp and Telegram. Despite its reach, it is not widely used in political circles, with insiders indicating that compliance with its use is performative.
Google's September 2026 Pixel Update Bulletin includes patches that affect standard Android platform code, relevant to both Pixel and non-Pixel devices, which have not been included in the regular monthly Android Security Bulletin. GrapheneOS has noted that Android 17 QPR1 introduced new developer APIs not present in the Android Open Source Project (AOSP) for the first time since Android Honeycomb, with one new package and modifications to sixteen others. GrapheneOS is backporting Pixel firmware and drivers from QPR1 onto Android 17 but lacks permissions to distribute this work. Additionally, there has been a delay in Google’s compliance with a GPL source request, with access granted over two weeks after the initial request. Starting in 2027, Google will require all Android app developers to register with them and provide legal identification and signing key evidence, complicating the process of sideloading unverified apps. GrapheneOS and other organizations are advocating for the Keep Android Open campaign against these developments, which may restrict competition and tighten Google's control over the Android ecosystem.
Between December 2025 and August 2026, a coalition of advanced threat actors exploited the Claude AI model by extracting sensitive information from approximately 1.8 million Android applications. The operation involved groups such as ShinyHunters, Midnight Blizzard (APT29/Nobelium), and the Chinese-speaking entity GTG-10007. They automated the mass download, decompilation, and analysis of Android APKs for hardcoded credentials, API keys, and authentication tokens, leading to extensive credential theft and breaches across various sectors.
The attack utilized a distributed pipeline on ten AWS EC2 instances to download APKs, which were then scanned using TruffleHog. Verified secrets were organized and routed in real-time to a private Telegram group for operational deployment. Over 2,100 Azure AD authentication tokens were extracted from more than 40 Microsoft tenants within 34 hours. The operation also included a carding component where stolen payment card data was sold.
The tactics employed aligned with several MITRE ATT&CK techniques, including file discovery, unsecured credentials, valid accounts, phishing, and exploitation of remote services. ShinyHunters gained administrative control over targeted environments rapidly, leading to bulk data theft affecting over 200 organizations. Midnight Blizzard automated malware creation and phishing campaigns, targeting government and defense entities. GTG-10007 used Claude for coordinated offensive operations, discovering zero-day vulnerabilities and delivering exploits.
Initially, the campaign targeted a broad range of Android APKs but later focused on organizations with valuable credentials across various sectors, including government, technology, and healthcare. Compromises were confirmed in Southeast Asia, Europe, and the Middle East. Organizations are advised to audit Android applications for hardcoded secrets, monitor API key usage, and implement robust security practices to mitigate risks.
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
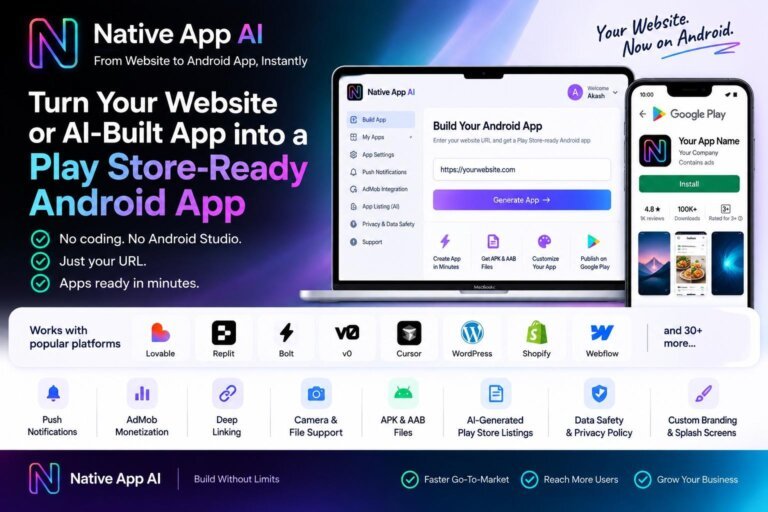
Native App AI simplifies the process of converting websites or AI-generated web apps into Android applications ready for the Play Store without needing to rebuild from scratch. It allows users to input a website URL, customize the app's features, and generate APK and AAB files for testing and publishing. The platform supports various features such as push notifications, AdMob monetization, deep linking, and custom branding. It also assists in preparing necessary information for Google Play, ensuring compliance with policies and technical requirements. This service is beneficial for SaaS companies, startups, e-commerce ventures, and creators who have existing web products.
The Google Maps speedometer has disappeared for many Android Auto users due to a cache conflict, resulting in the speed overlay vanishing from screens. This issue is linked to internal desynchronization between the mobile app and the car's infotainment system, causing crashes for users. The problem is not due to changes on Google’s servers but rather the accumulation of temporary data that prevents crucial elements from loading correctly. Reports indicate that this issue affects users across various Android versions, including Android 14. A temporary solution involves performing a clean reset of the Google Maps and Android Auto apps by clearing their cache and data. If the problem persists, users may need to check for updates or wait for a fix from Google. Additionally, maintaining updated location permissions and the car’s system is recommended. Waze is suggested as an alternative for speed accuracy during this issue.
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption.
Various management models are available for different environments, including:
1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management.
2. Sophos: Manages both BitLocker and FileVault from a single console.
3. ESET: Offers lightweight management and removable-media protection.
4. Trend Micro: Integrates encryption with DLP capabilities.
5. Check Point: Provides advanced pre-boot options and policy management.
6. Trellix: Comprehensive enterprise encryption suite with a complex management interface.
7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options.
8. Broadcom (Symantec): Manages native engines within its broader security framework.
9. Dell: OEM-integrated encryption management for Dell hardware.
10. Kaspersky: Provides encryption management but is restricted in the U.S.
Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
Microsoft BitLocker and Apple FileVault are free, integrated encryption solutions within their respective operating systems. As of 2026, the focus is on investing in management solutions that provide compliance proof, key escrow, recovery options, and policy enforcement across devices. Native encryption solutions lack certain management features, prompting the need for additional management layers from various vendors.
Legacy freeware like TrueCrypt is no longer maintained, posing risks for business use, while VeraCrypt is a credible open-source alternative but lacks centralized management. Management options include Microsoft Intune for Windows, Sophos for mixed fleets, and specialized providers like Check Point and WinMagic for advanced needs.
Organizations should ensure proper key management before enforcing encryption to avoid data loss and regularly test recovery processes. It is crucial to verify claims regarding compatibility and pre-boot options when selecting encryption solutions. Native engines are free, but management layers typically charge per endpoint annually.
Comma Compliance released the source code for its Android capture component on September 10, 2026, allowing corporate IT and security teams to inspect the software that captures employee text messages for compliance archiving. The source code is available on GitHub under the MIT license. The capture mechanism reads messages stored in the phone's default messaging app, encrypts them, and sends them to the customer's Comma backend without intercepting messages in transit. A persistent notification appears on the phone when archiving is active, indicating the organization responsible for the archiving. Comma previously open-sourced its WhatsApp and Signal capture connectors in 2025.
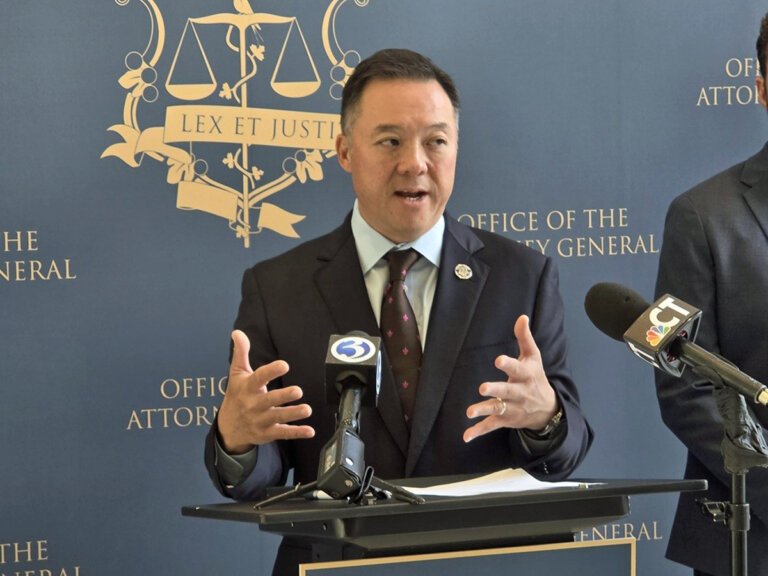
Attorney General William Tong has launched an investigation into MediaLab.AI Inc., the parent company of Kik, due to concerns about the app's child safety practices. Kik is described as having inadequate age verification and content screening, with about one-third of American teenagers using it, and 70% of users aged 13 to 24. The National Center on Sexual Exploitation identified Kik as a leading app for exposing children to sexual content and included it in their “Dirty Dozen” list. Between 2014 and 2020, over 2,000 federal cases involved Kik. MediaLab has attempted to improve safety by reclassifying the app to an 18+ rating and activating explicit content filters, but these efforts have been deemed insufficient. The investigation will also assess Kik's compliance with the Connecticut Data Privacy Act, focusing on the handling of sensitive data without consent.