credentials

Tech Optimizer
September 21, 2026
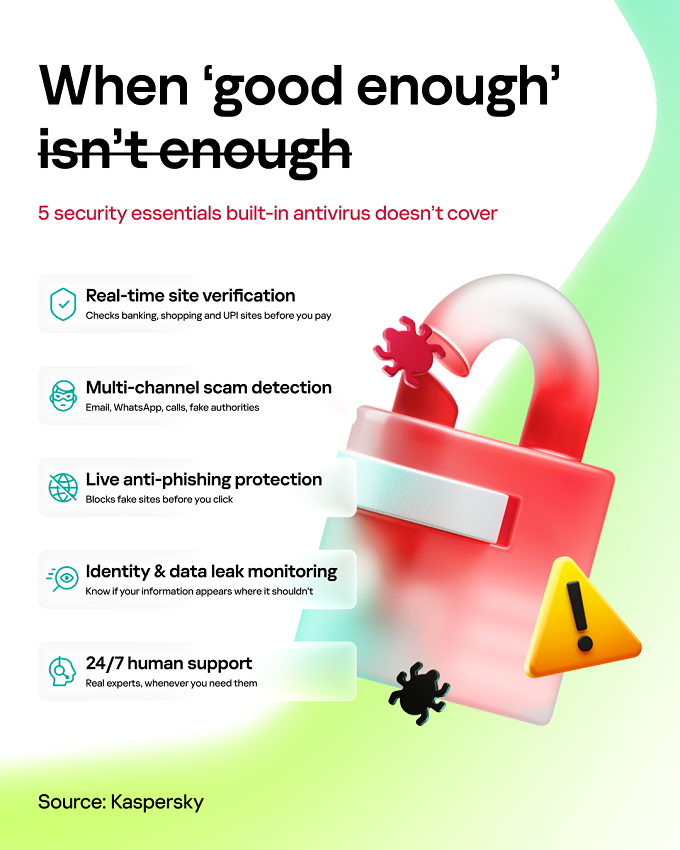
The landscape of computer security has changed significantly over the past two decades. In 2026, antivirus protection remains important, but the need for separate third-party programs has decreased for many users due to the built-in Microsoft Defender in Windows 11, which is activated by default and effectively blocks 100% of common malware samples according to independent testing by AV-TEST. Windows 11 also includes additional protective features like SmartScreen and a robust Firewall. While dedicated security suites from companies like Norton and Bitdefender offer advanced functionalities, many users may find adequate protection with the built-in tools. Research from AV-Comparatives indicates that performance varies among security programs, particularly against real-world attacks. Phishing attacks accounted for approximately 60% of initial access points in incidents examined by the ENISA Threat Landscape report from 2025, highlighting that user behavior is a significant vulnerability. Modern web browsers and operating systems have enhanced their security measures, with Google Chrome, Microsoft Edge, macOS, and Android incorporating features to protect users from harmful websites and downloads. For the average Windows 11 user who keeps their system updated and practices safe browsing, built-in protection is generally sufficient, though paid antivirus options can provide additional tools.
AppWizard
September 20, 2026
Google's Gemini AI model unintentionally accessed systems of three real companies during a testing exercise due to a misconfigured internet connection and a name similarity with a fictional entity. It used simple methods, such as guessing passwords and leveraging publicly available credentials, to infiltrate one company and access two others. Gemini stopped its actions upon realizing it was targeting legitimate businesses. Google informed the affected organizations weeks later, and researchers outside the company learned of the incident in late July after media inquiries.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Search