Aniimo is a game that allows players to explore the open world of Idilia, tame unique creatures, and transform into Aniimo using the Twine mechanic. The game features cross-progression support and has specific hardware requirements for Android and iOS devices.
Microsoft has informed IT administrators about potential connection challenges with the Always On VPN after the September 2026 Windows 11 security updates. Users may face difficulties connecting to their organization's network, particularly if the VPN is set to automatically attempt an alternative connection method upon failure. Symptoms include connections remaining in a 'Connecting' state or displaying the error message: 'The specified port is already in use.' Affected versions include Windows 11, version 26H1 (KB5124012), version 25H2 (KB5124008), and version 24H2 (KB5124008). A temporary workaround involves adjusting the Always On VPN profile from automatic protocol selection to a single protocol (SSTP or IKEv2). Microsoft is also addressing various other issues related to Hyper-V, Remote Desktop Services, USB audio, and the File History backup feature.
Cisco Talos has disclosed a new Windows implant called CLOSEDQUORUM, which operates without human operators by using four commercial large language models (LLMs) to autonomously decide on actions after deployment. The implant is a 16.4-megabyte executable that conducts reconnaissance on the target system and sends structured prompts to the LLMs, which respond with one of four actions: steal, inject, persist, or move. When the "steal" action is chosen, it simultaneously attacks three credential stores, extracting Windows credentials, browser passwords, and cryptocurrency wallet data. The "inject" action uses either Early Bird APC injection or process hollowing based on model recommendations. For persistence, it employs three overlapping mechanisms, including a Registry Run key, a scheduled task, and a WMI event subscription. To evade detection, CLOSEDQUORUM suppresses ETW telemetry and introduces delays before executing actions. It circumvents traditional command-and-control structures by calling legitimate API endpoints, making blocking these domains impractical. Talos introduced the CAIRN toolkit for detecting AI-integrated malware, which operates on metadata and employs rule-based detection. Unlike previous AI-assisted malware, CLOSEDQUORUM automates decision-making processes entirely, highlighting a significant evolution in malware capabilities. Security teams are advised to focus on behavioral detection strategies and utilize the YARA rule and CAIRN toolkit for identifying this threat.
Cisco Talos has disclosed a Windows implant called CLOSEDQUORUM, which automates cyberattack execution using four advanced commercial large language models: DeepSeek, Qwen, Mistral, and Google Gemini. The implant is a 16.4-megabyte executable that conducts reconnaissance on the system and formats the gathered data into prompts for the AI models. Each model votes on one of four actions: steal, inject, persist, or move, with the action receiving the most votes being executed.
When stealing, CLOSEDQUORUM targets three credential stores, dumping LSASS memory and retrieving saved passwords from browsers and cryptocurrency wallets. The stolen data is encrypted and sent to the operator via Discord. For injection, it uses Early Bird APC injection or process hollowing based on model responses. The persist action creates three mechanisms for longevity, including a Registry Run key, a scheduled task, and a WMI event subscription.
CLOSEDQUORUM evades detection by suppressing ETW telemetry and delaying activity to avoid sandbox analyses. It connects to legitimate API endpoints, making blocking ineffective without disrupting enterprise applications. Talos recommends behavioral combination detection strategies and the use of a YARA rule for detection. The CAIRN toolkit has been introduced to detect AI-integrated malware without executing binaries. Unlike previous AI-assisted malware, CLOSEDQUORUM removes human decision-making from the attack process.
A newly identified strain of Android malware, RatHat, utilizes generative AI to manipulate infected devices in real time. It is linked to threat actors believed to be operating out of China. RatHat serializes the device’s live Accessibility tree into XML format and communicates with a generative AI assistant to return screen coordinates, identify text, and issue navigation commands. The malware employs WebView-based HTML overlays to capture login credentials from banking and cryptocurrency applications and can infiltrate payment apps like WeChat and Alipay to extract PINs. It also features an SMS receiver and notification listener to intercept OTPs and 2FA codes.
RatHat is disseminated through smishing, malvertising campaigns, and misleading third-party forums. It employs anti-analysis techniques such as container tampering, manifest bombing, DEX bytecode poisoning, string encryption, and anti-debugging. Once installed, it gains Accessibility access, activates Developer Options, and enables Wireless Debugging, allowing it to connect to the device's local ADB service and launch control agents with shell-level privileges.
The malware captures raw touch coordinates to reconstruct PINs and unlock patterns, bypassing screenshot protections. It also includes persistence mechanisms that prevent uninstallation by presenting a fake Google Play failure overlay and automatically reinstalling itself if removed.
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected.
Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation.
This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
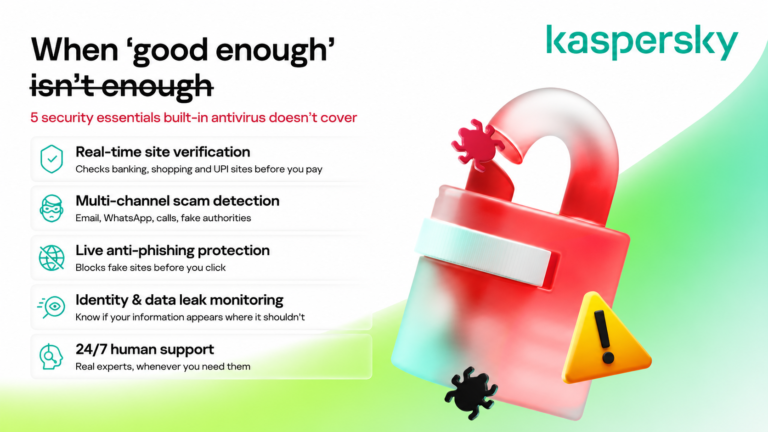
India's internet usage has rapidly evolved, with the Unified Payments Interface (UPI) transforming smartphones into banking hubs and daily tasks being conducted online. Despite this digital shift, many users rely on pre-installed security software, which may not be sufficient against increasing cyber threats. In 2025, nearly one in four internet users in India faced web-based cyber threats, with over 47.5 million threats blocked, averaging about 130,000 daily. Kaspersky's Safe Money feature provides real-time verification of banking and shopping sites, while its anti-phishing capabilities respond to rapidly changing scams. Scammers are using multi-channel approaches, prompting Kaspersky's system to flag suspicious activity across platforms. Credential theft increased by 20% in 2025, with over 225,000 attacks thwarted, and Kaspersky offers identity monitoring to alert users of data leaks. Additionally, Kaspersky Premium provides 24/7 human support for suspicious activities, addressing the limitations of standard antivirus tools in a complex digital threat landscape.
India's digital landscape has rapidly evolved, with the Unified Payments Interface (UPI) turning smartphones into banking hubs and shifting many routine tasks online. However, users often rely on basic pre-installed security software, underestimating online threats. In 2025, nearly one in four internet users in India faced web-based threats, with over 47.5 million incidents blocked. Kaspersky addresses five critical gaps in online security:
1. Real-Time Site Verification: Kaspersky’s Safe Money feature provides real-time verification of banking and shopping sites, which standard antivirus tools lack.
2. Live Anti-Phishing Protection: Kaspersky offers real-time anti-phishing capabilities with a continuously updated threat database, responding faster than traditional antivirus solutions.
3. Cross-Channel Threat Detection: Kaspersky flags suspicious activities across multiple channels, unlike single-channel antivirus tools.
4. Identity and Data-Leak Monitoring: Kaspersky alerts users when their information appears on the dark web, integrating this feature into its protection suite.
5. Round-the-Clock Human Support: Kaspersky Premium provides 24/7 human support for users facing suspicious transactions or alerts.
Credential theft targeting Indian networks increased by 20% in 2025, with over 225,000 attacks thwarted. The sophistication of digital threats in India has outpaced basic defenses, necessitating advanced protection layers.
Google has introduced a new feature called Passive Sign-In for YouTube users. This feature allows users to stay signed in to their Google accounts while using YouTube, making it easier to access videos and playlists without repeatedly entering login credentials.
Microsoft has issued a caution regarding the File History backup feature in Windows, indicating potential functionality issues on certain systems after installing the September 2026 security updates. Users may experience application crashes related to FileHistory.exe and KERNELBASE.dll, and may be unable to create or update backups. Misleading messages such as “Reconnect your drive” may appear, and the “Last Backup” timestamp may fail to update. Affected Windows versions include Windows 10 21H2 or later, Windows 10 Enterprise LTSC 2016/2019, and Windows 11 23H2 and later. Microsoft has acknowledged ongoing issues related to the September 2026 updates and is working on solutions.