- Wild Tokyo, Rolling Slots, Mino Casino, and Boho Casino are the best mobile casinos in Australia based on mobile performance, gameplay experience, payment efficiency, and overall usability.
India's internet usage has rapidly evolved, with the Unified Payments Interface (UPI) transforming smartphones into banking hubs and daily tasks being conducted online. Despite this digital shift, many users rely on pre-installed security software, which may not be sufficient against increasing cyber threats. In 2025, nearly one in four internet users in India faced web-based cyber threats, with over 47.5 million threats blocked, averaging about 130,000 daily. Kaspersky's Safe Money feature provides real-time verification of banking and shopping sites, while its anti-phishing capabilities respond to rapidly changing scams. Scammers are using multi-channel approaches, prompting Kaspersky's system to flag suspicious activity across platforms. Credential theft increased by 20% in 2025, with over 225,000 attacks thwarted, and Kaspersky offers identity monitoring to alert users of data leaks. Additionally, Kaspersky Premium provides 24/7 human support for suspicious activities, addressing the limitations of standard antivirus tools in a complex digital threat landscape.
India's digital landscape has rapidly evolved, with the Unified Payments Interface (UPI) turning smartphones into banking hubs and shifting many routine tasks online. However, users often rely on basic pre-installed security software, underestimating online threats. In 2025, nearly one in four internet users in India faced web-based threats, with over 47.5 million incidents blocked. Kaspersky addresses five critical gaps in online security:
1. Real-Time Site Verification: Kaspersky’s Safe Money feature provides real-time verification of banking and shopping sites, which standard antivirus tools lack.
2. Live Anti-Phishing Protection: Kaspersky offers real-time anti-phishing capabilities with a continuously updated threat database, responding faster than traditional antivirus solutions.
3. Cross-Channel Threat Detection: Kaspersky flags suspicious activities across multiple channels, unlike single-channel antivirus tools.
4. Identity and Data-Leak Monitoring: Kaspersky alerts users when their information appears on the dark web, integrating this feature into its protection suite.
5. Round-the-Clock Human Support: Kaspersky Premium provides 24/7 human support for users facing suspicious transactions or alerts.
Credential theft targeting Indian networks increased by 20% in 2025, with over 225,000 attacks thwarted. The sophistication of digital threats in India has outpaced basic defenses, necessitating advanced protection layers.
A young Minecraft enthusiast, known as MightyMikePLays67, accidentally charged ,000 to his father's company credit card while promoting his YouTube channel. The father, Dave, has lost his job and must settle the bill within 30 days. Despite the situation, he remains optimistic and is considering selling their home to cover the expense. Dave and his son shared a light-hearted moment about the incident, and he has launched a merchandise website featuring designs inspired by Mighty Mike's adventures. Dave has not sought external assistance or fundraising options, and he provided a screenshot of the credit card bill showing a charge of ,479.83. He is determined to handle the situation independently, expressing uncertainty about sharing his story with news outlets.
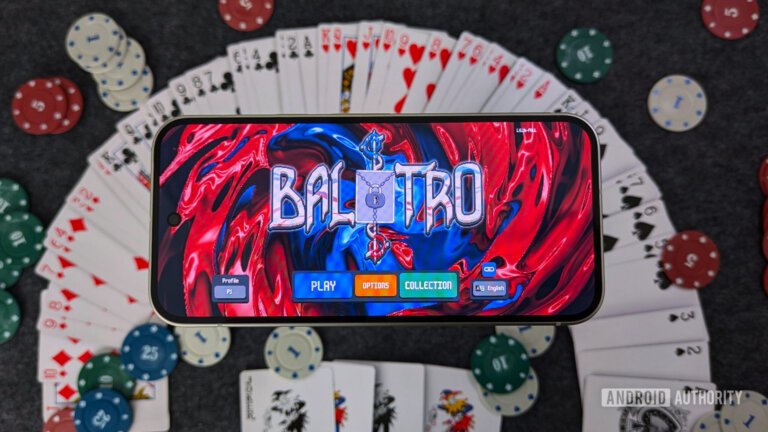
A user has trained a fruit fly brain to play the Android game Balatro, using a custom seed-finding algorithm to achieve a 20% win rate on the easiest setting.
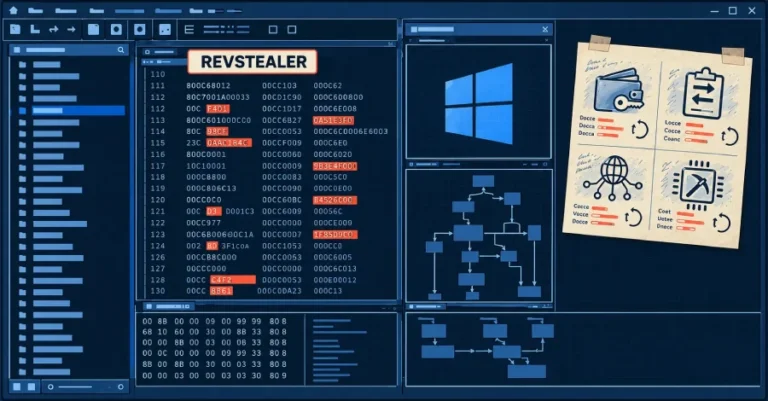
Elastic Security Labs has identified four previously undocumented programs associated with REVSTEALER, a Windows information stealer that persists on infected machines after self-deletion. The programs are ProManager, WinUpdate, SoftManager, and LockAppHost, each with distinct functionalities. ProManager steals wallet files and logs passwords, WinUpdate monitors the clipboard for cryptocurrency addresses, SoftManager acts as a reverse proxy, and LockAppHost executes a cryptocurrency miner after disabling Windows Update and Microsoft Defender.
REVSTEALER has been marketed as a commercial infostealer since February 2026, exfiltrating sensitive data such as browser passwords, cookies, and cryptocurrency wallet information. It deletes itself after reporting its activities but leaves the four programs installed for persistence. These programs share build tradecraft with REVSTEALER, including the use of identical packers and runtime function resolutions.
REVSTEALER primarily spreads through game-cheat lures and disguises itself as pirated software. It employs evasion techniques to resist analysis, including checking for sandbox environments and using indirect system calls. Users are advised to avoid unofficial software and to follow specific steps if infected, such as re-enabling Windows Update services and changing passwords.
Indicators of compromise include SHA-256 hashes for REVSTEALER and its associated programs, as well as domains linked to their command and control servers.
Ransomware protection is best approached as a layered strategy rather than relying on a single solution. The effectiveness of software is significantly enhanced by maintaining a well-managed backup that is disconnected during an attack. Five tools were evaluated based on their default settings, focusing on behavioral detection, protected folders, file rollback, and real-time protection.
1. Norton 360: Rated as the best overall ransomware protection, it offers comprehensive features including behavioral monitoring, protected folders with dual alert modes, and 50 GB of cloud backup within a single subscription. It has a perfect score in advanced threat assessments.
2. Bitdefender: Recognized for its file rollback and remediation capabilities, it provides an effective "undo" feature that restores files, although this feature is turned off by default.
3. Avast One Free: The best free ransomware protection option, it includes a dedicated shield on the free Windows tier and has achieved a perfect score in advanced threat assessments.
4. NordVPN Threat Protection Pro: Best for blocking the delivery route of ransomware, it prevents downloads before encryption starts but cannot stop the process once it has begun.
5. McAfee: Best for protecting multiple devices simultaneously, it offers unlimited device coverage on most plans with integrated ransomware defense in its scanning engine.
Modern ransomware protection software has shifted from signature matching to focusing on monitoring the behavior of processes interacting with files. The four essential layers of protection include behavioral monitoring, protected folders, automatic file rollback, and backup. Most users do not need a separate anti-ransomware product, as these features are typically included in main antivirus suites, with the key consideration being whether these features are activated.
The rankings of the tools were based on whether the ransomware protection layer is enabled by default, the extent of file recovery when intervention occurs, and the frequency of false positives during normal use.
- Norton 360: Best overall, with protection enabled by default and a perfect score in advanced threat testing.
- Bitdefender: Best for file rollback, but the rollback feature is disabled by default.
- Avast One Free: Best free option, with a perfect score in advanced threat assessments but lacks rollback capabilities.
- NordVPN Threat Protection Pro: Effective at blocking malware downloads but does not provide rollback or backup features.
- McAfee: Suitable for families with multiple devices, offering automatic backup of flagged files but lacks user-configurable protected folder options.
The effectiveness of ransomware protection tools is primarily assessed through behavioral responses rather than library matching. Backup remains a critical layer of defense, functioning even when other layers fail.
On August 18, an entity named "Cyberleek" shared what is believed to be authentic gameplay footage from Grand Theft Auto 6, featuring the protagonist Jason. The footage showcased typical GTA activities and was removed from social media due to copyright claims from Take-Two and Rockstar. Cyberleek's leaks were not from testers but indicated access to a segment of GTA 6. They expressed consumer rights grievances and made three demands: no more digital preorders, no selling DLC already included in base game files, and mandatory offline fallback states for single-player games. Cyberleek is also promoting a cryptocurrency token, $Cyberleek, with a market cap of .1 million, allowing token holders to vote on gameplay clips to release. The timing of the leaks suggests a possible European origin, and investigations link Cyberleek to past posts on a German cybersecurity forum. There are indications that Cyberleek is not affiliated with Rockstar Games, and if identified, they could face significant consequences. Rockstar's official gameplay reveal for GTA 6 is scheduled for August 27.
A manifesto linked to the leak of Grand Theft Auto 6 has prompted discussions among advocates of the Stop Killing Games campaign, which calls for games with single-player content to include an "offline fallback state." Stop Killing Games has distanced itself from the manifesto, acknowledging the authenticity of the leaks while condemning the illegal actions of the leaker, who is allegedly promoting a memecoin. The organization expressed empathy for the developers at Rockstar, emphasizing the negative impact of leaks on them and the gaming community. They noted the potential legal consequences for the leaker, referencing a past incident involving severe repercussions for a similar breach. At least two additional GTA 6 videos have emerged, with the official reveal scheduled for August 27.
A suspected advanced persistent threat (APT) group linked to China exploited a newly patched vulnerability in VMware vCenter (CVE-2026-59310), which has a critical CVSS score of 9.8, allowing for arbitrary code execution and the deployment of Babuk-derived ransomware. A recently patched vulnerability in Apple macOS (CVE-2026-65400) has been exploited to deploy a cryptocurrency miner, granting unauthorized root access. The Lazarus Group from North Korea exploited a zero-day vulnerability in Microsoft Windows, targeting defense and aerospace sectors. GeoServer patched a critical SQL injection vulnerability that was actively exploited. A new macOS malware, Amnesia Stealer, targets users through ClickFix attacks, stealing data and allowing real-time access to authenticated sessions. A novel attack technique named GhostSplice can manipulate AI coding assistants. Research revealed a method exploiting Chromium's DevTools Protocol for data theft. Noteworthy CVEs this week include CVE-2026-68820, CVE-2026-58231, and multiple others across various platforms. A high-severity command injection flaw in FileRun allows remote code execution. An advanced ClickFix attack has been reported, deploying sophisticated malware. A heap overflow vulnerability in Citrix NetScaler was patched after indications of exploitation. A new malware loader targeting Portuguese-speaking users has been identified. A significant reduction in exposed Automatic Tank Gauge systems has been observed. A phishing campaign targeting Brazil has been detected, and an F.B.I. agent faces charges for unauthorized crypto withdrawals. Authorities in Ukraine dismantled fraudulent call centers, and a North Carolina man was sentenced for cyber extortion. Unauthorized access to sensitive data by the ExfilSquad group has been confirmed. LightSpy activity linked to China has been detected in over 13 countries. A supply chain attack exposed over 2,500 companies, and an Azure exfiltration campaign has exposed millions of enterprise records.