cryptocurrency

AppWizard
October 7, 2026
A browser-based clone of Minecraft called "Tweetcraft" has been created by a user named jaivin, allowing multiplayer sessions within posts on X/Twitter. The game uses AI to operate seamlessly in the browser and offers in-game sponsorships purchasable with cryptocurrency. Although it resembles Minecraft, jaivin claims it does not use any of Minecraft's assets and is not affiliated with Mojang or Microsoft. The launch post for Tweetcraft received 7.4 million views, indicating positive reception despite concerns over potential legal issues. Additionally, other AI-generated gaming clones, such as browser-based versions of GTA 5 and Halo, have been released but faced takedowns from intellectual property owners. The rise of these AI-driven clones raises questions about the sustainability of such practices in the gaming industry.
AppWizard
October 7, 2026
Minecraft is now playable within posts on X (formerly Twitter) through a project called "Tweetcraft," developed by user jaivin using AI technology. Tweetcraft allows users to create a shared Minecraft world and post a link for others to join in real-time multiplayer sessions. Jaivin has also introduced in-game sponsorship opportunities, enabling players to purchase ad placements with cryptocurrency. The project operates without official authorization from Mojang or Microsoft, and jaivin claims it uses none of Minecraft's assets. The launch post has garnered over 7.4 million views, raising potential legal concerns. The community's response includes both enthusiasm and apprehension regarding possible legal challenges. Additionally, October has seen the emergence of browser-based versions of other popular games, highlighting the rapid innovation in AI-generated gaming content.
Tech Optimizer
September 25, 2026
Cybercriminals have developed an infostealer called MacSync, targeting Mac devices by using iCloud calendar events and cloud storage. This malware disguises itself as fake cryptocurrency wallets and pirated software. It begins with a loader that retrieves instructions from calendar entries and deploys malware to exfiltrate sensitive information, including credentials and cryptocurrency wallets. Recent versions have introduced an Objective-C backdoor that mimics Finder. Victims are often tricked into downloading these malicious applications, and effective antivirus solutions can prevent damage. Cybercriminals use tactics like SEO poisoning and phishing to direct victims to fraudulent websites or social media promoting pirated software. In one case, the loader was marketed as a cryptocurrency wallet, and victims encountered a misleading ClickFix error message that prompted them to execute a command in the Terminal.
Tech Optimizer
September 22, 2026
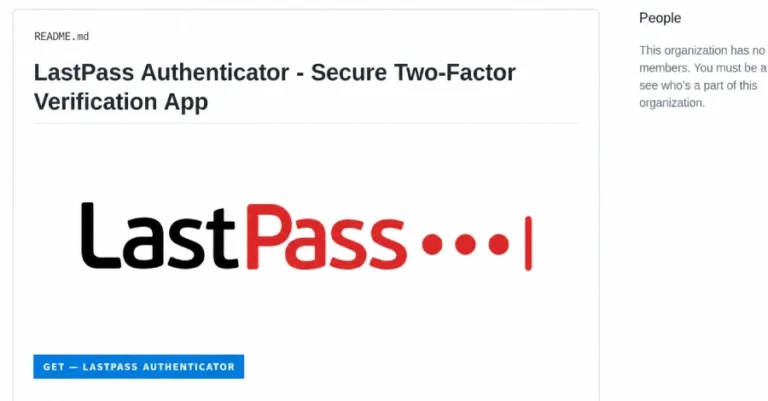
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
Search