cryptography

Tech Optimizer
September 14, 2026
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
Tech Optimizer
September 11, 2026
Microsoft BitLocker and Apple FileVault are free, integrated encryption solutions within their respective operating systems. As of 2026, the focus is on investing in management solutions that provide compliance proof, key escrow, recovery options, and policy enforcement across devices. Native encryption solutions lack certain management features, prompting the need for additional management layers from various vendors. Legacy freeware like TrueCrypt is no longer maintained, posing risks for business use, while VeraCrypt is a credible open-source alternative but lacks centralized management. Management options include Microsoft Intune for Windows, Sophos for mixed fleets, and specialized providers like Check Point and WinMagic for advanced needs. Organizations should ensure proper key management before enforcing encryption to avoid data loss and regularly test recovery processes. It is crucial to verify claims regarding compatibility and pre-boot options when selecting encryption solutions. Native engines are free, but management layers typically charge per endpoint annually.
AppWizard
August 29, 2026
Google has introduced several network security enhancements in Android 17 to improve user privacy. One key feature is Encrypted Client Hello (ECH), which encrypts domain names to prevent external observers from monitoring user activities. ECH is integrated with private DNS and is enabled by default for apps using compatible networking libraries. Google claims to be the first major mobile operating system to implement widespread ECH support. Testing conducted by Jigsaw showed stable connection success rates and minimal interference across various networks. Additional security features in Android 17 include: - Local Network Protection, requiring apps to request permission before accessing devices on a user's home network. - Certificate Transparency, mandating public logging of certificates to detect forged ones. - A 2G Network Shutdown option for mobile operators to disable 2G services, reducing exposure to phishing messages.
Winsage
August 24, 2026
Microsoft has issued an advisory to IT teams and software developers regarding significant changes in Windows code signing due to the expiration of the Windows Production PCA 2011 certificate in October 2026. The transition will involve stronger cryptographic algorithms, including RSA-3072 and SHA-384, which may cause compatibility issues for applications that rely on hardcoded certificate checks or outdated cryptographic standards. Microsoft plans to implement post-quantum cryptography by default for Windows code signing in 2027. IT administrators are encouraged to assess their software environments, confirm vendor compliance with supported trust-validation mechanisms, and ensure applications are tested against the new certificate hierarchy and signing algorithms. Organizations with private trust stores must establish processes for recognizing and deploying legitimate Microsoft certificate updates.
Winsage
August 18, 2026
China's Ministry of State Security has directed state-linked organizations to remove a tailored version of Windows 10 from their systems, expediting a planned phase-out initially set for February 2027. This directive is driven by data security concerns, although specific vulnerabilities were not disclosed. The customized version, developed by C&M Information Technologies (CMIT), is based on Windows 10 Enterprise but modified to exclude consumer features and ensure updates remain within China. Since its launch in 2017, it has been used by various central agencies. The Chinese government has also encouraged the elimination of foreign-branded computers, leading to the emergence of domestic operating systems. Despite these efforts, as of July 2026, Windows held an 87.64% share of desktop web traffic in China, with Windows 10 accounting for 43.56% of usage. Approximately two in five Chinese desktops still run an unsupported version of Microsoft's software.
Winsage
July 31, 2026
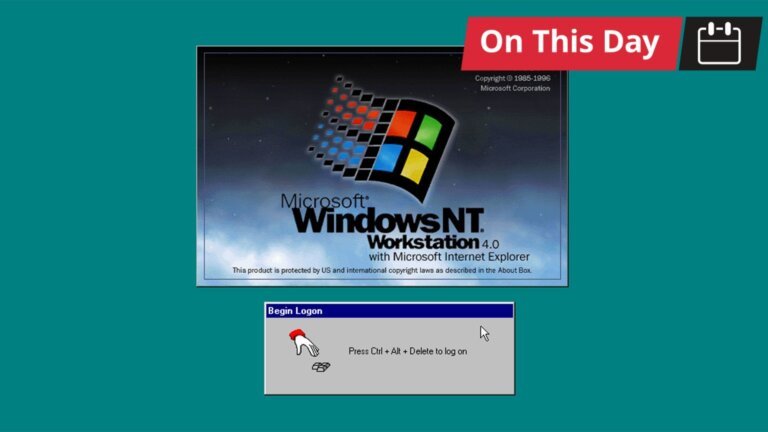
On July 31, 1996, Microsoft unveiled Windows NT 4.0 to its manufacturing partners. This release, codenamed Cairo, integrated the Windows 95 interface into a 32-bit enterprise OS and was the last version to support Alpha, MIPS, or PowerPC CPU architectures. The first public release of the NT line was Windows NT Server 3.1 in 1993, followed by versions 3.5 and 3.51 in 1994 and 1995, respectively. Windows NT 4.0 introduced features like My Computer and My Documents, as well as advanced components such as the cryptography API, DCOM, TAPI 2.0, and DirectX (v2). It had low minimum system requirements, recommending a CPU of 33 MHz or better, 32MB of RAM, SVGA graphics, and a 256 MB hard disk. NT 4.0 served as the foundation for Windows XP, which was released in 2001.
Winsage
July 31, 2026
On July 31, 1996, Microsoft released Windows NT 4.0, codenamed Cairo, which integrated the Windows 95 interface into a 32-bit enterprise operating system. It was the last version to support multiple CPU architectures, including Alpha, MIPS, and PowerPC. Windows NT 4.0 included features such as the Start Menu, Taskbar, Task Manager, and support for advanced functionalities like the cryptography API and DirectX (v2). The minimum hardware requirements were a CPU of 33 MHz or better, 32MB of RAM, SVGA graphics, and a 256 MB hard disk. Following its launch, Microsoft introduced versions for embedded systems and a Terminal Server edition. The release of Windows XP in 2001 marked a shift away from DOS-based consumer operating systems.
Search