cyber activities

Tech Optimizer
September 16, 2026
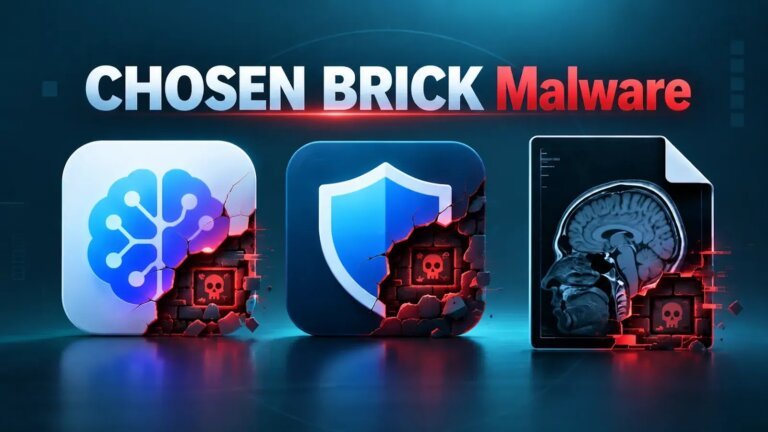
Iranian state-affiliated cyber actors are targeting dissidents, activists, and journalists using fake AI applications, counterfeit antivirus tools, and fabricated MRI scan results, primarily through a spyware family known as CHOSEN BRICK, which is designed for Windows systems. This campaign has been active since at least 2025 and affects individuals globally, including in the UK, US, and Netherlands. The malware establishes persistence via the Windows Registry Run key and communicates through Telegram, utilizing unique Bot IDs for each victim. CHOSEN BRICK is capable of extensive data collection, including capturing screenshots, recording audio, and stealing email content. Personal information from victims has been found on pro-Iranian leak sites, increasing harassment risks. Security measures should include monitoring for suspicious Registry entries and unusual communications, while users are advised to avoid unsolicited software installations and keep their systems updated. The FBI refers to this malware family as HEAVYGRAM.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
AppWizard
July 13, 2026
The European Union has sanctioned VK, the Russian technology firm behind VKontakte and its subsidiary MAX, due to their involvement in cyber activities and providing personal data to Russian authorities against dissenters. These sanctions were formalized on July 13 and align with a broader effort involving the UK, targeting individuals and entities linked to Russia's cyber operations. The MAX application is developed under the oversight of Russia's Federal Security Service (FSB). Additionally, Apple's removal of VK applications from its App Store has prompted a response from the Kremlin, with government spokesperson Dmitry Peskov indicating a need for clarification from Apple on this decision.
Search