cybersecurity firm

AppWizard
September 10, 2026
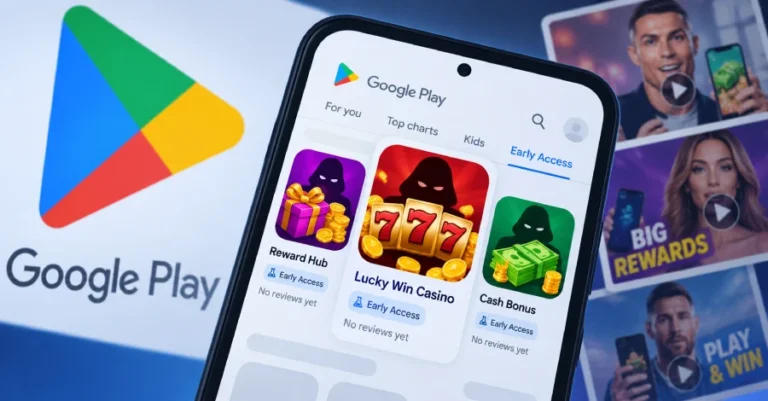
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Tech Optimizer
September 2, 2026
Gen Digital stock (ISIN US3687361044) traded at 30.02 dollars on September 1, 2026, reflecting a 3.2 percent decline from the previous close. The stock is within a 52-week trading range of 17.78 to 31.29 dollars, currently less than 4 percent below the 52-week high of 31.29 dollars. The intrinsic GF Value for the shares is estimated at 33.22 dollars, indicating the current price is 9.6 percent below this fair value. The stock has increased approximately 69 percent from its 52-week low of 17.78 dollars. Gen Digital introduced the Fearless Planet Index, showing North America with an average digital risk score of 29.6 percent, Europe at 28.5 percent, Asia-Pacific at 27.4 percent, the Middle East and Africa at 25.6 percent, and Latin America at 22.0 percent. The stock is quoted at 30.02 dollars on Nasdaq as of September 1, 2026.
Tech Optimizer
August 31, 2026
Silver Fox is linked to the distribution of a backdoor malware called ValleyRAT, disguised as the legitimate QN Wallpaper adware application. Once installed, ValleyRAT provides complete control over the compromised machine. The malware uses DLL sideloading to operate under the guise of a legitimate process, bypassing security measures. It disables Windows Defender and adds itself to autorun entries, and can mark its process as critical, causing system crashes if terminated. Kaspersky has identified specific indicators of compromise (IoCs) including hashes, command-and-control servers, and associated domains. In 2026, Kaspersky recorded over 100,000 detections of ValleyRAT affecting more than 1,500 unique users, mainly in China and India.
Winsage
August 27, 2026
Researcher Dominik Reichel has identified a new malware implant called SLEEPWALKER, which is disguised as an agent from ESET. SLEEPWALKER is unique because it does not contain malicious code and remains dormant until it receives specific network signals to activate. It appears to be designed for targeted attacks, likely orchestrated by nation-states. Although it was submitted to VirusTotal last year, it has not been linked to any active campaigns or confirmed victims. The origins of SLEEPWALKER are unknown, and its code is described as somewhat "rough around the edges," indicating it may still be in development.
TrendTechie
August 19, 2026
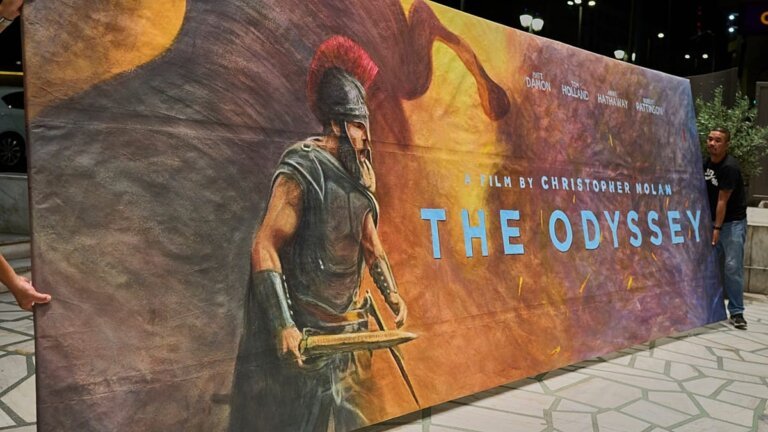
Pirated digital copies of the film "Odyssey" are being used to spread the Lumma Stealer malware, which compromises viewers' computers. Bitdefender's internal data shows that users have attempted to download malicious executable files disguised as the film, which has not yet been released on online platforms. These counterfeit copies are circulating on illegal sites, and the Lumma Stealer malware can steal sensitive information from infected devices. Bitdefender identified several bait file names that are actually executable files designed to infect computers rather than play the film. This tactic follows a trend of using popular films to disseminate malware, with similar campaigns documented in the past. Cybercriminals exploit the gap between a film's theatrical release and its availability on legal streaming platforms. Users are advised to watch films only through verified services and to keep their cybersecurity software updated.
Winsage
August 17, 2026
A suspected advanced persistent threat (APT) group linked to China exploited a newly patched vulnerability in VMware vCenter (CVE-2026-59310), which has a critical CVSS score of 9.8, allowing for arbitrary code execution and the deployment of Babuk-derived ransomware. A recently patched vulnerability in Apple macOS (CVE-2026-65400) has been exploited to deploy a cryptocurrency miner, granting unauthorized root access. The Lazarus Group from North Korea exploited a zero-day vulnerability in Microsoft Windows, targeting defense and aerospace sectors. GeoServer patched a critical SQL injection vulnerability that was actively exploited. A new macOS malware, Amnesia Stealer, targets users through ClickFix attacks, stealing data and allowing real-time access to authenticated sessions. A novel attack technique named GhostSplice can manipulate AI coding assistants. Research revealed a method exploiting Chromium's DevTools Protocol for data theft. Noteworthy CVEs this week include CVE-2026-68820, CVE-2026-58231, and multiple others across various platforms. A high-severity command injection flaw in FileRun allows remote code execution. An advanced ClickFix attack has been reported, deploying sophisticated malware. A heap overflow vulnerability in Citrix NetScaler was patched after indications of exploitation. A new malware loader targeting Portuguese-speaking users has been identified. A significant reduction in exposed Automatic Tank Gauge systems has been observed. A phishing campaign targeting Brazil has been detected, and an F.B.I. agent faces charges for unauthorized crypto withdrawals. Authorities in Ukraine dismantled fraudulent call centers, and a North Carolina man was sentenced for cyber extortion. Unauthorized access to sensitive data by the ExfilSquad group has been confirmed. LightSpy activity linked to China has been detected in over 13 countries. A supply chain attack exposed over 2,500 companies, and an Azure exfiltration campaign has exposed millions of enterprise records.
AppWizard
August 4, 2026
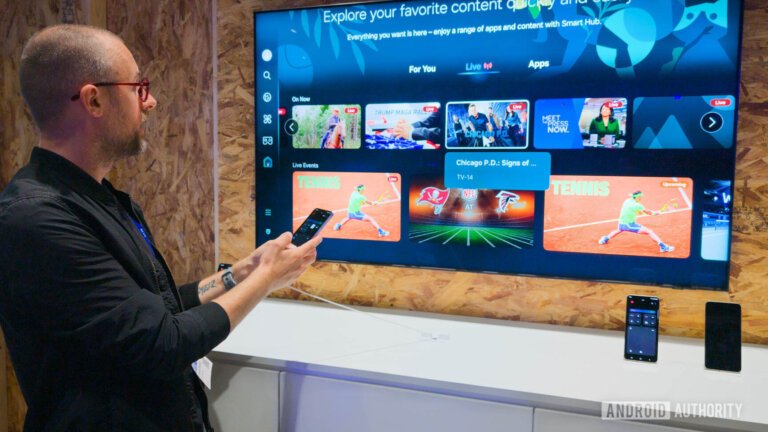
Security researchers found that several Samsung Smart TV applications, including Pac-Man, were embedding residential proxy SDKs from data brokers like Bright Data. In response, Samsung has banned the inclusion of residential proxy functionality in new app submissions and is working to remove existing apps with such software. The investigation by Norwegian cybersecurity firm Mnemonic revealed that the Bright Data SDK was integrated into various gaming applications, some promoted by Samsung. While Samsung TVs were not automatically sharing internet connections, the SDK could be activated remotely by developers, requiring user consent. Once consent was granted, the proxy service could operate in the background. Many Samsung TV applications were found to download most of their code from remote servers, complicating verification processes. The issue of residential proxy software is not limited to Samsung, as it has also been identified in various Android apps and devices. Following these findings, LG and Google have also taken measures to address the risks associated with residential proxy networks.
Tech Optimizer
July 15, 2026
Cybersecurity firm ArcticWolf has identified 292 malicious GitHub repositories that impersonate legitimate software tools, part of a campaign to deliver a new variant of the BoryptGrab infostealer. This malware can extract sensitive information from 19 web browsers, 32 cryptocurrency wallets, messaging applications like Telegram and Discord, gaming platforms such as Steam, and Windows Credential Manager. It can also exfiltrate files from users' Desktop and Documents folders and capture screenshots. This variant bypasses Chrome’s App-Bound Encryption using direct code injection and does not include an anti-analysis layer or conceal itself, aiming to harvest data quickly without persistence. The malicious activity began in late June, with most repositories removed from GitHub, though several dozen remain active. GitHub's status as a key platform in the open-source community makes it a target for cybercriminals, emphasizing the need for developers to thoroughly vet code before integration.
Search