cybersecurity firm

AppWizard
October 9, 2026
Researchers from Bitdefender have discovered that thousands of inexpensive Android devices are preloaded with malware called "Midnight Mimosa," which generates fraudulent advertising revenue. This malware is embedded in the device firmware before the first power-up, making it impossible for users to uninstall. It operates with system-level privileges, allowing it to install or remove applications without user consent and to download additional code. The malware primarily aims for financial gain through advertising and click fraud, while also gathering information about devices. Bitdefender has detected this malware on thousands of devices across over 150 countries, with the highest concentrations in Mexico, France, and Italy, followed by the United States, Germany, Brazil, and Spain. Many affected devices are low-cost, white-label, or counterfeit models, often sold online. The malware stealthily installs legitimate-looking applications that display ads in invisible windows, generating ad impressions without user awareness. Bitdefender identified at least 32 disguised applications and found 13 apps in the Google Play Store with similar ad-fraud code. The source of the malware remains unidentified, but some affected firmware was signed with certificates from Shenzhen Zediel, a Chinese company. The researchers suggest that the malware could have been introduced at various stages of the supply chain, potentially by manufacturers or intermediaries.
Tech Optimizer
October 1, 2026
AhnLab’s V3 antivirus software received a perfect score in the latest evaluation by AV-TEST, making it the only South Korean product to achieve this in the assessment conducted in July and August 2026. Both V3 Endpoint Security and V3 Internet Security scored the maximum of 18 points, earning the title of “Top Products” from AV-TEST. AhnLab has participated in AV-TEST’s evaluations since 2013, competing against major global cybersecurity firms.
AppWizard
September 30, 2026
Russian cybersecurity firm Positive Technologies has identified 11 security vulnerabilities affecting Android and Apple devices, with nine related to Apple and two to Android, classified as high severity. The Android vulnerabilities include one that allows attackers to exploit an NFC tag to execute an app without owner approval and another that lets installed apps modify network settings without additional permissions. Google has addressed these issues in its September 2026 security patches. For Apple, vulnerabilities include a macOS flaw that allows malicious apps to gain the highest system privileges and another that exposes sensitive information. Apple has released patches for these vulnerabilities, but specific OS versions affected have not been disclosed. Users are advised to ensure their devices have the latest security updates to mitigate risks.
AppWizard
September 10, 2026
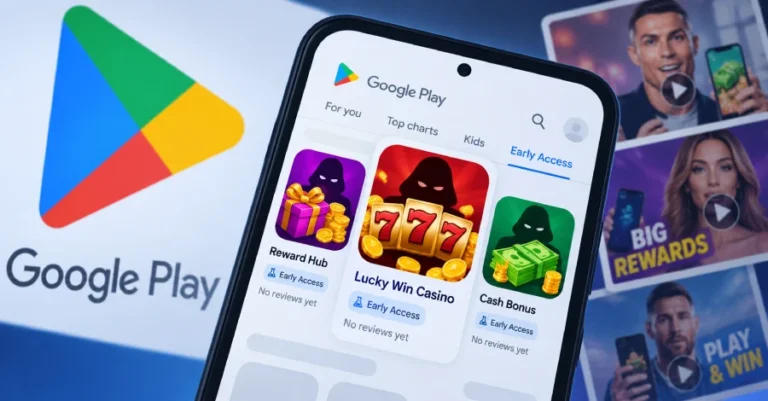
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Tech Optimizer
September 2, 2026
Gen Digital stock (ISIN US3687361044) traded at 30.02 dollars on September 1, 2026, reflecting a 3.2 percent decline from the previous close. The stock is within a 52-week trading range of 17.78 to 31.29 dollars, currently less than 4 percent below the 52-week high of 31.29 dollars. The intrinsic GF Value for the shares is estimated at 33.22 dollars, indicating the current price is 9.6 percent below this fair value. The stock has increased approximately 69 percent from its 52-week low of 17.78 dollars. Gen Digital introduced the Fearless Planet Index, showing North America with an average digital risk score of 29.6 percent, Europe at 28.5 percent, Asia-Pacific at 27.4 percent, the Middle East and Africa at 25.6 percent, and Latin America at 22.0 percent. The stock is quoted at 30.02 dollars on Nasdaq as of September 1, 2026.
Tech Optimizer
August 31, 2026
Silver Fox is linked to the distribution of a backdoor malware called ValleyRAT, disguised as the legitimate QN Wallpaper adware application. Once installed, ValleyRAT provides complete control over the compromised machine. The malware uses DLL sideloading to operate under the guise of a legitimate process, bypassing security measures. It disables Windows Defender and adds itself to autorun entries, and can mark its process as critical, causing system crashes if terminated. Kaspersky has identified specific indicators of compromise (IoCs) including hashes, command-and-control servers, and associated domains. In 2026, Kaspersky recorded over 100,000 detections of ValleyRAT affecting more than 1,500 unique users, mainly in China and India.
Winsage
August 27, 2026
Researcher Dominik Reichel has identified a new malware implant called SLEEPWALKER, which is disguised as an agent from ESET. SLEEPWALKER is unique because it does not contain malicious code and remains dormant until it receives specific network signals to activate. It appears to be designed for targeted attacks, likely orchestrated by nation-states. Although it was submitted to VirusTotal last year, it has not been linked to any active campaigns or confirmed victims. The origins of SLEEPWALKER are unknown, and its code is described as somewhat "rough around the edges," indicating it may still be in development.
TrendTechie
August 19, 2026
Pirated digital copies of the film "Odyssey" are being used to spread the Lumma Stealer malware, which compromises viewers' computers. Bitdefender's internal data shows that users have attempted to download malicious executable files disguised as the film, which has not yet been released on online platforms. These counterfeit copies are circulating on illegal sites, and the Lumma Stealer malware can steal sensitive information from infected devices. Bitdefender identified several bait file names that are actually executable files designed to infect computers rather than play the film. This tactic follows a trend of using popular films to disseminate malware, with similar campaigns documented in the past. Cybercriminals exploit the gap between a film's theatrical release and its availability on legal streaming platforms. Users are advised to watch films only through verified services and to keep their cybersecurity software updated.
Search