data exfiltration

AppWizard
August 23, 2026
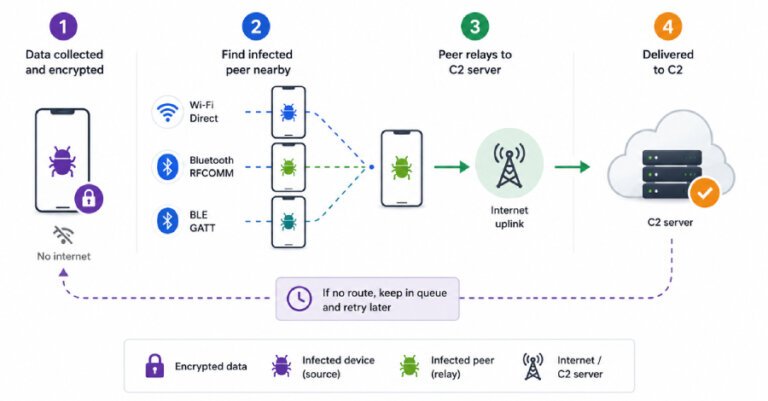
A new Android malware threat, codenamed Manic, poses significant risks to Ukrainian banks, government services, and messaging applications, with a reach extending to Russian and European financial institutions, global fintech platforms, cryptocurrency services, and military communication channels. Manic combines Android banking malware and mobile spyware, targeting sensitive applications and enabling comprehensive device takeover. It features a novel Wi-Fi mesh technique for data relay through compromised devices and utilizes phishing sites and dropper apps. The malware originated in February 2026, with initial development leading to its first deployment by late May. It monitors 169 package IDs related to banks, payment services, and messaging applications, primarily affecting Ukrainian targets but also impacting applications in Russia and Europe. Manic can infiltrate commercial and military messaging apps, track locations, monitor notifications, and collect files. It exploits Android's accessibility services to capture sensitive data and employs a store-and-forward relay mechanism for data exfiltration through nearby compromised devices. Google has stated that no apps containing this malware are found on Google Play, and Android users are protected by Google Play Protect.
Tech Optimizer
July 25, 2026
A new remote access trojan (RAT) named msaRAT has been identified by Cisco Talos, linked to the Chaos ransomware group and built using Rust. It exploits Chrome and Edge browsers to disguise its traffic and evade detection. MsaRAT operates through a headless browser process, enabling remote code execution and facilitating ransomware deployment, data theft, and other malicious activities. It is typically installed via phishing emails or malicious files, making it resistant to standard browser patches. Cisco Talos recommends specific SNORT rules and a ClamAV signature for detection. Indicators of Compromise (IoC) include traffic to the IP address 172.86.126.18 and the domain is-01-ast.ols-img-12.workers.dev. The malware primarily targets large organizations, but individual users may also be at risk.
Winsage
June 19, 2026
Microsoft has introduced the Microsoft Execution Containers (MXC) SDK to establish Windows as a reliable operating system for autonomous agents, focusing on containment, identity, and manageability. The MXC framework serves as a policy-driven execution layer for agents on Windows and Windows Subsystem for Linux (WSL), allowing developers to set access permissions using JSON or TypeScript. It employs process and session isolation for agent containment and identity. Future enhancements will include micro-VM support for high-risk tasks and integration with Windows 365 for cloud PC workloads. IT teams can manage MXC policies through Entra ID and Intune, while Defender and Purview provide protection and observability. The MXC framework is built on Microsoft's security initiatives, including Secure Boot and passwordless sign-in, allowing agents to inherit a secure foundation. However, early commentary expresses caution regarding MXC's perception as a comprehensive security solution, noting issues with overly permissive policies and the lack of outbound network filtering. Other platforms, such as Linux, are also enhancing security for agents with kernel-level isolation and secure environments like NVIDIA's OpenShell runtime. Various projects are focusing on agent sandboxes within Kubernetes, employing technologies like gVisor and Kata Containers for isolation. Overall, no singular dominant platform security model for AI agents has emerged, with Windows' MXC still considered nascent compared to existing solutions in Linux and Kubernetes ecosystems.
Winsage
June 12, 2026
OnyxC2 is a sophisticated credential stealer available for a subscription fee of 0 per month, distributed through disguised lures such as fake Windows updates and legitimate software installers. It functions as a commercial product with features like an automated payload builder, tiered licensing, and a centralized web dashboard. The malware boasts a 99% detection-evasion rate, successfully evading major antivirus solutions during tests. It is developed in C++, utilizing direct system calls and mutating with each build to avoid detection. OnyxC2 collects data from around 210 applications, targeting 45 web browsers, password managers, cryptocurrency wallets, and FTP clients. The malware is delivered using DLL sideloading, where a password-protected archive contains a legitimate application and a malicious DLL. The attacker's DLL is disguised by inflating its size and is loaded by a trusted binary. The malicious code remains encrypted on disk and decrypts in memory to evade analysis. OnyxC2 communicates with a Cloudflare-fronted command-and-control server to manage infected hosts and execute commands like hardware registration and cookie uploads. The threat extends to business environments, targeting FTP and email clients, with stolen session cookies allowing ongoing access to corporate infrastructure. Implementing anti-data exfiltration controls is recommended as a mitigation strategy.
AppWizard
May 28, 2026
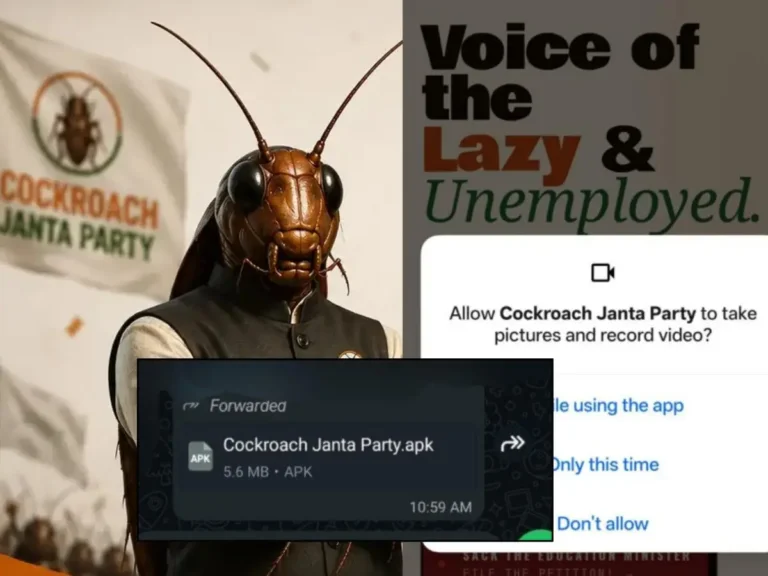
A cybersecurity report released on May 22, 2026, identifies a counterfeit Android application posing as the official app of the Cockroach Janta Party as a significant malware threat. The malicious app, known as Cockroach.Janta.Party, functions as a Remote Access Trojan (RAT) and can infiltrate Android devices, steal sensitive information, intercept communications, and control infected smartphones. The genuine Cockroach Janta Party has no affiliation with this app and is a victim of brand impersonation. The app is distributed through WhatsApp, Telegram, and misleading websites, particularly a rogue domain, cockroachjantaparty[.]org. It targets Android devices running versions 8.0 to 14 and requests elevated permissions, including access to camera, SMS, call logs, and contacts, while misusing the Android Accessibility Service to read on-screen content and grant itself additional permissions. The app contains multiple malicious modules for data exfiltration and uses a Command and Control infrastructure based on the Telegram Bot API. Users are advised to uninstall the app, disable Accessibility permissions, reset banking credentials, enable two-factor authentication, and conduct a full mobile security scan. The legitimate Cockroach Janta Party is encouraged to issue a formal clarification regarding the impersonation.
Search