deceptive tactics

Tech Optimizer
September 15, 2026
Iranian state-sponsored hackers are targeting dissidents, activists, and journalists using deceptive tactics, including malicious applications that impersonate reputable cybersecurity products like Norton Antivirus and KeePass. The FBI and UK authorities issued a warning about these hackers, who establish rapport with targets via social messaging platforms, posing as IT support or known contacts. They convince victims to download files that appear authentic, including AI video creation applications and other software. The spyware, named “Chosen Brick,” infects Windows PCs and has capabilities such as capturing screen content, recording audio, collecting message data, and downloading additional malware. The hackers have exploited this spyware to publish personal details of victims, increasing their harassment. The FBI advises potential victims on detecting the spyware and recommends enabling antivirus software, running regular scans, and avoiding unofficial downloads.
AppWizard
September 10, 2026
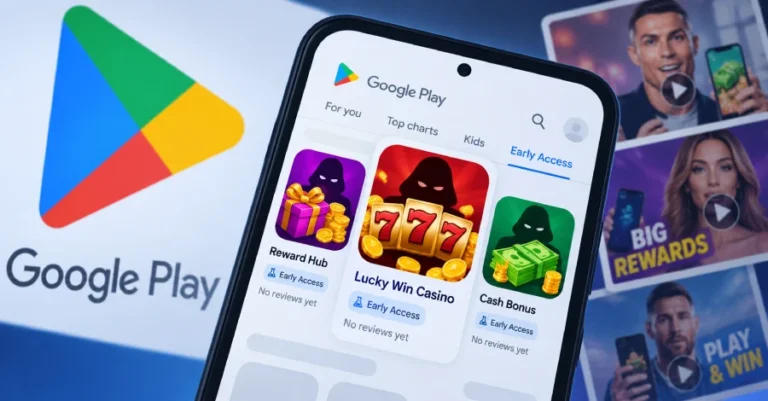
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
Tech Optimizer
August 8, 2026
Securonix Threat Research has identified a cyber campaign called SMOKE#SCREEN that uses deceptive tactics to trick users into installing weaponized versions of ScreenConnect, a legitimate remote monitoring software. The attackers disguise their malicious intent with fake update notifications for applications like Zoom and Adobe, as well as counterfeit business documents. This campaign allows attackers to gain persistent remote access to victims' systems, disable security protections, and exploit trusted services like Dropbox and Cloudflare for delivering malicious payloads. Victims have been reported on both Windows and macOS platforms. Businesses are advised to verify updates through official channels and train staff on the risks of unexpected software installations.
Search