deceptive websites

Winsage
September 30, 2026
Microsoft has introduced a new feature called Assisted Setup in Windows 11, which allows users to install popular third-party applications like TikTok, WhatsApp, and Spotify immediately after the out-of-box experience (OOBE). This feature is gradually rolling out with build 26340.9354, released on September 8. Users can opt for automatic downloads and installations of these applications, but they must explicitly consent to download them, unlike pre-installed apps like OneDrive and Phone Link. The setup process also allows users to pin popular websites to the taskbar, with recommendations based on geographical location. Windows 11 26H2 has been officially released.
Winsage
September 24, 2026
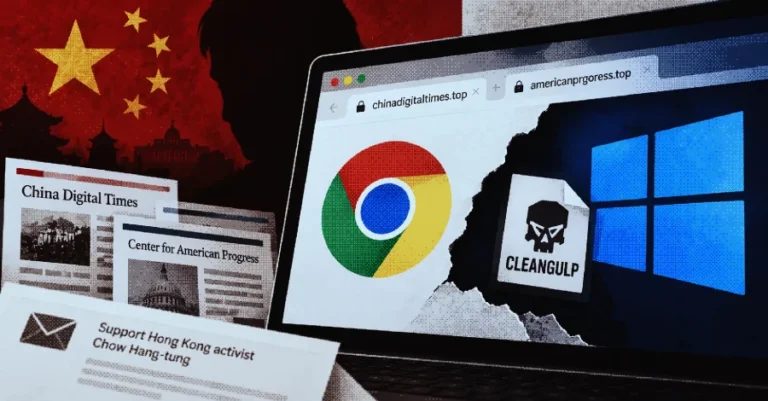
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Tech Optimizer
August 29, 2026
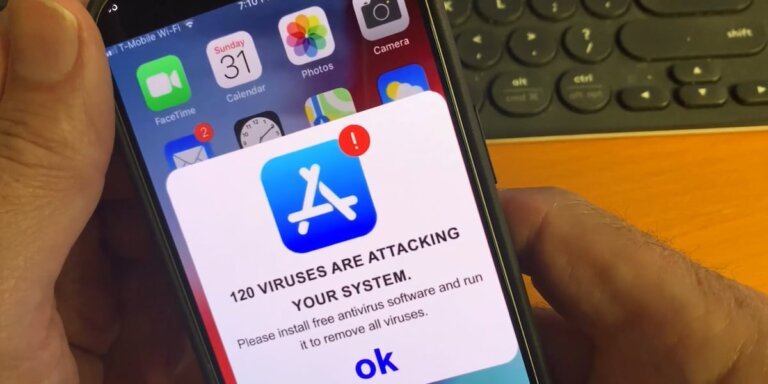
A viewer reported receiving a popup on her smartphone claiming her system was infected with 120 viruses, which is a scam designed to provoke panic and encourage the download of a free antivirus app called “Total Cleaner.” This popup aims to trick users into downloading an app that may have hidden costs, initiate expensive subscriptions, or direct them to phishing sites. The app “Total Cleaner” has fake reviews, hidden costs after installation, and privacy concerns regarding personal data collection. Most modern smartphones do not require traditional antivirus programs, and such popups are advertisements from deceptive sources. To protect against these alerts, users should close the tab immediately, keep their devices updated, and only download apps from official app stores after thorough research.
Tech Optimizer
August 17, 2026
The landscape of mobile security has shifted away from traditional third-party antivirus software, as modern Android devices are equipped with built-in security features. Key components of this security framework include Google Play Protect, which blocked 27 million malicious apps in 2025; application sandboxing that isolates apps; proactive permissions that enhance user privacy; AI-powered threat detection for sophisticated attacks; and strict sideloading policies to limit risks from off-market malware. Despite these defenses, threats such as social engineering, phishing, malicious push notifications, and unsecured public Wi-Fi remain prevalent, often evading traditional antivirus solutions. However, certain scenarios, such as frequent sideloading, using older devices, connecting to public Wi-Fi, or suspected infections, may warrant the use of third-party antivirus apps for additional protection. Overall, the built-in security features of Android provide a strong defense for most users, with user education being crucial for effective smartphone protection.
Winsage
May 20, 2026
Bitdefender's research highlights the use of Microsoft's MSHTA utility in malware attacks, noting its default activation in Windows systems. Cybercriminals exploit MSHTA to execute malicious scripts under the guise of legitimate processes, linking it to various malware families like LummaStealer and PurpleFox. The study reports a rise in MSHTA-related detections, indicating a shift towards "living-off-the-land" tactics that utilize legitimate tools to evade security alerts. Social engineering is identified as a common entry point for attacks, employing deceptive methods such as fake software downloads and phishing links. MSHTA can retrieve and execute additional payloads through multi-stage chains, complicating detection efforts. The attacks target sensitive information, including credentials and financial data, and the continued presence of MSHTA poses risks as it allows threat actors to conceal malicious actions. To mitigate these threats, organizations are advised to restrict or disable legacy scripting tools and exercise caution with untrusted downloads. The report emphasizes the challenge of detecting unusual behaviors associated with legitimate utilities in the context of cyber threats.
AppWizard
December 11, 2025
DroidLock is a newly identified ransomware targeting Android users in Europe, capable of locking users out of their devices and demanding ransom for access or threatening permanent data deletion. It spreads through deceptive websites promoting counterfeit applications and gains access to devices by monitoring user passcodes. Victims report ransom demands displayed on their screens, often accompanied by a countdown timer. The ransomware employs phishing tactics to lure users into downloading harmful software, which can lock screens, obtain app lock credentials, exploit device administrator privileges, capture images, and silence devices. While it has not yet reached the UK, experts advise users to download applications only from official sources like the Google Play Store and to verify developer credentials for third-party software.
Search