Defender Antivirus

Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Winsage
September 20, 2026
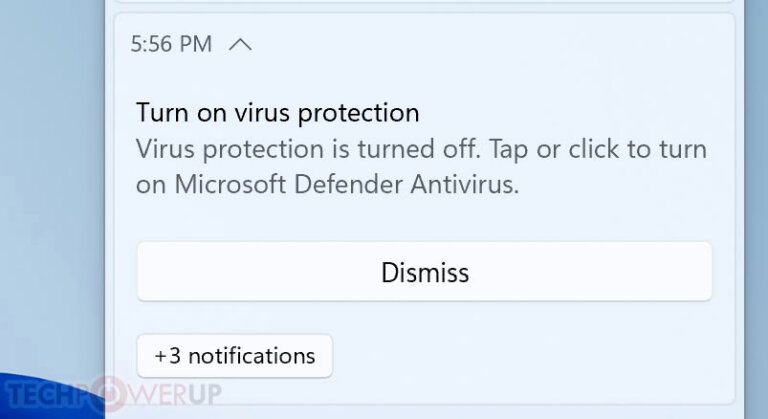
Microsoft resolved an issue in its Windows Security framework that incorrectly indicated Microsoft Defender Antivirus was disabled. This fix was implemented through Defender platform update 4.18.26080.4, released on September 17. The update installs automatically unless users have blocked mandatory security updates. Users had been receiving false alerts during system boot and intermittently afterward, which redirected them to the Windows Security home tab where settings appeared normal. Microsoft acknowledged the issue on August 28, affecting all supported versions of Windows and Windows Server with the latest Defender updates, but did not specify the triggering update. Users in the Windows Insider program reported similar warnings as early as June.
Tech Optimizer
September 19, 2026
For nearly two months, Windows 11 users received persistent notifications from the Windows Security app falsely indicating that Microsoft Defender was disabled, despite it functioning properly. This issue, which began in early August, has been addressed with a security update from Microsoft. The false alerts affected all versions of Windows 11, Windows Server, and Windows 10, and were linked to a bug introduced with a recent Defender security update. Microsoft confirmed that no manual action is required from users to resolve the issue, as the fix will be automatically deployed to all PCs with mandatory security updates enabled. The problem was resolved in the Microsoft Defender Antivirus update (version 4.18.26080.4), released on September 17, 2026. Users can verify the status of Defender by checking Windows Security or using a PowerShell command.
Winsage
September 19, 2026
Microsoft resolved an issue that caused misleading alerts indicating that Defender Antivirus was disabled after recent updates. This fix was confirmed in an update to the Windows release health dashboard and was implemented in the Microsoft Defender Antivirus update (version 4.18.26080.4) rolled out on September 17. The bug, acknowledged by Microsoft in late August, affected users in the Release Preview Channel of the Windows Insider program since at least June and impacted all supported versions of Windows clients and servers. Users received erroneous notifications in the Windows Security app prompting them to activate Microsoft Defender Antivirus, despite it functioning correctly. Misleading alerts could appear upon Windows startup and intermittently thereafter, even when notification settings were disabled.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
Winsage
September 11, 2026
Microsoft addressed a significant bug that affected the launch of Teams and Outlook on ARM-based Windows devices after updates from the August 2026 Patch Tuesday. The issue primarily impacted users of devices like the Surface Pro 11 and Surface Laptop 7 running Windows 11 24H2 or later, who had not installed necessary updates from the Microsoft Store. The bug caused Teams and Outlook to fail to launch or close unexpectedly following the installation of security updates released on or after August 11, 2026 (KB5121003). Classic versions of Outlook and other applications were not affected. A temporary workaround was suggested, involving updating the Auto Super Resolution Package. The bug was resolved through cumulative updates released on September 8, 2026 (KB5124012), and users were urged to install the latest updates for improvements and issue resolutions. Additionally, Microsoft acknowledged other issues related to updates from August, including disruptions in printing and PDF exporting due to .NET Framework updates, gaming problems from peripherals with RGB lighting, and alerts regarding Microsoft Defender Antivirus being disabled. They also fixed issues related to the loss of custom mouse settings and desktop configurations following the installation of the KB5120998 August 2026 preview update.
Tech Optimizer
September 8, 2026
Microsoft has acknowledged a software bug causing persistent Windows Security pop-ups that incorrectly indicate antivirus protection is disabled. These notifications began appearing after the latest Microsoft Defender Antivirus updates, but the antivirus is functioning correctly. The issue affects various versions of Windows and Windows Server with the latest Defender updates. Microsoft has committed to resolving the issue in a future update, though no timeline has been provided. Users are advised to verify the status of their antivirus through the Windows Security app and disregard the notifications until a fix is released.
Winsage
September 7, 2026
Microsoft is facing significant security and reliability issues, particularly related to system startup, BitLocker recovery, and updating Secure Boot certificates. Users have expressed confusion over these complexities, especially regarding Microsoft Defender Antivirus errors. These problems stem from a tumultuous period before the launch of Windows 11, including changes to the TPM requirement and the extension of Windows 10's life. Despite increased security patches, underlying issues remain, leading to user skepticism about the reliability of Windows systems.
Tech Optimizer
September 4, 2026
Microsoft has acknowledged a software bug in its Windows operating system that causes misleading pop-up notifications, indicating that antivirus protection is disabled. These alerts began appearing after the latest Microsoft Defender Antivirus updates, despite the antivirus functioning correctly. The notifications can occur at startup and intermittently, and cannot be silenced through standard notification controls. The issue affects various versions of Windows and Windows Server with the latest Defender updates. Microsoft is working on a resolution, but no timeline has been provided. Users are advised to verify their antivirus status through the Windows Security app and can ignore the notifications if real-time protection is confirmed as active.
Search