Defender Update

Winsage
September 22, 2026
Recent investigations have shown that a specific update to Microsoft Defender has caused performance issues for VLC Media Player, particularly a slowdown in startup times. Jean-Baptiste Kempf, a VideoLAN developer, attributed this sluggishness to a bug in the Microsoft Defender update, which quarantined VLC's plug-in cache. The problematic Defender signature update is version 1.455.50.0, linked to Windows Update KB5121003 released on August 11th. Users can reset the plug-in cache to improve performance by either reinstalling VLC or using the built-in functionality to regenerate the cache with vlc-cache-gen.exe. Alternatively, users can reset preferences and cache files by searching for "VLC" and selecting the reset option. Microsoft has not yet provided a fix for these issues, and users may need to set an exclusion in Microsoft Defender for VLC Media Player to prevent unnecessary scans, enhancing its performance.
Winsage
September 20, 2026
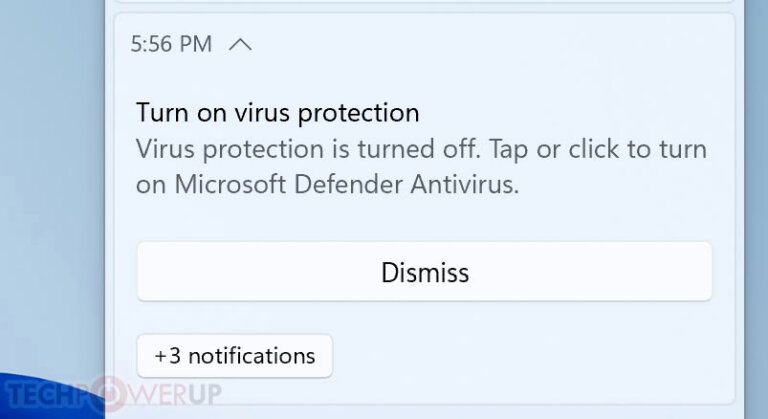
Microsoft resolved an issue in its Windows Security framework that incorrectly indicated Microsoft Defender Antivirus was disabled. This fix was implemented through Defender platform update 4.18.26080.4, released on September 17. The update installs automatically unless users have blocked mandatory security updates. Users had been receiving false alerts during system boot and intermittently afterward, which redirected them to the Windows Security home tab where settings appeared normal. Microsoft acknowledged the issue on August 28, affecting all supported versions of Windows and Windows Server with the latest Defender updates, but did not specify the triggering update. Users in the Windows Insider program reported similar warnings as early as June.
Winsage
August 16, 2026
Microsoft released its August 2026 Patch Tuesday updates, including the latest Defender package for ISO installations. The updates are aimed at combating malware threats and are issued approximately every three months for Windows installation images (WIM and VHD) and ISOs. The latest Windows 11 update is available through the Media Creation Tool (MCT). The security definitions were delivered through security intelligence update version 1.455.50.0, applicable to various platforms including Windows 11, Windows 10 ESU, Windows Server 2022, and others. The update includes enhancements to the anti-malware client, engine, and signature versions, with platform version 4.18.26070.9, engine version 1.1.26070.7, and security intelligence version 1.455.50.0. The previous security intelligence update was version 1.447.236.0, which introduced detections for various malware types. The most recent intelligence update is version 1.457.181.0.
Winsage
June 8, 2026
Microsoft has rolled out new Defender patches for Windows 11 ISOs, aligning with its commitment to security updates. Updates for Microsoft Defender for Endpoint's endpoint detection and response (EDR) will no longer be included with monthly Windows security updates or Patch Tuesdays; they will now be delivered via Microsoft Update. This change aims to allow faster deployment of EDR enhancements independently of the operating system's update cycle. The rollout for Windows 10 began in late May 2026, with plans to extend support to Windows 11 and other versions by fall 2026. EDR updates will be delivered using KB5005292, contingent on prerequisite updates. Systems must run Sense version 10.8798.25857.1000 or later and have specific Windows updates installed to qualify for the new delivery method. Organizations should align their update policies with this new approach before the broader rollout. In case of significant issues, the EDR update can be reverted using a specific command. Further details are available in the Microsoft 365 Admin Center under message ID MC1381119.
Winsage
June 6, 2026
Microsoft is rolling out updates for Windows Defender to protect users from newly discovered malware threats. These updates occur frequently, with a significant refresh every three months for Windows installation images (WIM and VHD) and ISOs. The recent Windows 11 update includes the latest definitions and addresses vulnerabilities from outdated anti-malware definitions in installation images. The latest security definitions were delivered through security intelligence update version 1.445.323.0, applicable to various platforms, including Windows 11 and several Windows Server versions. The update enhances the anti-malware client, engine, and signature versions to platform version 4.18.26040.7, engine version 1.1.26040.8, and security intelligence version 1.447.236.0. The most recent intelligence update is version 1.451.297.0, which improves threat detection against various malware types.
Winsage
May 21, 2026
In April 2026, two zero-day vulnerabilities, RedSun and UnDefend, were discovered in Microsoft Defender, affecting Windows 10, Windows 11, and Windows Server platforms. These vulnerabilities allow attackers to escalate privileges to SYSTEM and bypass Defender’s protections. RedSun exploits a flaw in Defender's remediation process, enabling low-privileged users to overwrite critical system files. UnDefend allows attackers to disrupt Defender’s updates, keeping it outdated and ineffective. Both vulnerabilities are actively being exploited, with attackers leveraging them to gain persistent access and deploy ransomware. The primary targets are organizations using Windows systems with Defender enabled, particularly in sectors like finance, healthcare, and government. Mitigation strategies include applying updates for related vulnerabilities, monitoring for suspicious activities, and implementing additional security measures.
Winsage
May 5, 2026
Microsoft's Defender anti-malware tool update version 1.449.425.0 removed two DigiCert root digital certificates, leading to false positives that flagged them as severe malware (Trojan:Win32/Cerdigent.A!dha). This incident was later identified as a false positive, and updating to version 1.449.430.0 or later reinstates the certificates. The issue may be linked to a DigiCert employee encountering disguised malware. Additionally, Windows updates from April 14 caused third-party backup applications to malfunction due to the addition of vulnerable psmounterex.sys kernel driver versions to a blocklist. Users experienced difficulties with mounting backup image files, and Microsoft referenced a vulnerability rated 9.3 out of 10 in the driver. Other affected software includes Acronis Cyber Protect Cloud and UrBackup server. Microsoft has not explained the delay in adding the vulnerable driver to the blocklist, and other recent update-related issues have also been reported.
Winsage
April 8, 2026
Microsoft released a security intelligence update for Microsoft Defender Antivirus on April 7, 2026, enhancing protection for Windows 11, Windows 10, and Windows Server. The update introduces refined threat detection capabilities to combat malware and zero-day attacks, utilizing advanced detection logic and cloud-based protection. The security intelligence version is 1.447.209.0, engine version is 1.1.26020.3, and platform version is 4.18.26020.6. Updates are automatically delivered via Windows Update, but can also be manually initiated or deployed using standalone installer packages. The update supports legacy platforms, including Windows 7 and Windows 8.1, provided they have SHA-2 code signing support enabled. Additionally, updates to the Network Inspection System (NIS) are available for certain environments.
Winsage
September 8, 2025
A vulnerability in the Windows Defender update process allows users with administrator privileges to disable the security service and manipulate its files. This flaw enables attackers to create a symbolic link (symlink) with a higher version number that redirects the Defender service to a folder they control. The attacker can then execute malicious actions, such as introducing harmful code or deleting executable files, effectively disabling the service and exposing the system to threats.
Winsage
August 18, 2025
Recent updates for Windows 11 and Windows 10 have caused significant stability issues linked to a bug in the Microsoft Defender update, making some solid-state drives (SSDs) and hard drives (HDDs) unreadable. The issue was first reported by a user on Twitter and affects drives that contain the Windows operating system, leading to potential system failures. The problem is particularly prevalent in the latest 24H2 versions of Windows 11 and several updates for Windows 10. It appears to be associated with certain drives using a specific NAND controller from Phison. The bug is triggered during heavy write sessions to NVMe SSDs and HDDs, especially when writing or backing up data exceeding 50 gigabytes. The range of affected drive models is unclear, and users are uncertain about potential solutions, including firmware updates.
Search