deletion

Winsage
September 24, 2026
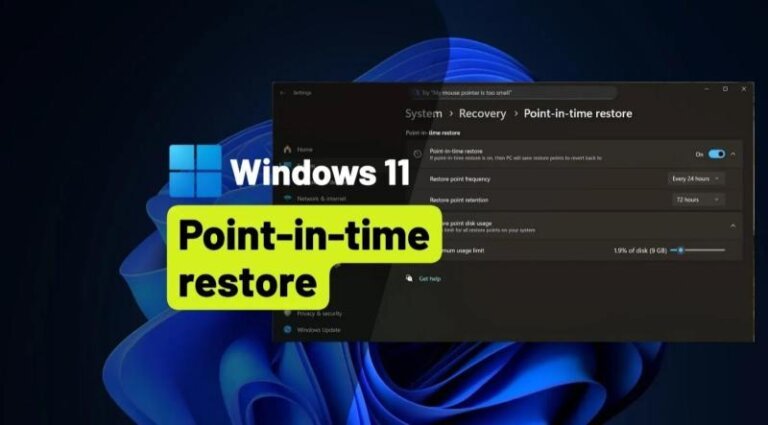
The Point-in-Time Restore feature in Windows 11 allows users to revert their system to a previous state, but it may result in the loss of recently created files. This feature captures the system's state, including Windows system files, installed applications, and local settings. Restore points are generated automatically every 24 hours, but users can create them manually. However, restoring can erase new documents, recently installed applications, and any settings changes made since the last restore point. Files stored in OneDrive remain unaffected. To verify Point-in-Time Restore settings, users must access the Settings application, select System, and then Recovery. Restore points are retained for up to 72 hours and may be deleted sooner if storage is limited. Windows 11 version 26H2 enables this feature by default for devices with an OS volume of at least 200 GB. Before restoring, users should back up recent work to an external drive. To initiate the restore, access the Windows Recovery Environment, select Troubleshoot, and then Point-in-Time Restore. If files are lost after a restore, 4DDiG Data Recovery Software can help recover deleted files. It scans local drives for files deleted during a rollback or accidental deletion. A robust recovery plan should include using Point-in-Time Restore, OneDrive for daily file protection, and separate backups before significant system changes.

Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
AppWizard
September 5, 2026
The City Council will examine Mayor Mamdani's administration's use of a secretive encrypted messaging channel for media relations, which connects nearly 200 social media influencers. This discussion is scheduled for a hearing on September 22. Queens Councilman Phil Wong plans to introduce legislation requiring influencers to label posts for city agency campaigns with a disclaimer stating “Paid for by NYC.” A report revealed that city officials communicated with influencers through a Signal app group titled “NYC Creators Announcements,” sharing updates and multimedia content. Some influencers received payment for their involvement, while others supported the mayor's agenda for personal growth. Concerns have been raised about the Signal chat potentially violating record-keeping regulations due to auto-deletion of messages. The identities of the influencers and details of their contracts remain undisclosed. Wong's proposed bill aims to reveal any undisclosed payments to influencers and raise questions about the integrity of the administration's use of external promoters. Critics argue that the administration's secrecy calls for greater transparency in public relations expenditures.
Winsage
August 28, 2026
An ASUS ROG Zephyrus G14 owner reported that after using Eco Mode for several weeks, Windows 11 removed the NVIDIA GeForce RTX 5070 Ti GPU driver when switching back to performance mode. This behavior is expected due to Windows 11's automatic driver removal for inactive GPUs, managed by a maintenance task called pnpclean.dll, which cleans up drivers for devices not connected for 15 to 30 days. After the driver was deleted, the GPU was recognized as a generic display adapter, requiring reinstallation of the driver. The user found a workaround by disabling the Disk Cleanup handler in PowerShell to prevent automatic deletion, but this increased storage usage as Windows would no longer purge old driver packages.
Winsage
August 24, 2026
The configuration reveals a sequence of actions including file and directory deletions, relocations, and registry operations, such as deleting and modifying registry keys and values. The file-move primitive can transform into an arbitrary file-write capability when directed to the System32 directory. The automation of these actions is achieved through a tool called BTRCLI, which extracts a legitimate driver from Windows Defender, constructs an encrypted transaction, and loads the driver, using the target machine's version of BTR.sys to avoid external drivers.
Search