deletion

Tech Optimizer
October 10, 2026
Raymond Chen, a Microsoft veteran, advises against installing multiple antivirus solutions on the same system due to conflicts that arise, such as each program attempting to quarantine the other's processes. This can lead to significant performance issues and erratic behavior in Windows. Microsoft has stated that Windows Defender is sufficient for most users, highlighting its comprehensive security features in Windows 11. The company warns that running multiple real-time antivirus programs can increase resource consumption and conflict likelihood. Independent testing has shown that Microsoft Defender ranks highly among antivirus solutions.
Winsage
October 3, 2026
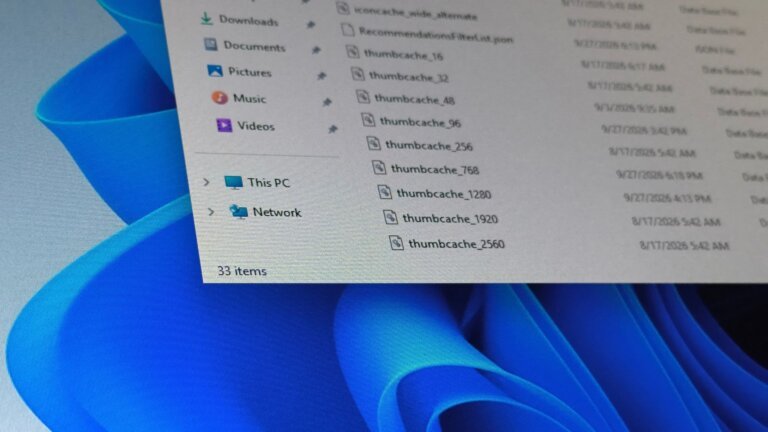
Windows 11 uses a thumbnail caching mechanism to store previews of images in specific databases located in %LocalAppData%MicrosoftWindowsExplorer, such as thumbcache32.db and thumbcache1024.db. When a user deletes an image, the corresponding thumbnail may remain in the cache, as deletion does not automatically remove it from the thumbnail database. The cache retains only reduced versions of images, not the original files, which is significant in digital forensics where thumbnails can provide insights even when original files are missing. Users can manage their thumbnail cache using the cleanmgr tool to clear saved thumbnails or disable thumbnail caching through the Local Group Policy Editor or File Explorer settings.
AppWizard
September 30, 2026
Google Photos is introducing a “Delete all” button in its Remember List feature, allowing users to remove all previously shared entries at once. This feature, found in the top-right corner of the Remember List interface, will include a confirmation prompt before data is permanently erased. Currently, users can only delete individual entries. Additionally, a “Regenerate Image” option is being developed for the AI wardrobe tool. The introduction of these features aims to enhance user control and experience.
Winsage
September 28, 2026
Windows retains thumbnails in a cache file named thumbcache_256.db, but it does not save a thumbnail of every deleted photo. Other operating systems, including macOS and Linux, also use thumbnail caching. Users can access their thumbnail cache by navigating to %LOCALAPPDATA%MicrosoftWindowsExplorer, but this will not show deleted images. Thumbnails are created only when images are displayed in Explorer’s thumbnail view. Windows allows users to clear the thumbnail cache using the Disk Cleanup tool, and there is an option to disable thumbnail caching in Windows 11 Pro and higher. The cached thumbnails do not guarantee persistence and do not represent original files. Windows also keeps records of application launches in Prefetch, maintains entries for USB devices in the USBSTOR registry key, saves Wi-Fi networks and passwords, and can keep clipboard history and recent file shortcuts.
Winsage
September 28, 2026
A recent post on X claims that Windows retains a thumbnail of every deleted photo in a file named thumbcache_256.db, which has raised privacy concerns among users. While Windows does maintain a thumbnail cache for efficiency, this practice is not unique to Windows, as other operating systems like macOS, Linux, and Android also use similar systems. Users can inspect or clear their thumbnail cache by accessing specific database files in the Windows Explorer directory. The claim that Windows retains "every photo you’ve ever deleted" is misleading, as thumbnails are only created when images are viewed in thumbnail mode. Windows does not cache every file, and thumbnails must exist before they can be cached. Additionally, Windows keeps app launch records in Prefetch files for performance optimization, maintains entries for USB devices in the USBSTOR registry key, retains records of Wi-Fi networks and passwords (which are encrypted), and can keep clipboard history and recent file shortcuts. Caching previews is common across various operating systems, and Microsoft is focused on user consent and privacy as it enhances Windows 11 with AI functionalities.
Winsage
September 24, 2026
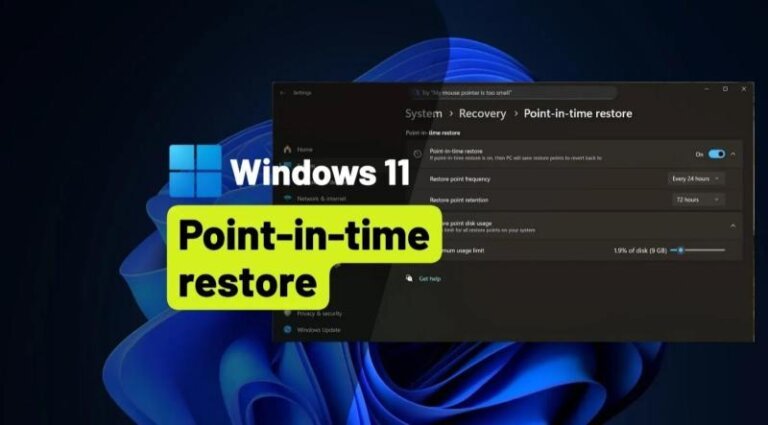
The Point-in-Time Restore feature in Windows 11 allows users to revert their system to a previous state, but it may result in the loss of recently created files. This feature captures the system's state, including Windows system files, installed applications, and local settings. Restore points are generated automatically every 24 hours, but users can create them manually. However, restoring can erase new documents, recently installed applications, and any settings changes made since the last restore point. Files stored in OneDrive remain unaffected. To verify Point-in-Time Restore settings, users must access the Settings application, select System, and then Recovery. Restore points are retained for up to 72 hours and may be deleted sooner if storage is limited. Windows 11 version 26H2 enables this feature by default for devices with an OS volume of at least 200 GB. Before restoring, users should back up recent work to an external drive. To initiate the restore, access the Windows Recovery Environment, select Troubleshoot, and then Point-in-Time Restore. If files are lost after a restore, 4DDiG Data Recovery Software can help recover deleted files. It scans local drives for files deleted during a rollback or accidental deletion. A robust recovery plan should include using Point-in-Time Restore, OneDrive for daily file protection, and separate backups before significant system changes.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Search