Today on Google Play, notable app and game deals include:
- Easy Delivery Co. - A simulation game.
- Human Fall Flat - A physics-based puzzle platformer.
- FrogBoy - An adventure game.
- Kingdom Rush 5: Alliance TD - A tower defense game.
- Kingdom Rush Vengeance TD Game - Another tower defense game in the Kingdom Rush series.
- MAYATCH - A puzzle game.
- Cyberlords – Arcology PREMIUM - An RPG set in a futuristic world.
- Laser Tanks: Pixel RPG - A pixel art RPG.
Additionally, TCL NXTPAPER Android phones are available at discounts of up to 30%.
HSBC has restricted its Android app from functioning within Samsung's Secure Folder and Android's Private Space, causing many customers to lose access to online banking services. The bank described this as a "proportionate security control" to mitigate risks, stating that customers must use the app outside these environments. Feedback from users has been largely negative, with complaints about abrupt access loss and inadequate communication regarding the changes. Customers are unable to utilize web banking due to the app's requirement for multifactor authentication, and some have raised concerns about HSBC's compliance with the Financial Conduct Authority's Consumer Duty. HSBC has advised customers to access the app outside of protected spaces and mentioned the option of using a Physical Secure Key for desktop banking.
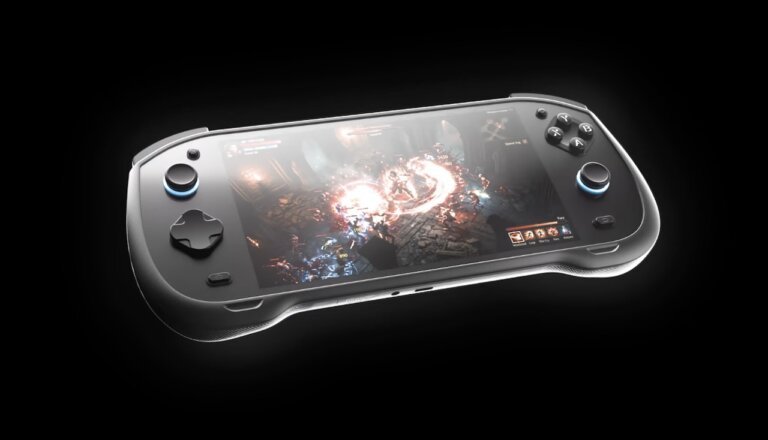
The X1 handheld gaming device uses Qualcomm's Snapdragon G2 Gen 2 Gaming Platform with 8GB of memory and 128GB of storage, expandable up to 1TB. It features a 7-inch 120Hz display and OwlOS software for a controller-first interface. The device also includes TMR sticks for precise control and a 9,300mAh battery for long gaming sessions. The price for the X1 is ₹29,500 for the Community Batch Drop, with reservations starting in October 2027.
Microsoft Office Professional Plus 2019 is available for .97, down from its regular price of 9. This offer is valid until September 27 and provides a lifetime license for one Windows PC, with no recurring fees. The suite includes applications such as Word, Excel, PowerPoint, Outlook, OneNote, Publisher, and Access, and features enhanced inking capabilities, new analytical tools in Excel, upgraded PowerPoint features, and improved Outlook functionalities. Users receive an immediate email with the download link and license key, which must be redeemed within seven days. The offer supports all languages and includes updates for the 2019 version.
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
A keylogger captures every keystroke made on a device and sends that information to an external source. In 2025, infostealer malware, including keyloggers, resulted in the theft of 642.4 million credentials from 13.2 million infections globally. In Australia, approximately 30,000 banking passwords were compromised between 2021 and 2025 due to this malware. The Australian Cyber Security Centre reported over 42,500 calls related to credential theft in one year, a 16% increase. Four main malware families dominate the landscape, with LummaC2 accounting for nearly 60% of credentials linked to infostealers in 2026. Keyloggers can be detected through signs such as typing lag, unexpected antivirus notifications, new browser extensions, and unexplained spikes in outbound data usage. Detection and removal steps include checking running processes, auditing startup programs, reviewing installed programs, running antivirus scans, and resetting passwords from a clean device. Keyloggers can infiltrate systems via phishing emails, malicious attachments, or compromised software downloads. Mobile devices can also be targeted by keyloggers disguised as legitimate apps.
Valve has open-sourced Lepton, an Android compatibility layer for the Steam Frame headset, allowing VR developers to adapt existing Android games for the device. The code is available on Valve's GitLab repository and facilitates the transition without needing to reconstruct games for a different platform. Lepton is designed to create a game-optimized Android environment rather than transforming the Steam Frame into a general Android device. It disables unnecessary Android services to maintain efficiency and integrates with the SteamOS host system, supporting various graphics stacks and Vulkan tools for enhanced VR gaming. Lepton operates without requiring root access, with each process running as a non-root user, and provides developers with tools for debugging and performance profiling. The open-sourced code offers insight into Valve's approach to supporting Android games on SteamOS.
Google has launched Android Bench 2.0, an upgraded benchmark for evaluating AI coding agents, which now includes 30 long-horizon tasks that can take human engineers days or weeks to complete. The best pass rate for these tasks is around 28%, down from approximately 91% in the previous version. The benchmark measures both pass rates and completion rates, acknowledging partial progress rather than just failures. It assesses various challenges, including app creation and feature integration, using a comprehensive scoring methodology that evaluates functionality, regression checks, and visual fidelity. AI models perform better with new code than with modifications to existing systems, facing challenges in runtime validation and cross-platform conversions. The current leaderboard shows OpenAI’s GPT-6 Astra leading with a 28% pass rate, while Gemini 3.8 Flash has an 8% pass rate. Developers using AI agents should be aware that while AI can generate significant portions of applications, further refinements will require human input. The benchmark is available on Google’s Android Bench leaderboard.
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures.
RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands.
The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure.
The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions.
GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.