deployment

AppWizard
September 23, 2026
The Android development community has historically addressed memory optimization reactively, but new performance requirements from Google Play, effective February 2027, emphasize proactive memory management. These requirements include metrics for dynamic memory usage, bitmap memory, and DEX code optimization, with apps needing at least 25% optimization coverage. Memory usage can now hinder releases even without local crash replication, necessitating its integration into the pre-production process alongside other performance metrics. Dynamic memory usage is defined as anonymous RSS plus swap, excluding file-backed data. Google Play will evaluate this across different application states and device performance categories. Bitmap memory is scrutinized for the retention of invisible bitmaps, and DEX optimization aims to reduce memory footprint and improve performance. Investigating memory growth involves using Android Studio’s Memory Profiler to monitor memory changes during specific user flows and conducting heap dumps to identify retained objects. Issues often arise from retained state, where components hold onto callbacks that reference image data, necessitating a focus on lifecycle management rather than merely cache size. Bitmap memory should be carefully managed, as the decoded size can significantly exceed the compressed file size. Downsampling images to match UI dimensions is crucial. Memory checks should occur before production, with a focus on establishing a memory budget based on actual measurements and defining representative memory scenarios for testing. A pre-release memory checklist includes running user flows repeatedly, testing on various devices, inspecting heap dumps, examining image configurations, and reviewing optimization metrics. Monitoring Android vitals and Play Console warnings is essential to detect potential issues before they lead to user-reported crashes.
Tech Optimizer
September 16, 2026
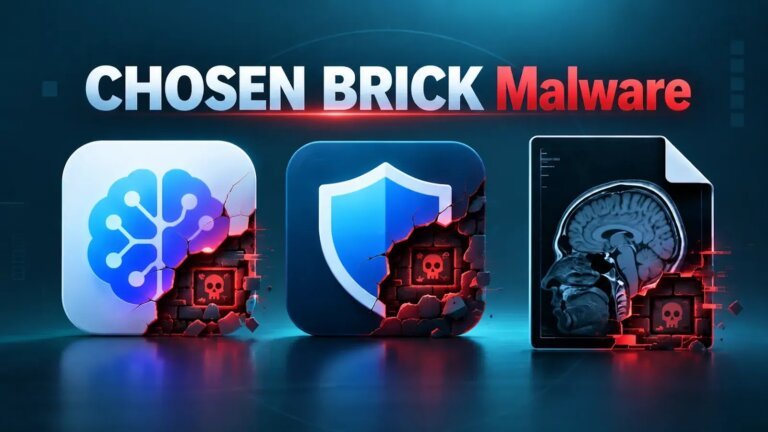
Iranian state-affiliated cyber actors are targeting dissidents, activists, and journalists using fake AI applications, counterfeit antivirus tools, and fabricated MRI scan results, primarily through a spyware family known as CHOSEN BRICK, which is designed for Windows systems. This campaign has been active since at least 2025 and affects individuals globally, including in the UK, US, and Netherlands. The malware establishes persistence via the Windows Registry Run key and communicates through Telegram, utilizing unique Bot IDs for each victim. CHOSEN BRICK is capable of extensive data collection, including capturing screenshots, recording audio, and stealing email content. Personal information from victims has been found on pro-Iranian leak sites, increasing harassment risks. Security measures should include monitoring for suspicious Registry entries and unusual communications, while users are advised to avoid unsolicited software installations and keep their systems updated. The FBI refers to this malware family as HEAVYGRAM.
Winsage
September 16, 2026
Organizations using Windows Server 2022 will lose mainstream support on October 13, 2026, although security updates will continue through extended support until October 2031. Customers are encouraged to plan for an upgrade to Windows Server 2025 to avoid potential security vulnerabilities and complications in future migrations. Microsoft recommends early evaluation and testing of Windows Server 2025 to ensure compatibility and smooth transition. Additionally, support for the Azure Edition’s hotpatching capability has been extended to October 2027, providing some customers more time to strategize their migration. However, remaining on Windows Server 2022 means missing out on new features and enhancements.
Winsage
September 16, 2026
Microsoft has announced that mainstream support for Windows Server 2022 will end next month, transitioning to an extended support phase that lasts until October 2031. Windows Server 2022 was released in September 2021 and will receive its final mainstream support update on October 13, 2026. After this date, it will continue to receive essential security updates at no extra cost until October 14, 2031. Hotpatching for Windows Server 2022 will be available until October 2027 for Datacenter: Azure Edition. Microsoft encourages administrators to upgrade to Windows Server 2025, which began rolling out to Windows Insiders in January 2024 and is expected to be generally available by November 2024. Windows Server 2025 will have mainstream support until November 13, 2029, followed by five years of extended support until November 14, 2034. A 180-day trial of Windows Server 2025 is available through the Microsoft Evaluation Center.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Search