device

AppWizard
September 18, 2026
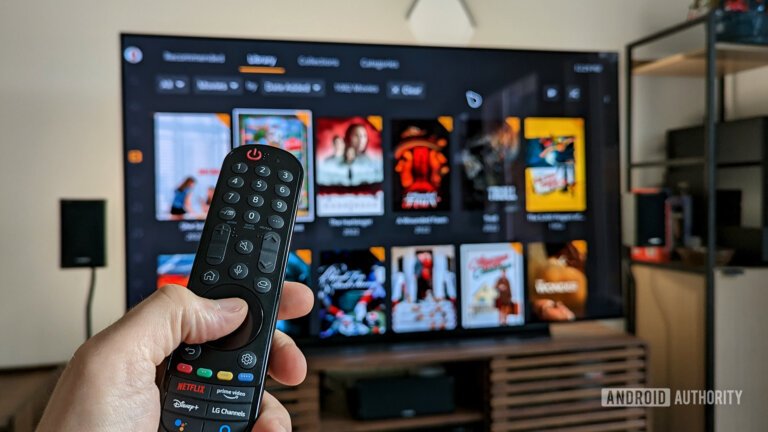
A new open-source Plex client named PlxNative has been developed for older LG TVs running on webOS to improve the browsing experience of Plex libraries. It operates independently of a web browser using a native Rust/OpenGL interface, allowing it to launch in about one second and ensuring fluid scrolling and menu navigation. PlxNative supports various Plex functionalities, including library browsing, profile switching, audio and subtitle selection, and direct play or server transcoding. It does not replace the TV's built-in video decoder and connects directly to the Plex Media Server over the local network after initial sign-in. Installation options include the Homebrew Channel or sideloading via LG’s Developer Mode, which requires periodic session renewals. The developer has submitted PlxNative for official review by LG.
AppWizard
September 18, 2026
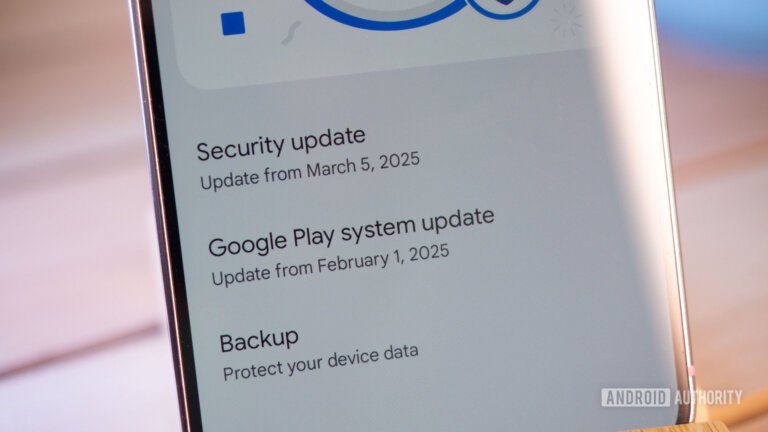
Google has launched the AndroidX Security State and Security State Provider libraries, enhancing Android's security framework. These tools allow applications to assess the security status of individual components on a device, rather than relying solely on the overall security patch level. Applications can now verify specific security fixes, identify available updates, and check for pending installations. This is particularly useful for security-sensitive applications, such as banking software, which can confirm the presence of necessary security fixes before allowing transactions. The libraries also enable apps to check for the resolution of specific vulnerabilities (CVEs), ensuring critical fixes are in place before enabling features like tap-to-pay. Phone manufacturers can communicate specific security fixes without changing the overall security patch date, meaning a device may show an outdated patch date while still having resolved certain vulnerabilities.
AppWizard
September 18, 2026
The new AndroidX Security State libraries, with stable releases of Security State v1.1.0 and Security State Provider v1.0.0, allow developers to evaluate the security status of individual device components. They provide three levels of security patch information: Device Security Patch Level (DSPL), Published Security Patch Level (PSPL), and Available Security Patch Level (ASPL). These libraries enable checks on critical components of the Android operating system, including system modules and the Linux kernel, which are represented by version numbers rather than monthly patch dates. Applications that prioritize security can utilize this detailed patch information to assess vulnerabilities, particularly those tracked as Common Vulnerabilities and Exposures (CVEs). The libraries also integrate with the Open Source Vulnerabilities (OSV) database for access to Android Security Bulletin data and device-specific vulnerability reports. Additionally, Android 17 allows manufacturers to declare individual security fixes beyond the stated security patch level, and Google is working with manufacturers to transition their OTA update clients to this new standardized system.
Winsage
September 18, 2026
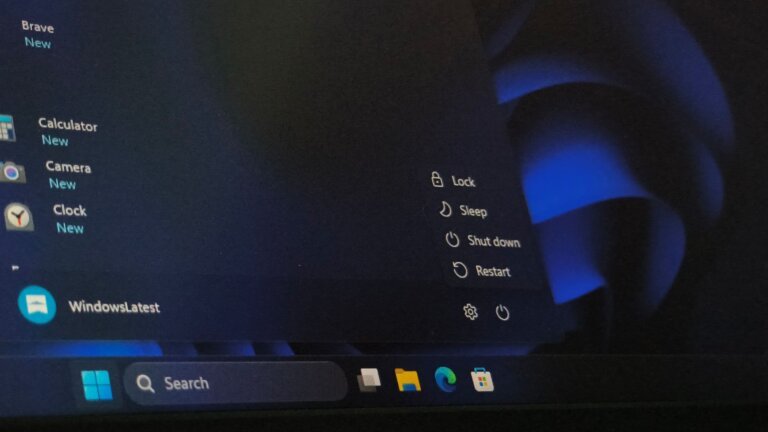
The Fast Startup feature in Windows, enabled by default, allows the kernel session to remain hibernated during shutdown, which results in quicker boot times by restoring a saved state. In contrast, selecting Restart clears the kernel session entirely, performing a complete boot of Windows. The process of shutting down with Fast Startup involves closing applications, logging off, keeping the kernel loaded in memory, saving the kernel and drivers to hiberfil.sys, and powering off, while Restart closes applications, logs off, ends the kernel session, and reboots immediately without saving a kernel snapshot. Fast Startup can lead to persistent issues from previous sessions, making Restart a better option for troubleshooting. To perform a full shutdown bypassing Fast Startup, users can execute the command "shutdown /s /t 0." Microsoft advises against permanently disabling Fast Startup, as it enhances shutdown-to-boot transitions.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Search